About Us Contact Blog
Governance DocsGovernance Docs
Which Toolkit?SoA GeneratorFree TemplatesGap AssessmentsBusiness Impact AnalysisAboutBlogContactMy AccountCart
FOX v.2.4.9
Browse Toolkits
Governance Docs
  • Browse All Toolkits
  • Information Security & Cybersecurity
  • Data Privacy & Protection
  • Governance, Risk & Compliance
  • Quality Management
  • Health, Safety & Environment
  • AI Governance

My Account

CART

No products in the cart.

Author: Governance Docs

Governance Docs LLC

Phishing-resistant MFA methods compared against NIST SP 800-63B-4 assurance levels

Phishing-Resistant MFA: The Complete 2026 Guide

Governance Docs20th August 2026

Phishing-resistant MFA under NIST SP 800-63B-4: which methods qualify, what AAL2 and AAL3 each require, and why synced…
Read More
Cybersecurity governance obligations under NIS2, DORA, ISO 27001 and NIST CSF 2.0

Cybersecurity Governance: The Definitive 2026 Board Guide

Governance Docs20th August 2026

Cybersecurity governance after NIS2: what boards must approve, why NIST CSF 2.0 added a 6th function, and the…
Read More
Clean desk policy rules for ISO 27001 Annex A 7.7 clear desk and clear screen

Clean Desk Policy: 9 Essential Rules for 2026

Governance Docs20th August 2026

A clean desk policy that passes an ISO 27001 audit: what Annex A 7.7 requires, the 9 rules…
Read More
BYOD policy requirements mapped to ISO 27001:2022 Annex A controls

BYOD Policy: The Essential 2026 Guide for ISO 27001

Governance Docs20th August 2026

A BYOD policy that survives an ISO 27001 audit: the 7 Annex A controls it satisfies, the 9…
Read More
PCI DSS documentation and evidence checklist for v4.0.1 assessments

PCI DSS Documentation: The Complete 2026 Evidence Checklist

Governance Docs20th August 2026

PCI DSS documentation a QSA actually asks for: the 12 requirement areas, the 51 future-dated controls effective 31…
Read More
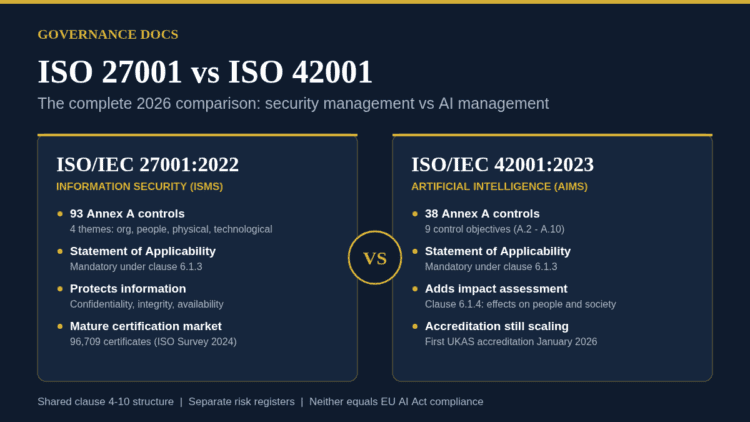
ISO 27001 vs ISO 42001 comparison chart showing 93 security controls against 38 AI controls

ISO 27001 vs ISO 42001: The Complete 2026 Comparison Guide

Governance Docs20th August 2026

ISO 27001 vs ISO 42001 compared for 2026: 93 security controls versus 38 AI controls, the shared clause…
Read More
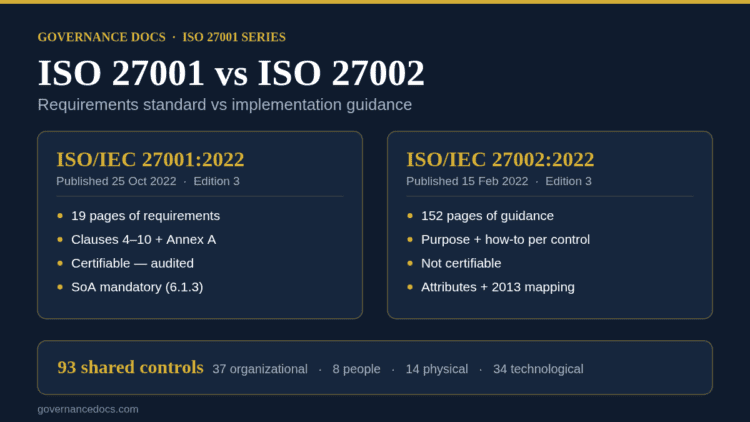
ISO 27001 vs ISO 27002 comparison chart showing the 19-page requirements standard against the 152-page implementation guidance

ISO 27001 vs ISO 27002: The Complete 2026 Guide to Which One You Need

Governance Docs19th August 2026

ISO 27001 vs ISO 27002 explained: one is a 19-page certifiable requirements standard, the other 152 pages of…
Read More
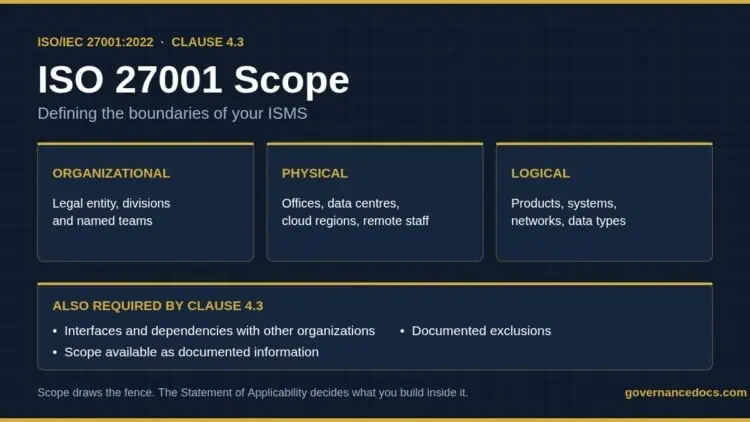
ISO 27001 scope diagram showing organizational, physical and logical ISMS boundaries under Clause 4.3

ISO 27001 Scope: The Complete 2026 Guide to Defining Your ISMS

Governance Docs18th August 2026

Your ISO 27001 scope decides your audit days, your workload and what your certificate says. Clause 4.3 rules,…
Read More
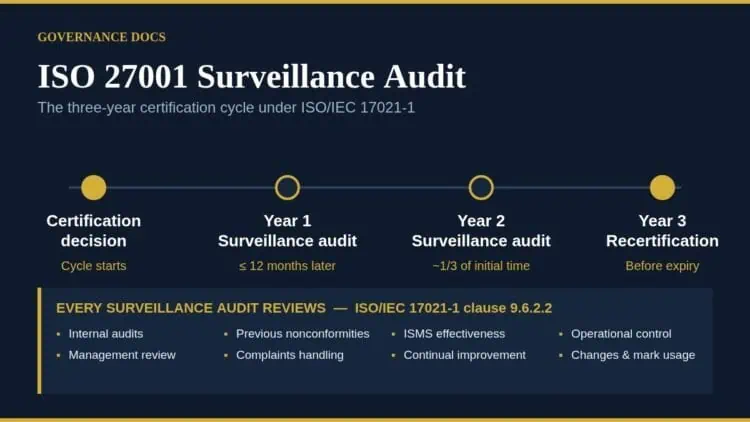
ISO 27001 surveillance audit timeline showing the three-year certification cycle

ISO 27001 Surveillance Audit: The Complete 2026 Guide

Governance Docs17th August 2026

What an ISO 27001 surveillance audit covers, when it is due, what it costs in 2026, and how…
Read More
How to weight the clauses in an ISO 22301 gap analysis

ISO 22301 Gap Analysis: 6 Proven Rules for a Plan That Lands

Governance Docs16th August 2026

Clause 8.2 carries everything built on top of it, and 8.5 cannot be closed on paper. How to…
Read More
What each ISO 27001 certification audit stage tests in a readiness assessment

ISO 27001 Readiness Assessment: 6 Proven Checks

Governance Docs16th August 2026

A gap analysis asks what is missing. A readiness assessment asks whether you would pass Stage 2 —…
Read More
What the ePrivacy Directive and the GDPR each require for cookie consent

Cookie Consent: 6 Proven Rules Article 5(3) Sets

Governance Docs16th August 2026

The rule never says cookies and never says personal data. What Article 5(3) covers, the two exemptions read…
Read More

    ←
  • 1
  • …
  • 46
  • 47
  • 48
  • 49
  • 50
  • …
  • 68
  • →

Recent Posts

Infographic answering is ISO 13485 worth it in 2026 with audit days, QMSR date and MDSAP regulators
Is ISO 13485 Worth It? The Complete 2026 Cost-Benefit Case

September 25, 2026

Is ISO 42001 worth it in 2026 — audit days, first-year cost and Annex A controls at a glance
Is ISO 42001 Worth It? The Complete 2026 Cost-Benefit Case

September 25, 2026

Is SOC 2 worth it in 2026 — typical first-year cost, annual report cycle and attestation status
Is SOC 2 Worth It? The Complete 2026 Cost-Benefit Case

September 24, 2026

ISO 21502 vs PMBOK 8 comparison: the 2020 project management guidance against PMI six principles, five Focus Areas and seven Performance Domains
ISO 21502 vs PMBOK 8: The Complete 2026 Guide for Project Governance

September 24, 2026

ISO 31000 vs ISO 27005 comparison: 2018 risk management guidelines against the 2022 information security risk guidance
ISO 31000 vs ISO 27005: The Definitive 2026 Guide

September 24, 2026

Categories

  • Articles
  • DORA
  • GDPR
  • HIPAA
  • ISO 27001
  • ISO 42001 & AI governance
  • ISO 9001
  • Management systems
  • NIS2
  • Security frameworks
  • SOC 2
Governance DocsGovernance Docs

Reliable ISO & compliance documentation toolkits that help your business meet regulatory standards with ease.

Governance Docs LLC
1209 Mountain Road Pl NE, Suite R
Albuquerque, NM 87110, USA
info@governancedocs.com
+1 812 227 5662

Toolkits

  • ISO 27001:2022
  • GDPR
  • SOC 2
  • PCI-DSS v4.0
  • HIPAA
  • ISO 42001
  • All toolkits →

Company

  • About Us
  • Blog
  • Contact
  • FAQ
  • Which toolkit do I need?
  • Free templates
  • SoA generator
  • Gap assessments
  • Business impact analysis
  • RSS feeds

Policies

  • Privacy Policy
  • Terms & Conditions
  • Refund & Return Policy
  • Delivery Policy
  • Manage cookies
Browse by topicISO 27001ISO 42001 & AI governanceGDPRSOC 2HIPAANIS2DORAISO 9001Management systemsSecurity frameworks
© 2026 Governance Docs LLC. All rights reserved.
Secure checkoutstripeVISA