
CART
No products in the cart.
ISO Compliance Insights & Best Practices
The ISO 27001 certification logo you are about to put in your website footer probably does not exist in the form you think it does. Marketing asks for “the ISO logo,” the certificate arrives with three different graphics on it, and somewhere between the two a claim gets published that the certification body is contractually obliged to make you take down.
This guide sorts out which graphic belongs to whom, which of them an ISO 27001 certification logo really refers to, what you are licensed to display, and the exact wording that keeps a security badge defensible in a tender response. The rules come from three places: ISO’s own trademark position, ISO/IEC 17021-1:2015 clause 8.3, and the conditions your accreditation body attaches to its symbol.
Free gap assessment
Where do you actually stand against ISO 27001?
Score every management system clause and all 93 Annex A controls, free, and get a prioritised gap list back.
Run the free ISO 27001 gap assessment → or View premium report sample
Start with the single fact that invalidates most of what is published on this subject. ISO does not certify anyone. In its own words on the ISO certification page, ISO “does not perform certification or issue certificates, and it does not permit anyone to use the ISO logo in connection with certification.” There is no official ISO 27001 certification logo issued by ISO, because ISO is not a party to your certification at all.
The ISO logo and the short name “ISO” are registered trademarks in over 100 countries, and ISO treats them as well-known marks. Use is restricted to ISO, its member bodies and its technical committees. ISO’s published guidance for everyone else is blunt: do not use or copy the logo, do not modify it, do not use a modified version, do not register “ISO” in a domain or company name, do not use “ISO” in a product or service name, and do not state that you or your products are endorsed, approved or certified by ISO. ISO has backed this up with national trademark actions, DMCA takedowns and WIPO domain disputes.
What you actually receive when you certify is narrower and more useful: a licence to display your certification body’s own certification mark. ISO/IEC 17021-1:2015 clause 8.3.1 requires every certification body to maintain rules for that mark. It must be traceable back to the certification body, it must be unambiguous, the mark or its accompanying text must identify the type of certification, and it must not appear on a product, on product packaging, or in any way that could be read as product conformity. Your ISO 27001 certification logo, in other words, is your certification body’s logo.
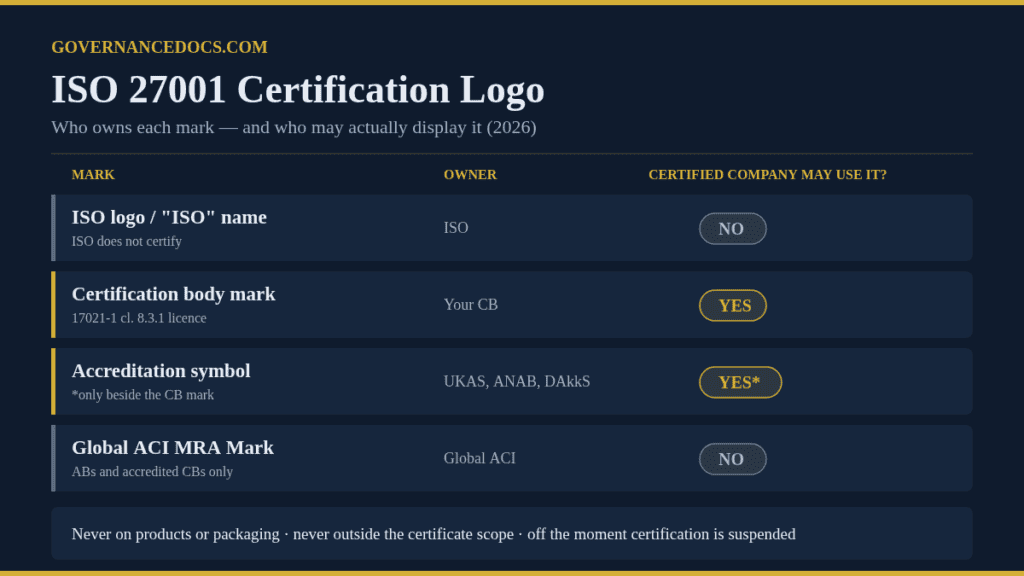
Four graphics circulate under the loose heading of an ISO 27001 certification logo, and only two of them are ever yours to use. Getting the ownership straight is the whole job.
| Graphic | Owner | May a certified company display it? | Governing rule |
|---|---|---|---|
| ISO logo / the word “ISO” as a mark | ISO | No. ISO, its members and its technical committees only | ISO trademark policy; ISO does not permit its logo in connection with certification |
| Certification body’s certification mark (BSI, DNV, Intertek, Schellman and so on) | The certification body | Yes, under the licence in your certification agreement | ISO/IEC 17021-1 clause 8.3.1 and 8.3.4 |
| Accreditation symbol (UKAS, ANAB, DAkkS and other national bodies) | The accreditation body | Usually yes, but only alongside the certification body’s mark | The accreditation body’s conditions of use |
| Global ACI MRA Mark (successor to the IAF MLA Mark) | Global ACI | No. Accreditation bodies and accredited conformity assessment bodies only | Global ACI MRA Mark policy; use is optional, not mandatory |
That last row is new ground for 2026. Global ACI has taken over the roles previously held by the International Accreditation Forum and ILAC, and its MRA Mark replaces the IAF MLA Mark. Global ACI states that accreditation bodies may use the MRA Mark to show signatory status, and that conformity assessment bodies accredited by a signatory may use it in combination with the accreditation symbol on their reports, certificates or statements. Certified clients are not in that list. Use is also optional, so a certificate is not defective for lacking it.
Your certificate itself will carry several of these marks, and that is correct. Clause 8.2.2(g) requires the certification document to show the name, address and certification mark of the certification body, and permits other marks, naming the accreditation symbol and the client’s own logo as examples, provided they are not misleading or ambiguous. A certificate with four graphics on it is normal. Your website footer is a different question.
The permitted surfaces for an ISO 27001 certification logo are the ordinary business ones: letterhead and stationery, brochures and literature, your website, advertising, email signatures, proposals and tender responses. Clause 8.3.4(a) binds you by legally enforceable agreement to follow your certification body’s rules when you reference your certification status in communication media such as the internet, brochures, advertising or other documents, so the certification body’s brand guide is the operative document and it is usually sitting in their client portal.
Three conditions travel with the mark everywhere it goes. First, the reference has to make clear that the certification covers a management system, not a product, process or service. Clause 8.3.3 sets out what a statement has to include: the identity of the certified client, the type of management system and the applicable standard, and the certification body that issued the certificate. Second, clause 8.3.4(g) forbids implying that certification applies to activities and sites outside the scope on the certificate, which is the trap for any company that certified one platform and then put the badge on the corporate homepage. Third, clause 8.3.2 bars the certification body from letting you apply its marks to laboratory test, calibration or inspection reports or certificates at all.
Clause 8.3.4 adds four more obligations that read like a list of the things companies actually do wrong: no misleading statements about your certification, no misleading use of the certification document or any part of it, no implication that the certification body certifies a product or process, and nothing that would bring the certification body or the certification system into disrepute.
An ISO 27001 certification logo stops at the product boundary, and that is the line hardest to police. The accreditation bodies express it in unusually specific terms. The UK conditions of use, as implemented in certification bodies’ own client instructions, exclude from “publicity material” any notice, label, document or written announcement affixed to or appearing on goods or products, unless those goods were made under an accredited product conformity scheme. The same exclusion extends to primary packaging, blister packs being the stock example, and to promotional products.
| Surface | Certification body’s mark | Accreditation symbol (UKAS conditions) |
|---|---|---|
| Website, brochures, letterhead, advertising | Permitted under the certification body’s licence | Permitted, only next to the certification body’s mark |
| Product, product packaging, blister packs, promotional items | Prohibited by clause 8.3.1 | Excluded from publicity material |
| Vehicles | Certification body’s rules apply | Not permitted on any vehicle |
| Buildings and flags | Certification body’s rules apply | Not permitted |
| Internal walls, doors, exhibition stands | Certification body’s rules apply | Permitted |
| Laboratory test, calibration or inspection reports | Prohibited by clause 8.3.2 | Separate accreditation applies |
Where the accreditation symbol is permitted, it comes with mechanical rules that are easy to breach in a design review. Under the UKAS conditions, a certified organisation may use the symbol only in conjunction with its certification body’s symbol; the accreditation symbol must not be larger than the certification body’s symbol and must never appear in isolation from it. Reproduction is specified too: black and white, or the purple and white scheme at Pantone 2685 C, or a single colour matching the predominant ink colour of the document, at a size that keeps every feature distinguishable, normally a minimum height of 20 mm, with no distortion or infilling. Other national accreditation bodies publish their own equivalents, so confirm the conditions that apply to yours rather than assuming the UK set travels.
An ISO 27001 certification logo that was accurate at sign-off becomes a liability the moment the certificate moves, and the obligations here are contractual rather than advisory.
Suspension is the sharpest case. Clause 9.6.5.2 lets the certification body suspend when a client fails to meet certification requirements, refuses to allow surveillance or recertification audits at the required frequency, or asks for suspension voluntarily. Clause 9.6.5.3 then states the position plainly: under suspension, the client’s management system certification is temporarily invalid. Advertising it during that window is advertising something that does not currently exist. Clause 9.6.5.4 restores the certification once the issue is resolved and withdraws or reduces scope if it is not, with a note that suspension would not normally exceed six months. Our guide to ISO 27001 certificate validity covers the cycle dates behind this in more detail.
On withdrawal, clause 8.3.4(d) requires you to discontinue all advertising matter containing a reference to certification, as directed by the certification body. On a scope reduction, clause 8.3.4(e) requires you to amend all advertising matter — every page, deck and signature block, not just the certificate page.
Enforcement is not theoretical. Clause 8.3.5 requires the certification body to control ownership of its marks and to act on incorrect references to certification status or misleading use of certification documents, marks or audit reports. The note lists the available responses: requests for correction and corrective action, suspension, withdrawal of certification, publication of the transgression, and legal action if necessary. Publication of the transgression is the one worth pausing on, because it is reputational damage administered by the body whose mark you were trying to borrow.
Most of the value in getting the ISO 27001 certification logo question right is in the sentence next to the graphic. ISO’s own guidance asks that standards be referenced in full, and ISO 27001 is a joint publication, so the correct reference is ISO/IEC 27001:2022, not “ISO 27001 standards” or “ISO compliant.”
| Claim to avoid | Why it fails | Defensible version |
|---|---|---|
| “ISO certified” with the ISO logo | ISO does not certify and does not license its logo for certification | “Certified to ISO/IEC 27001:2022 by [certification body], certificate [number]” with that body’s mark |
| “ISO approved” or “ISO accredited” | Neither status exists; accreditation applies to the certification body, not to you | “Certified by [certification body], accredited by [accreditation body]” |
| “Our platform is ISO 27001 certified” | Implies product conformity, contrary to clause 8.3.1 and 8.3.4(f) | “The information security management system covering [named service] is certified to ISO/IEC 27001:2022” |
| Badge on the corporate homepage for a single certified product line | Implies coverage of activities outside the certified scope, contrary to 8.3.4(g) | State the scope line from the certificate alongside the mark |
| Accreditation symbol on its own in the footer | Breaches the conditions of use | Pair it with the certification body’s mark, no larger than that mark |
If you find a competitor misusing a mark, the complaint route is defined. ISO directs complaints about misuse of its logo or false certification claims to the certification body that certified the organisation, which you identify from the statement of certification, the mark being used, or by asking for a copy of the certificate; ISO will respond to a complaint within 14 days and can help facilitate dialogue, without guaranteeing an outcome. False claims of accredited certification, including misuse of the Global ACI logo, go to the Global ACI Secretariat. On the buying side, the same discipline belongs in your supplier file: our note on ISO 27001 supplier assessment covers what to collect beyond a badge, and accredited ISO 27001 certification explains why the accreditation status behind the mark matters more than the mark itself.
No. ISO states that it does not permit anyone to use the ISO logo in connection with certification, and restricts the logo to ISO, its members and its technical committees. If you want a graphic to demonstrate certification, ISO’s own answer is to contact the certification body that issued your certificate.
Yes, with qualification. Clause 8.3.3 expects the statement to identify the certified organisation, the type of management system and the applicable standard, and the certification body that issued the certificate. Name the body, give the certificate number and state the scope, and the claim stands up. A bare “ISO 27001 certified” strapline across a whole corporate site, when only one business unit is in scope, does not.
No. Clause 8.3.1 prohibits use of the mark on a product, on product packaging, or in any other way that may be interpreted as denoting product conformity, and the accreditation conditions exclude goods, primary packaging and promotional products from permitted publicity material. Clause 8.3.3 does allow a carefully worded statement in accompanying information, as long as it cannot be read as certifying the product.
No. Whatever else sits in your ISO 27001 certification logo lockup, accreditation symbols are licensed for use alongside the certification body’s mark, never in isolation, and under the UKAS conditions the accreditation symbol must not be larger than the certification body’s symbol. The symbol is also barred from vehicles, buildings and flags, while internal walls, doors and exhibition stands are permitted.
The certification is temporarily invalid under clause 9.6.5.3, so the mark and every claim built on it have to come down for the duration. If suspension turns into withdrawal, clause 8.3.4(d) requires you to discontinue all advertising matter referring to certification, as directed by the certification body, and clause 8.3.5 gives that body the option of publishing the transgression if you do not.
There is no ISO-issued ISO 27001 certification logo. What exists is your certification body’s mark, licensed to you under a legally enforceable agreement, optionally paired with your accreditation body’s symbol under that body’s size and placement rules, and limited at all times to the management system and the scope printed on your certificate. Keep the graphic off products and packaging, keep the wording tied to ISO/IEC 27001:2022 and the named certification body, and take the badge down the day the certificate is suspended. Everything else in this area is a competitor’s marketing department guessing.
Getting there starts with a certificate you can defend, which means the documented information behind it holds up at stage 2. Our ISO 27001 Toolkit provides 165 templates mapped to ISO/IEC 27001:2022, covering the mandatory documents, the Statement of Applicability, the risk assessment and the full Annex A control set, so your ISMS evidence is ready before the auditor arrives. It is $99 for the complete pack. For the wider route to certification, start with our guide to ISO 27001 certification, and for the primary sources behind this article see ISO’s pages on certification and the ISO name and logo.
Free ISO 27001 risk assessment
Which of your risks sit above your appetite line?
Set your own risk criteria, pick from 61 information security risk scenarios, rate likelihood and impact, and decide how to treat each one. You get a heat map, a process score and the findings an auditor would raise, free.
Run the free risk assessment → or View premium report sample


October 11, 2026

October 11, 2026

October 11, 2026

October 11, 2026

October 11, 2026
