Description
At a glance: the NIST Cyber Risk Management Toolkit is an editable Microsoft Office documentation set built on the NIST SP 800-30 Rev. 1 risk assessment method, with a NIST CSF 2.0 maturity assessment workbook. It covers the 800-30 risk assessment template and report, the risk treatment plan, a cyber security risk management framework, and the security policies and procedures your treatment decisions point to. One-time price $89, instant download, licensed for internal use by one organisation. Implementing for several clients? The Consultant Package covers unlimited client engagements.
About the NIST Cyber Risk Management Toolkit
Last updated 1 November 2026. Version 2: the Word templates now open with a branded full-page cover, and all 61 Word and Excel files share consistent styling: Calibri text, navy headings with gold rules and matching tables. Each Excel workbook opens with a cover sheet and linked contents. Aligned to NIST SP 800-30 Rev. 1 and NIST CSF 2.0.
The NIST Risk Management Toolkit is a set of professional collection of over 50 files covering every facet of information security risk management built on the NIST SP 800-30 risk assessment methodology, with a CSF 2.0 maturity workbook included. This toolkit serves as a complete package to streamline the identification, assessment, treatment, and monitoring of security risks within an organization.
By leveraging NIST Toolkit, businesses, government agencies, and security teams can efficiently implement risk-based security controls, conduct thorough risk assessments, and achieve compliance with best practices and regulatory requirements.
Key Features:
- Formats: 55 editable Word documents, 6 Excel workbooks and two NIST reference PDFs.
- NIST SP 800-30 Compliance: Fully aligned with the NIST Risk Assessment methodology, ensuring a structured and standardized approach to risk evaluation.
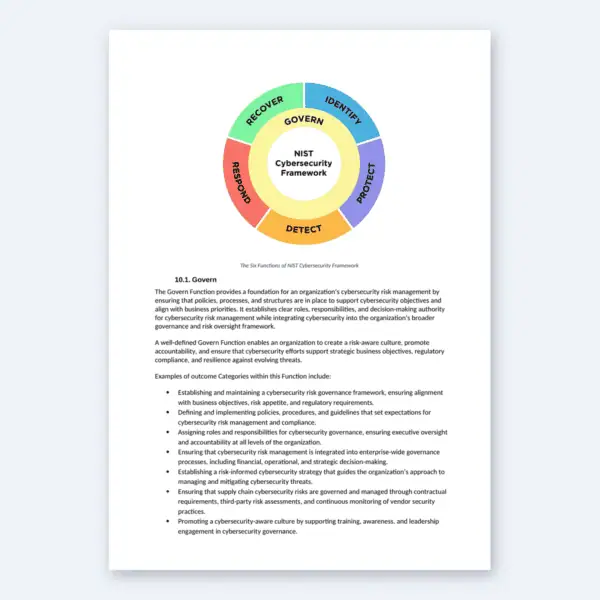
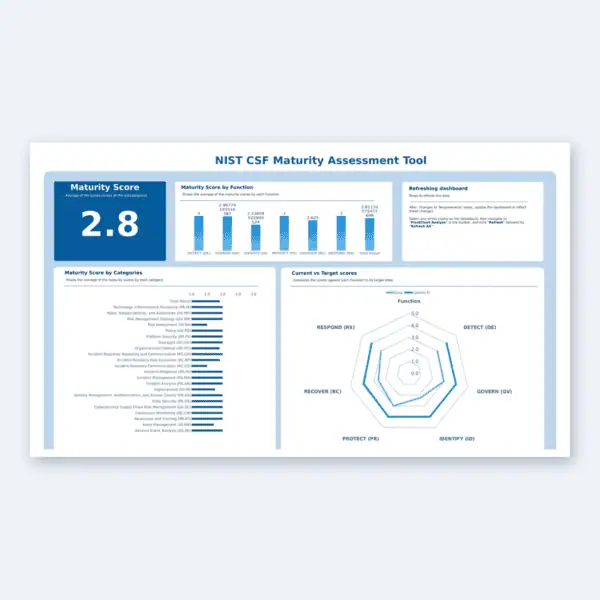
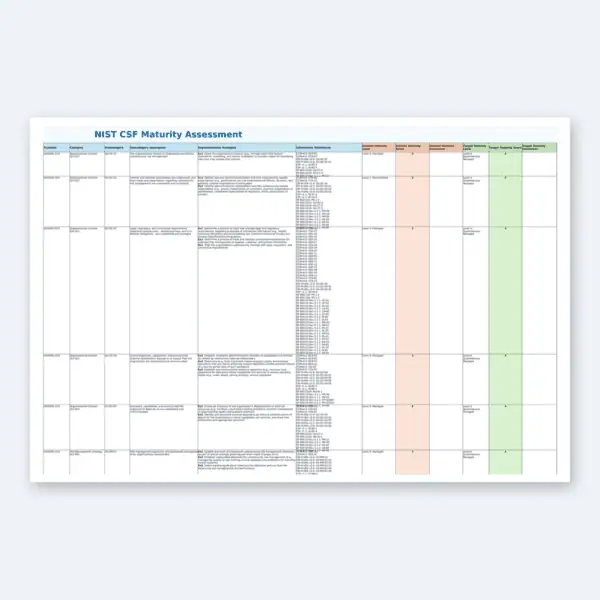
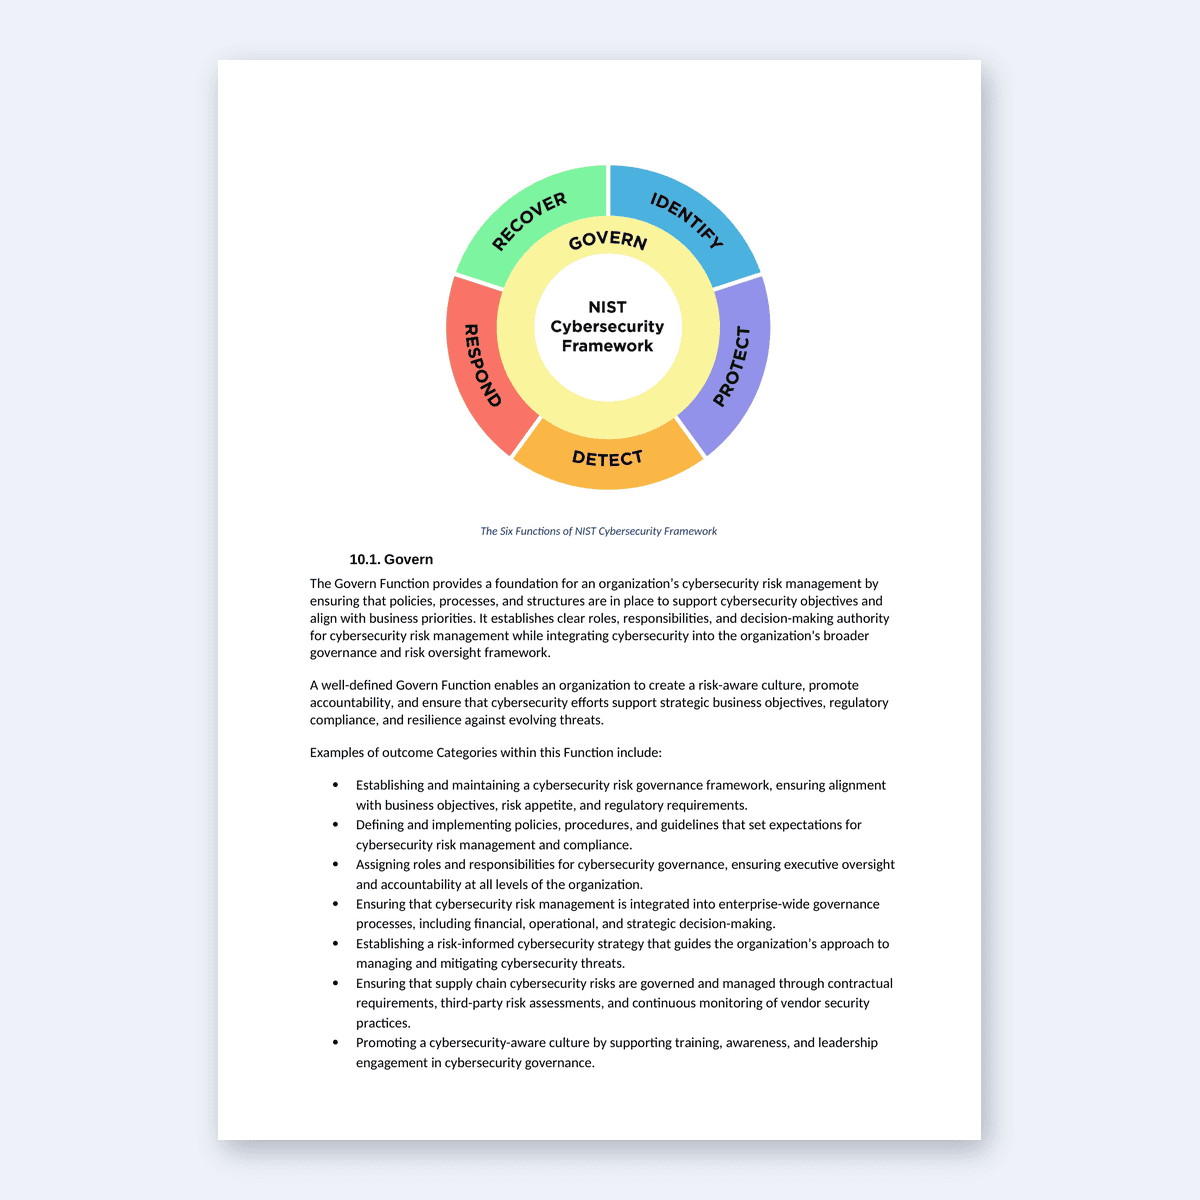
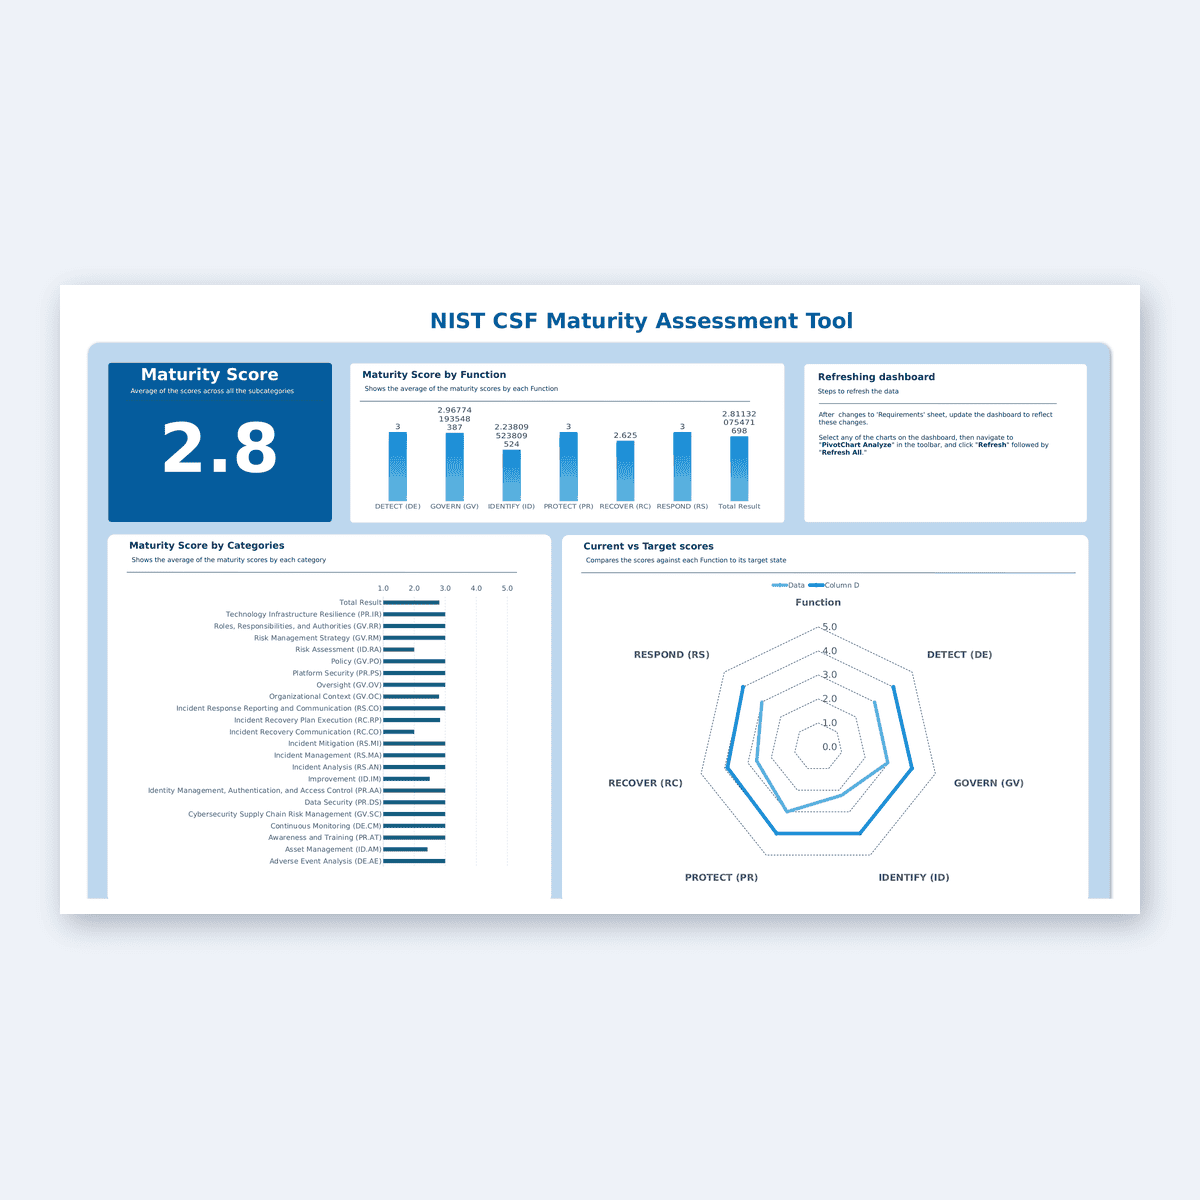
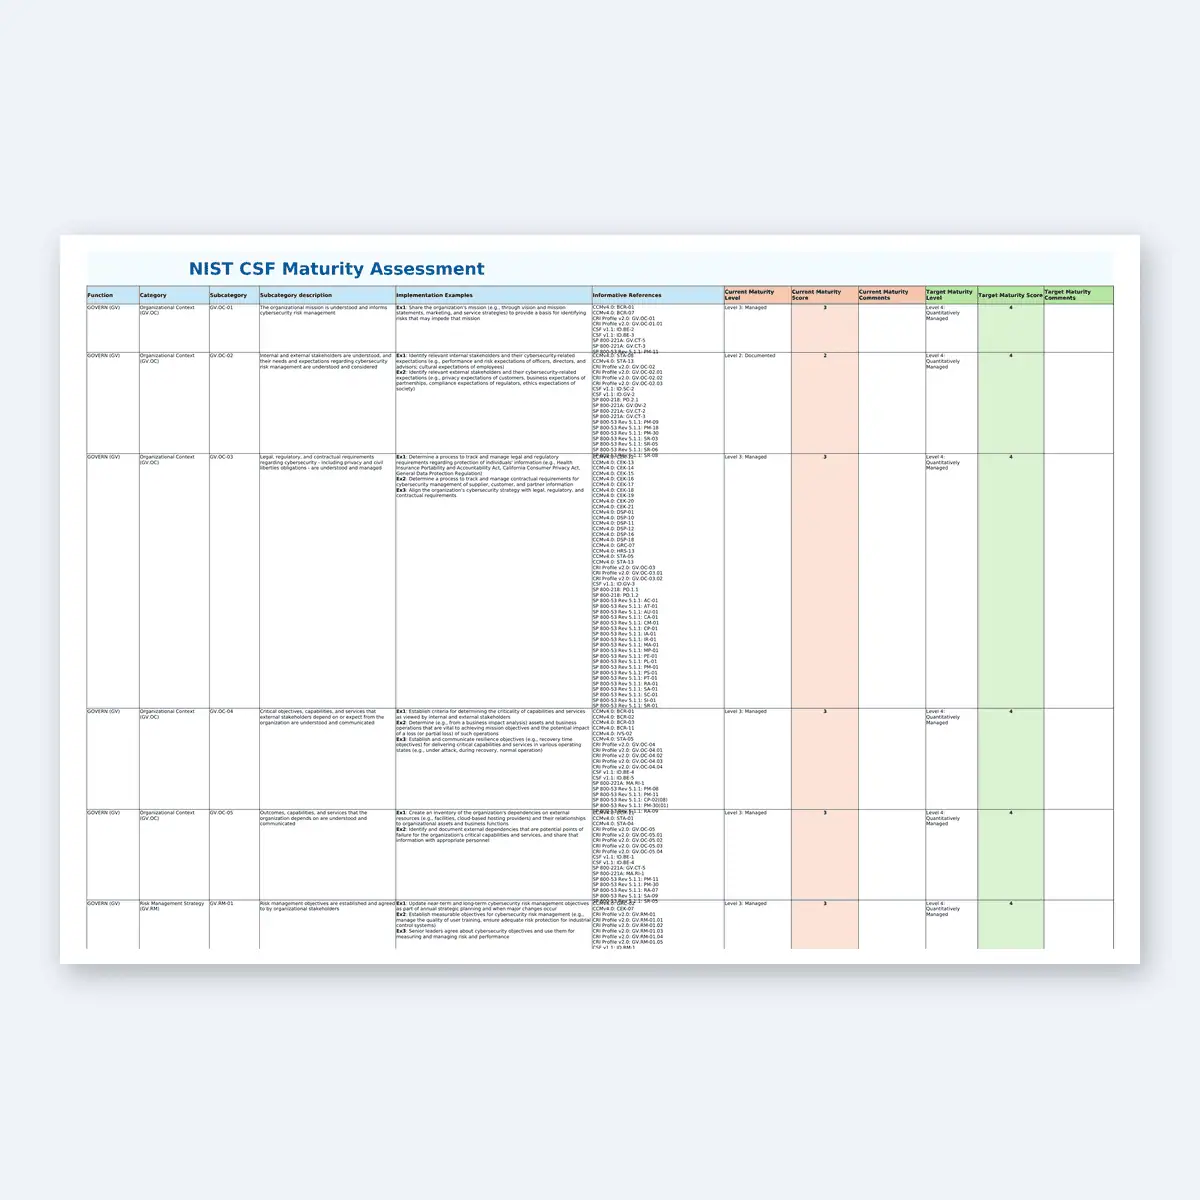
- Maturity Assessment Workbook: One Excel workbook scores maturity across the six Functions of the NIST Cybersecurity Framework 2.0 — Govern, Identify, Protect, Detect, Respond and Recover — over all 106 Subcategories.
- Comprehensive Risk Questionnaires: Detailed, pre-configured risk assessment forms with automated scoring.
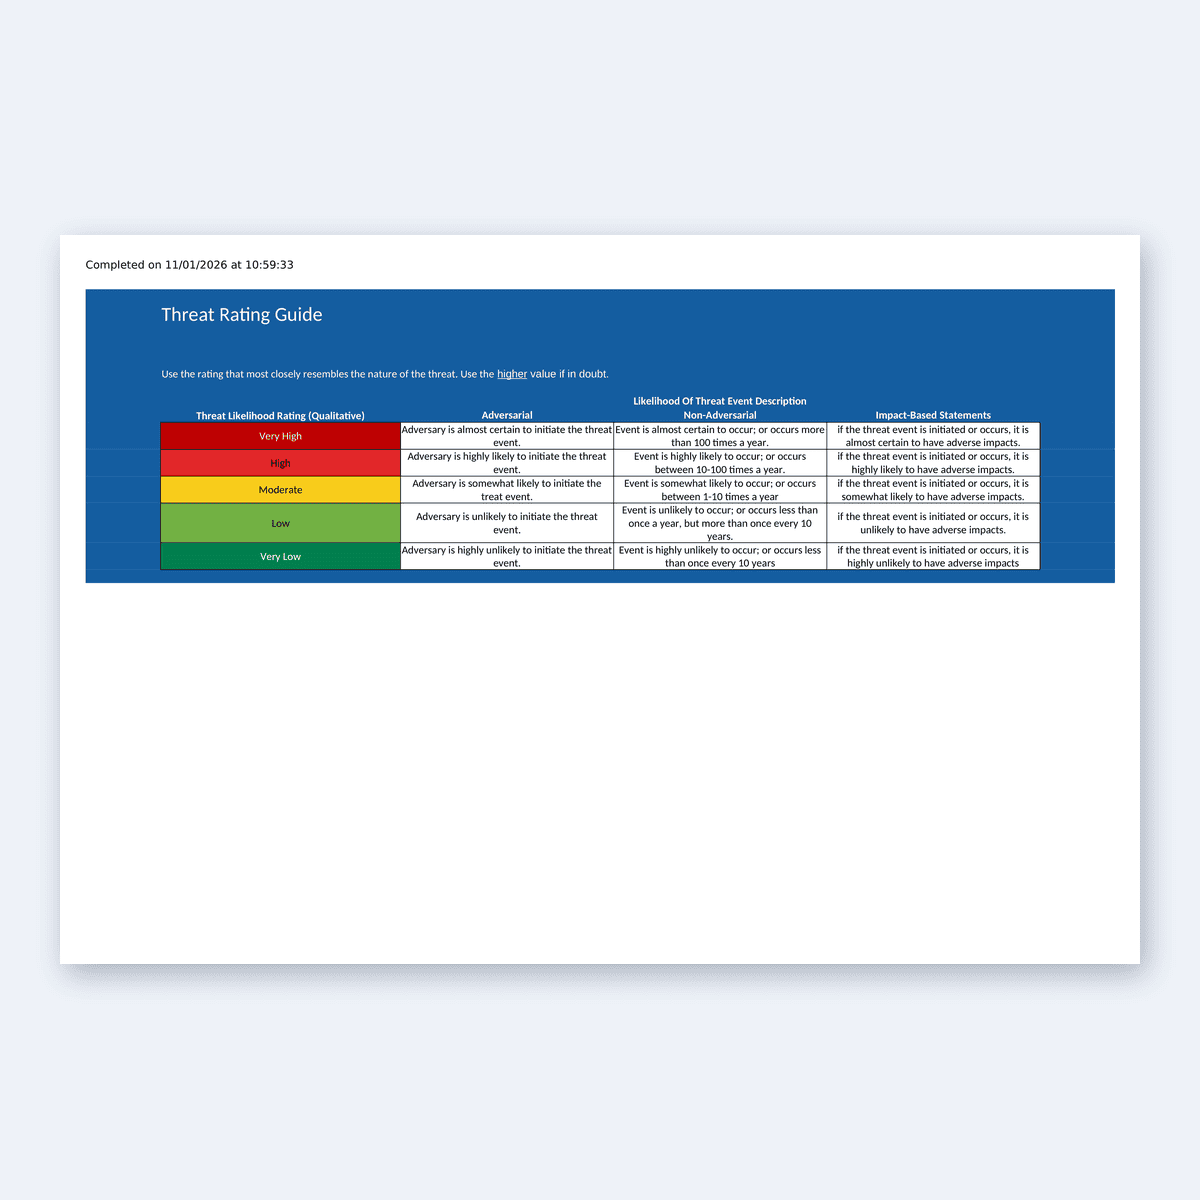
- Automated Risk Calculations: Excel-based tools for dynamic risk scoring, prioritization, and visualization of security posture.
- Gap Analysis & Remediation Plan: Helps organizations identify security weaknesses and develop structured mitigation strategies.
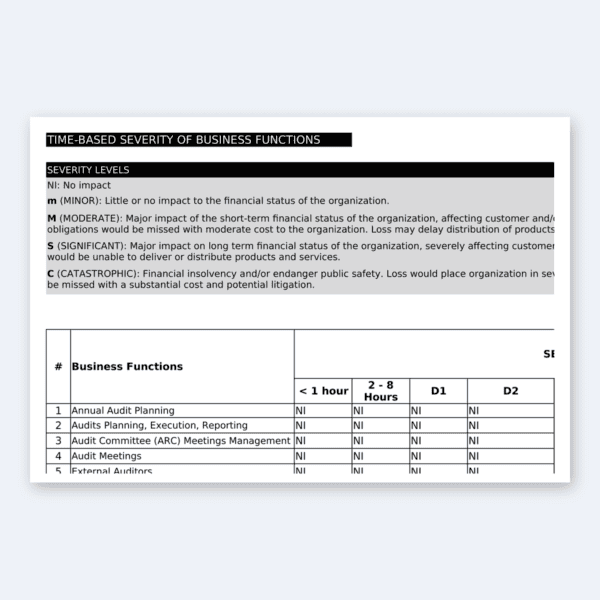
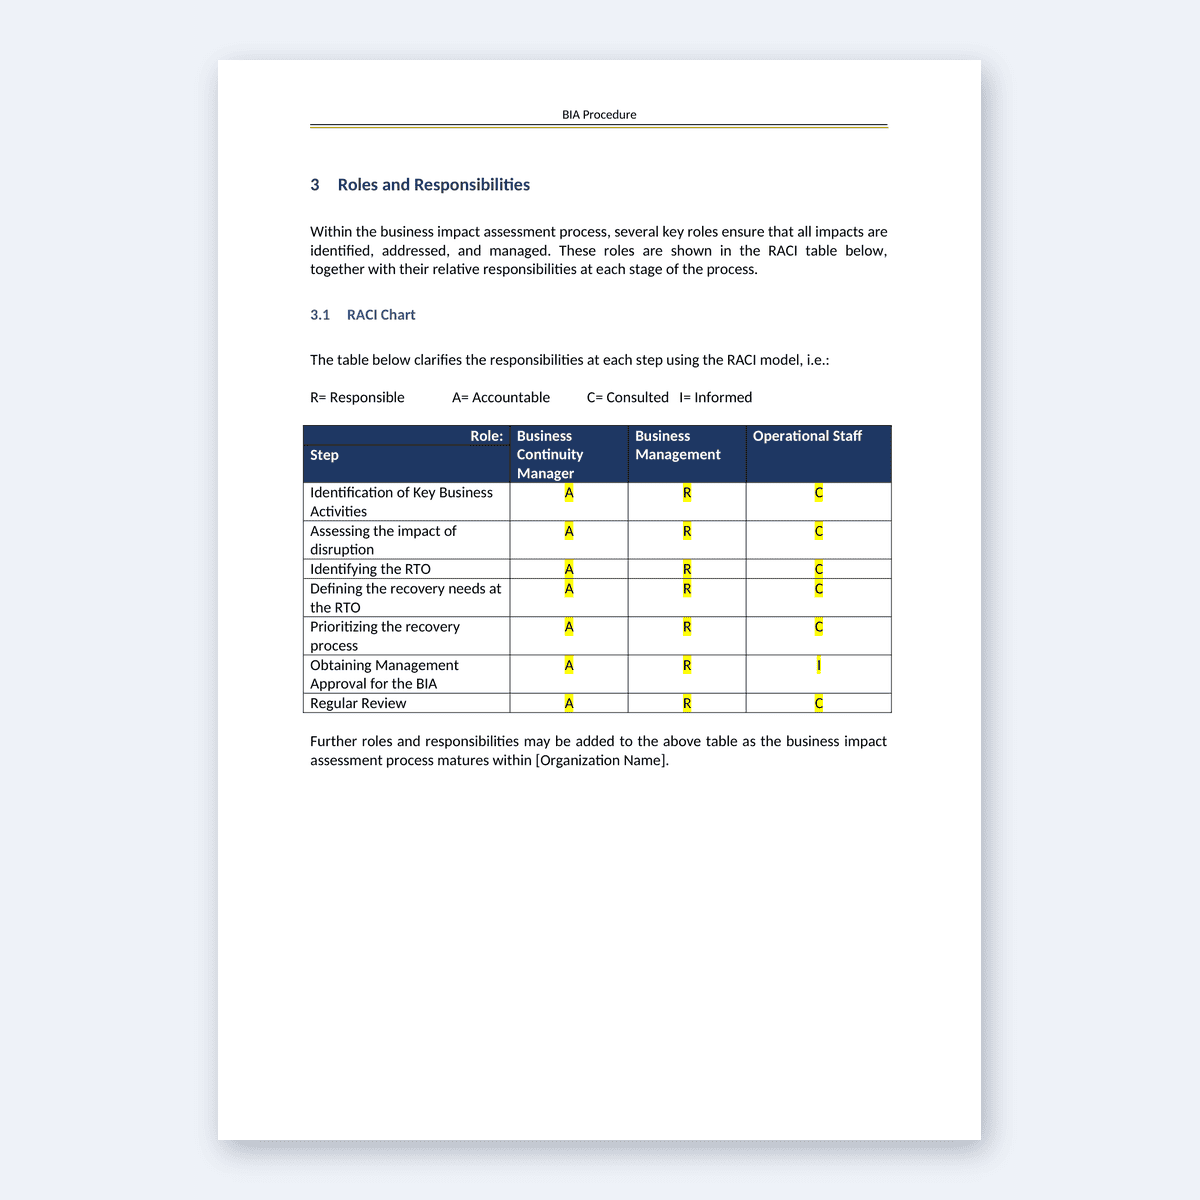
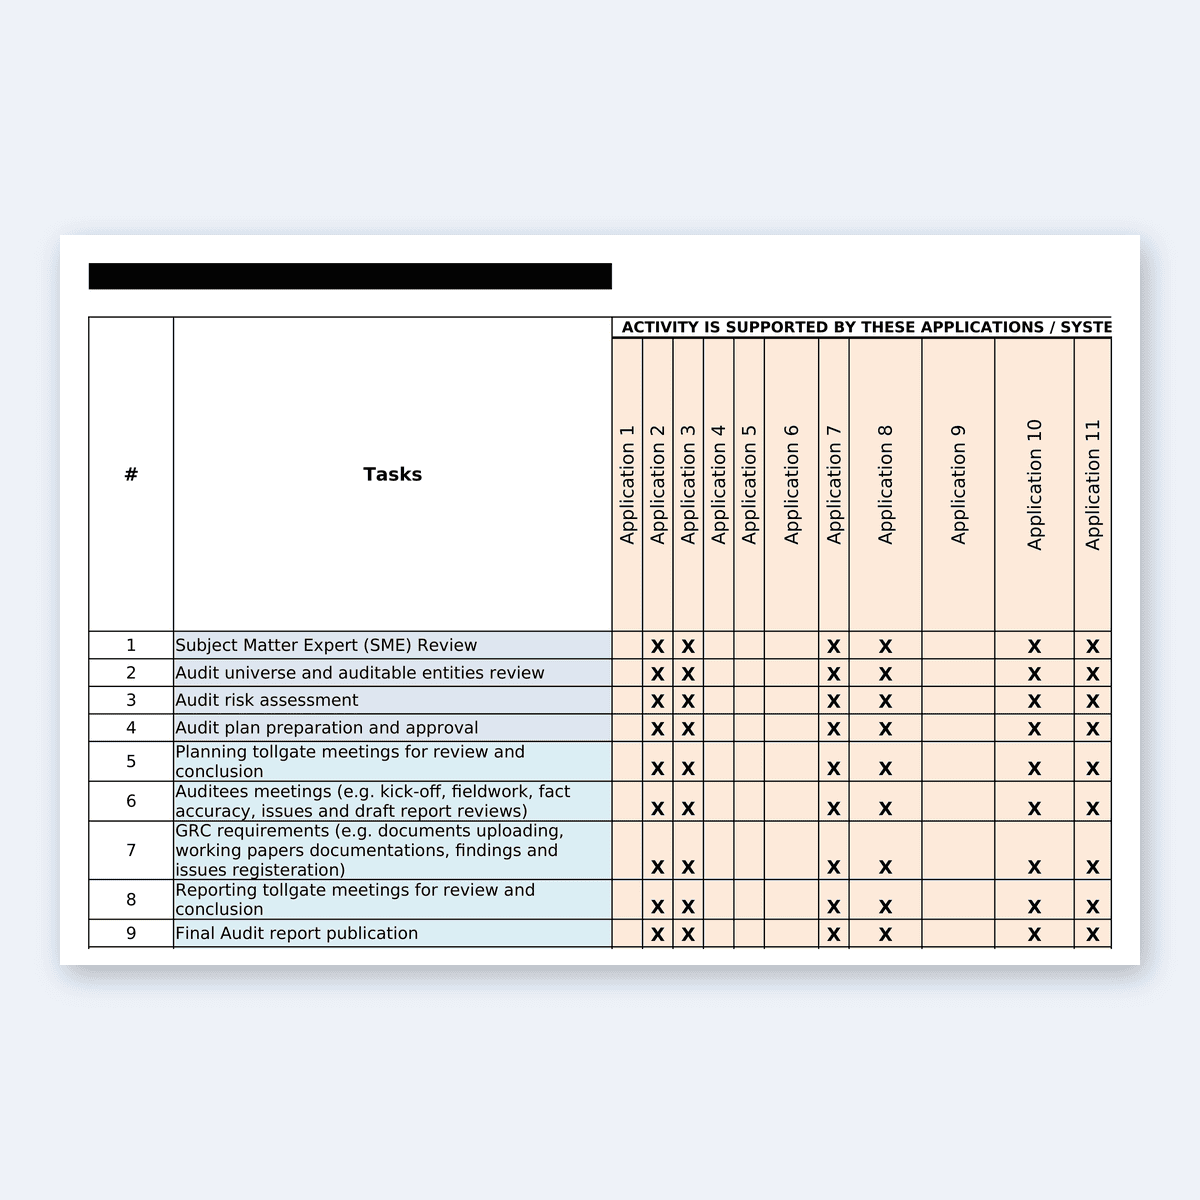
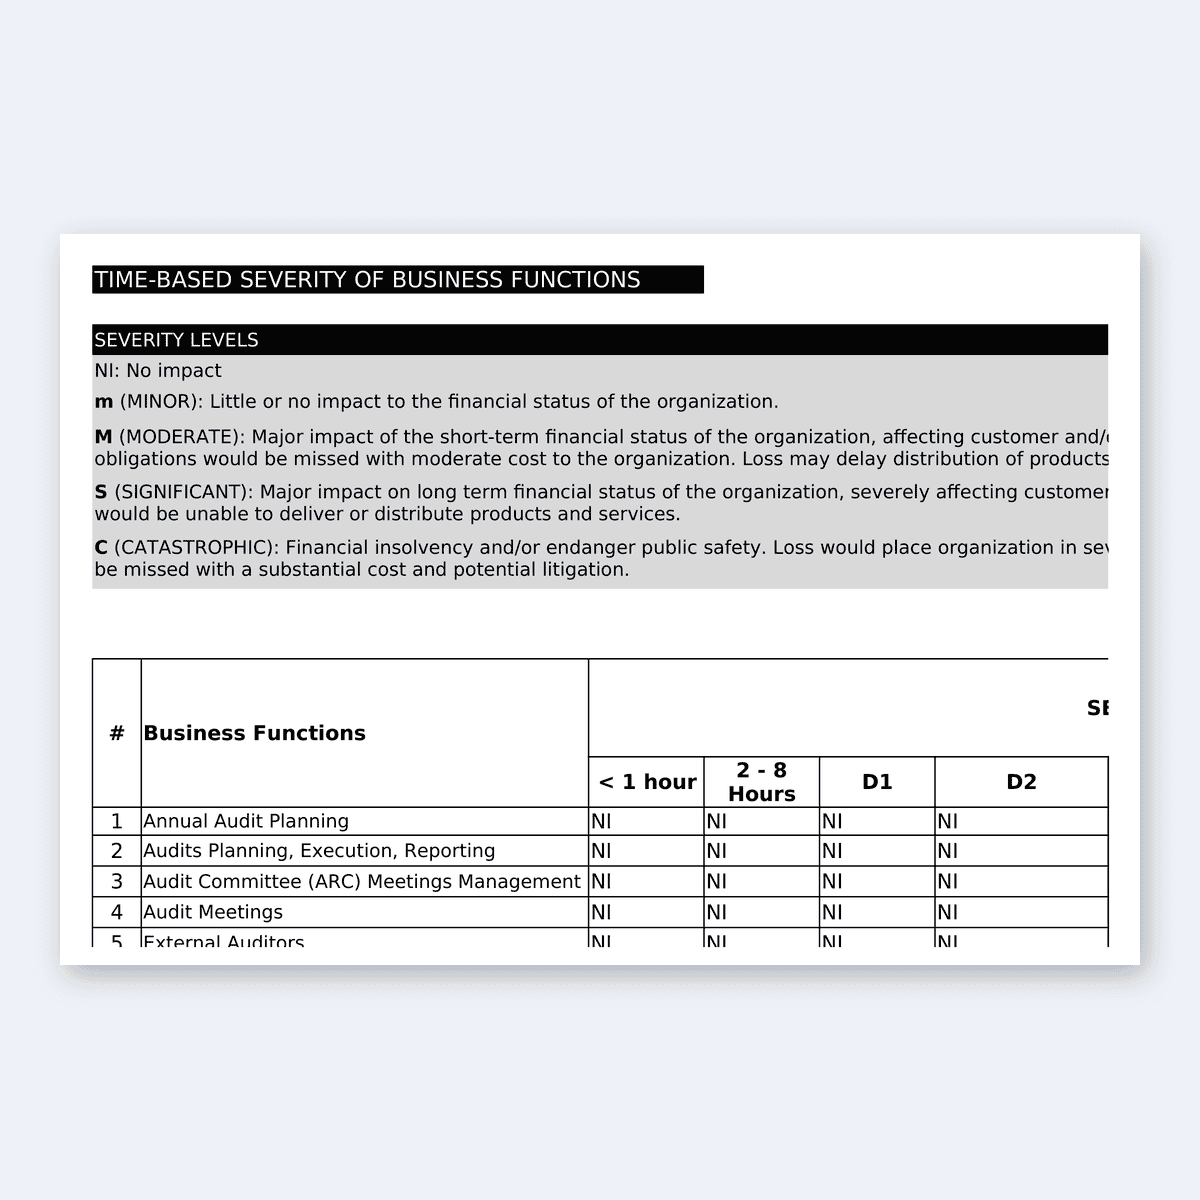
- Business Impact Analysis (BIA): Assess the potential consequences of risk events on business operations.
- Incident Management: incident management policy and reporting templates.
- Policy and Procedure Templates: Pre-built security policies covering access control, encryption, incident management, and more.
- Risk Treatment Plan: Pre-defined controls and mitigation measures mapped to NIST standards.
NIST Toolkit consist of the following documents:
- BIA Assessment Tool
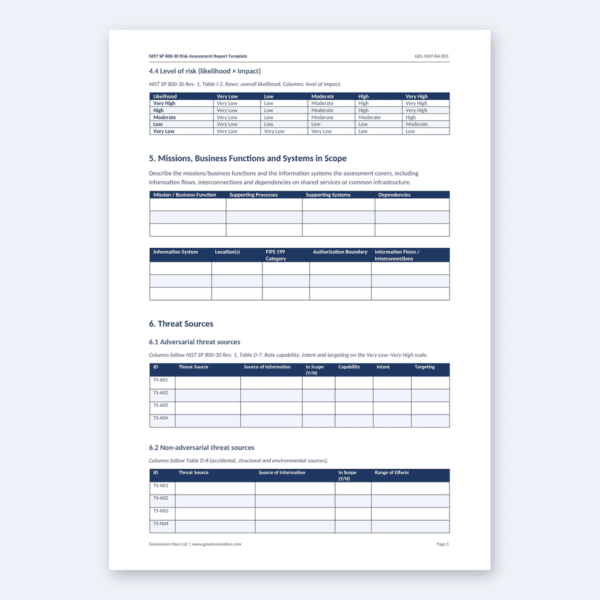
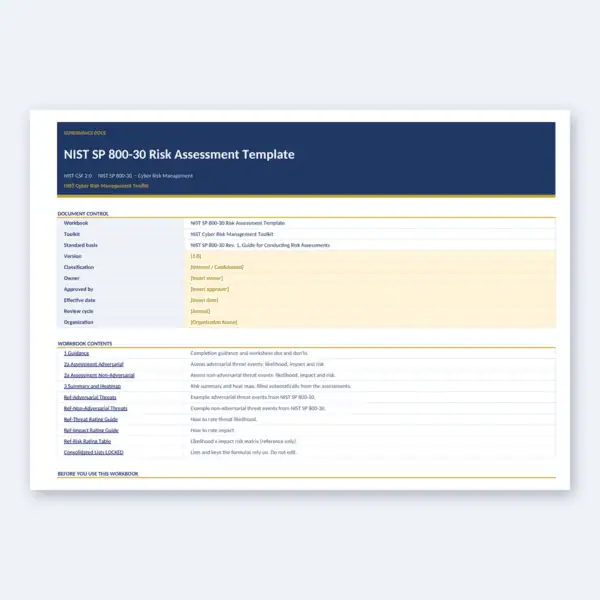
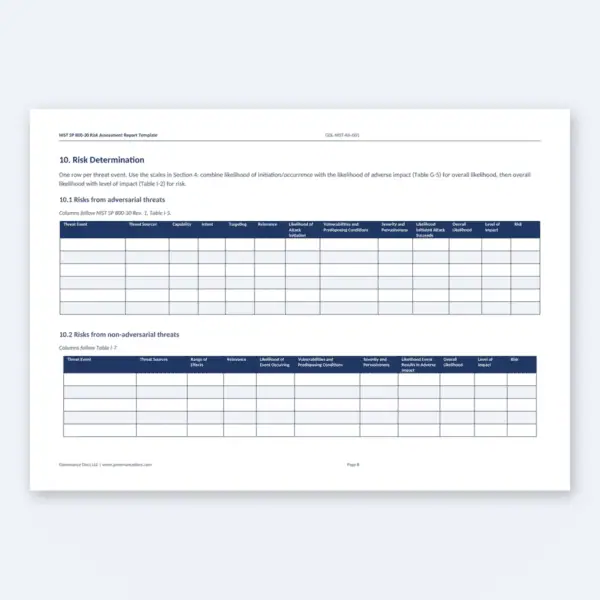
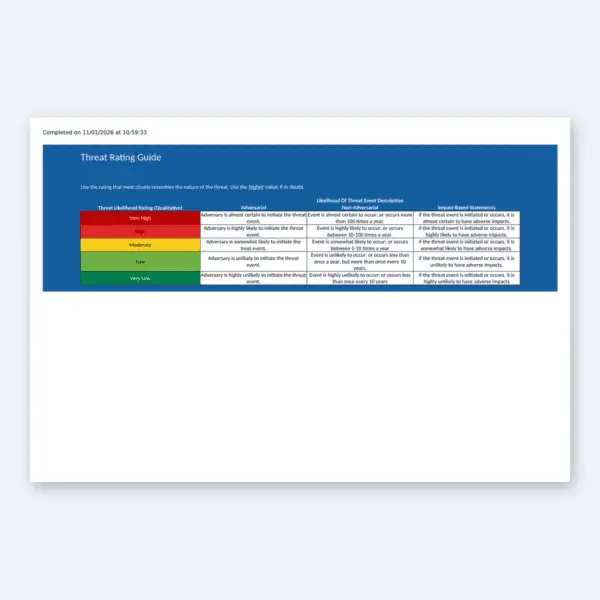
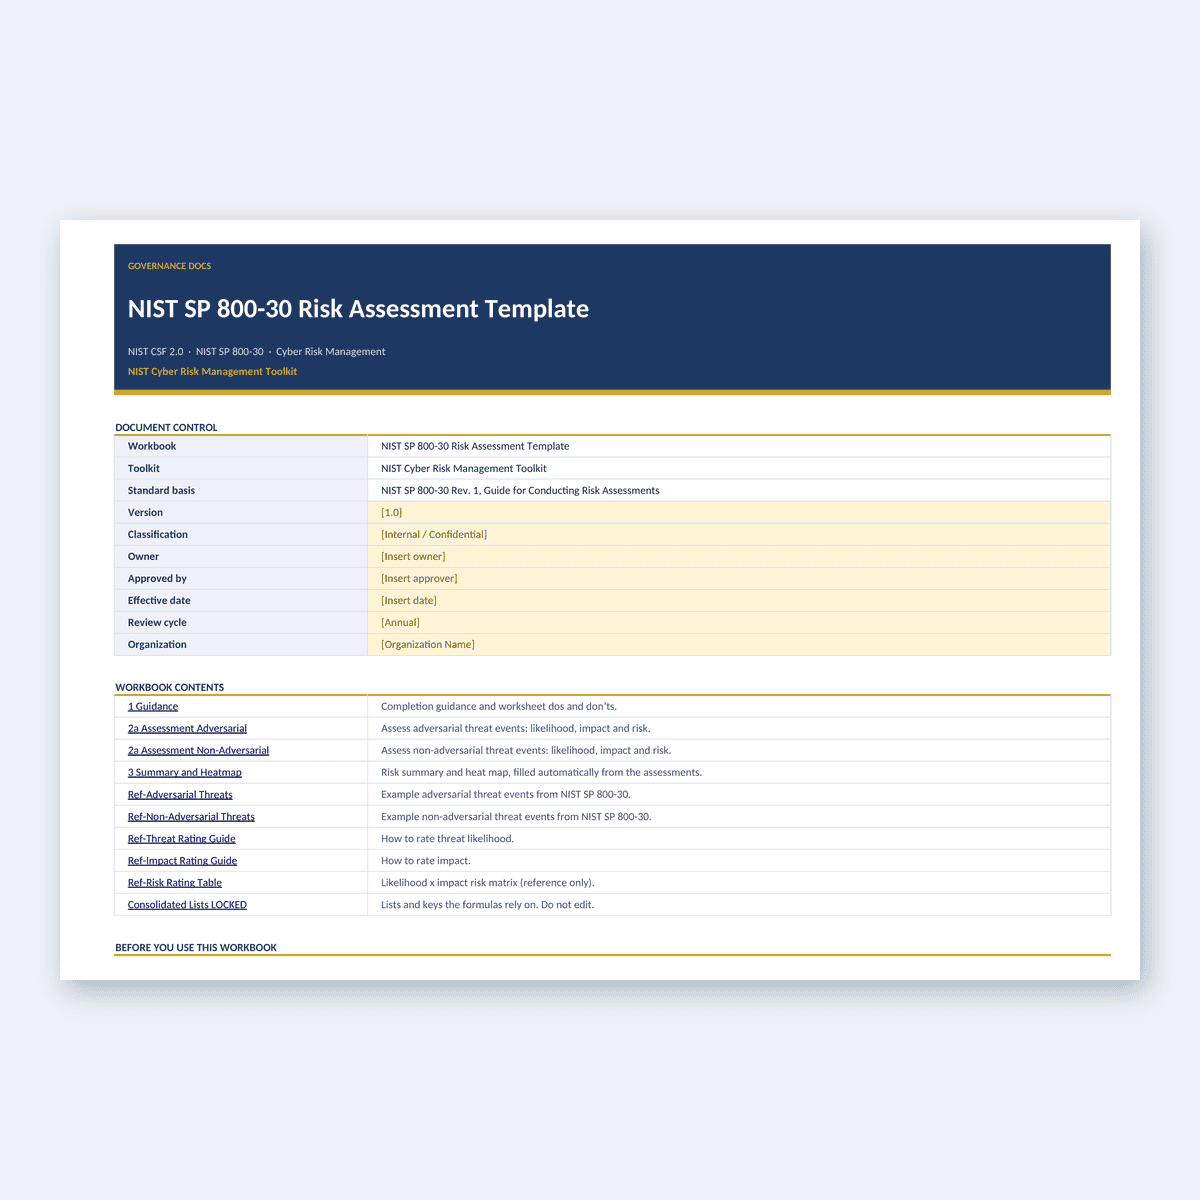
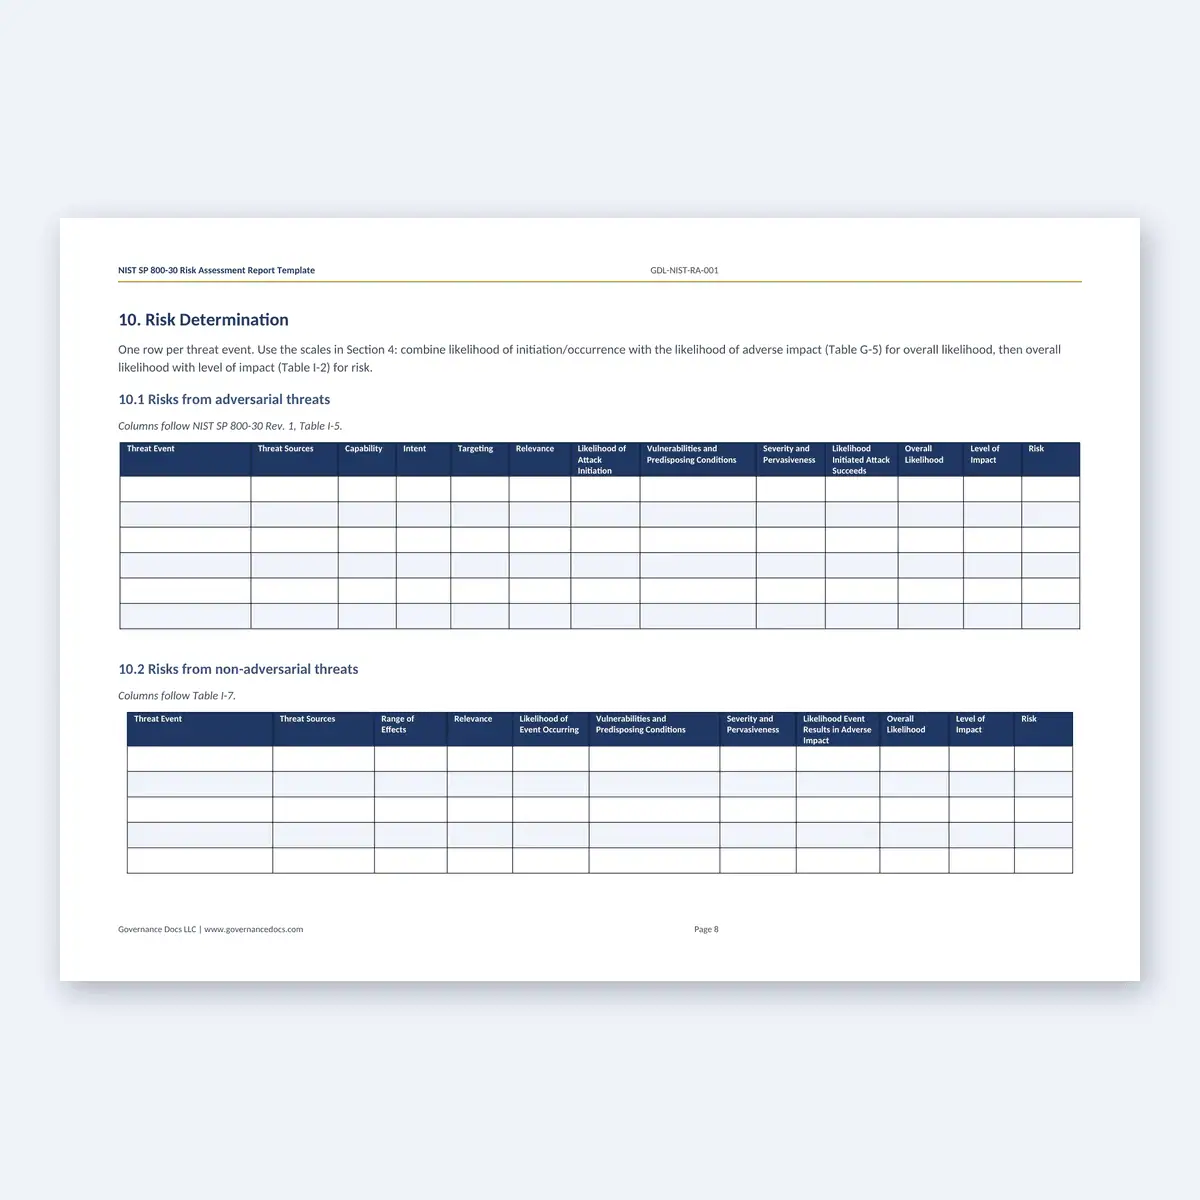
- NIST 800-30 Risk Assessment Template
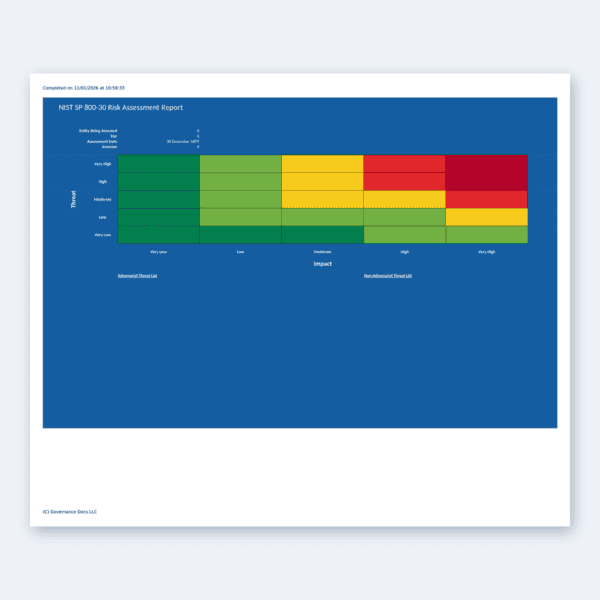
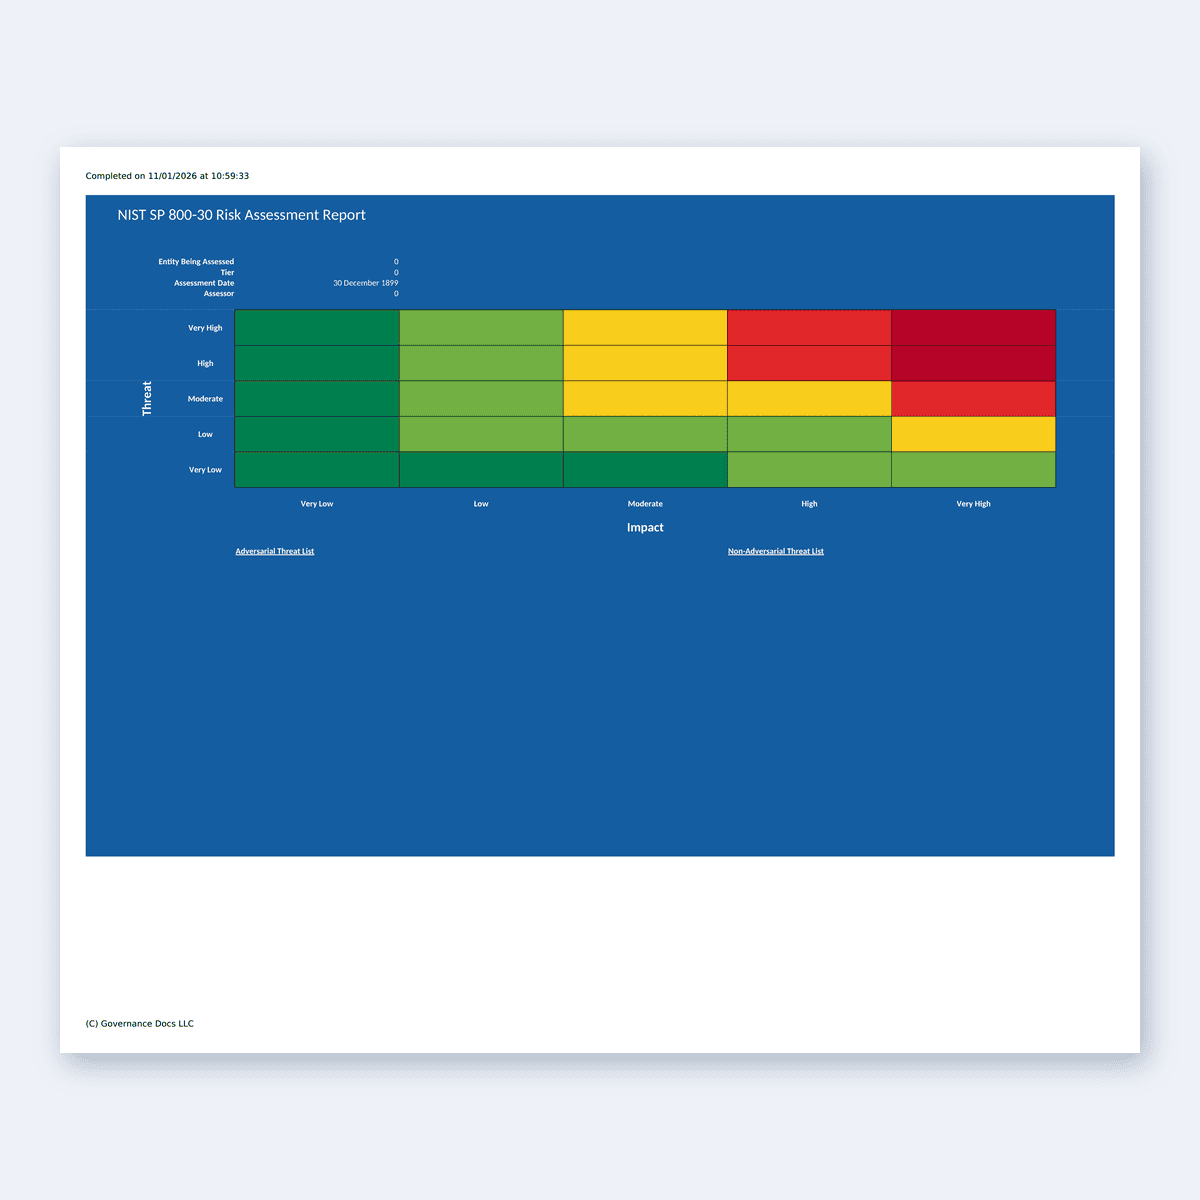
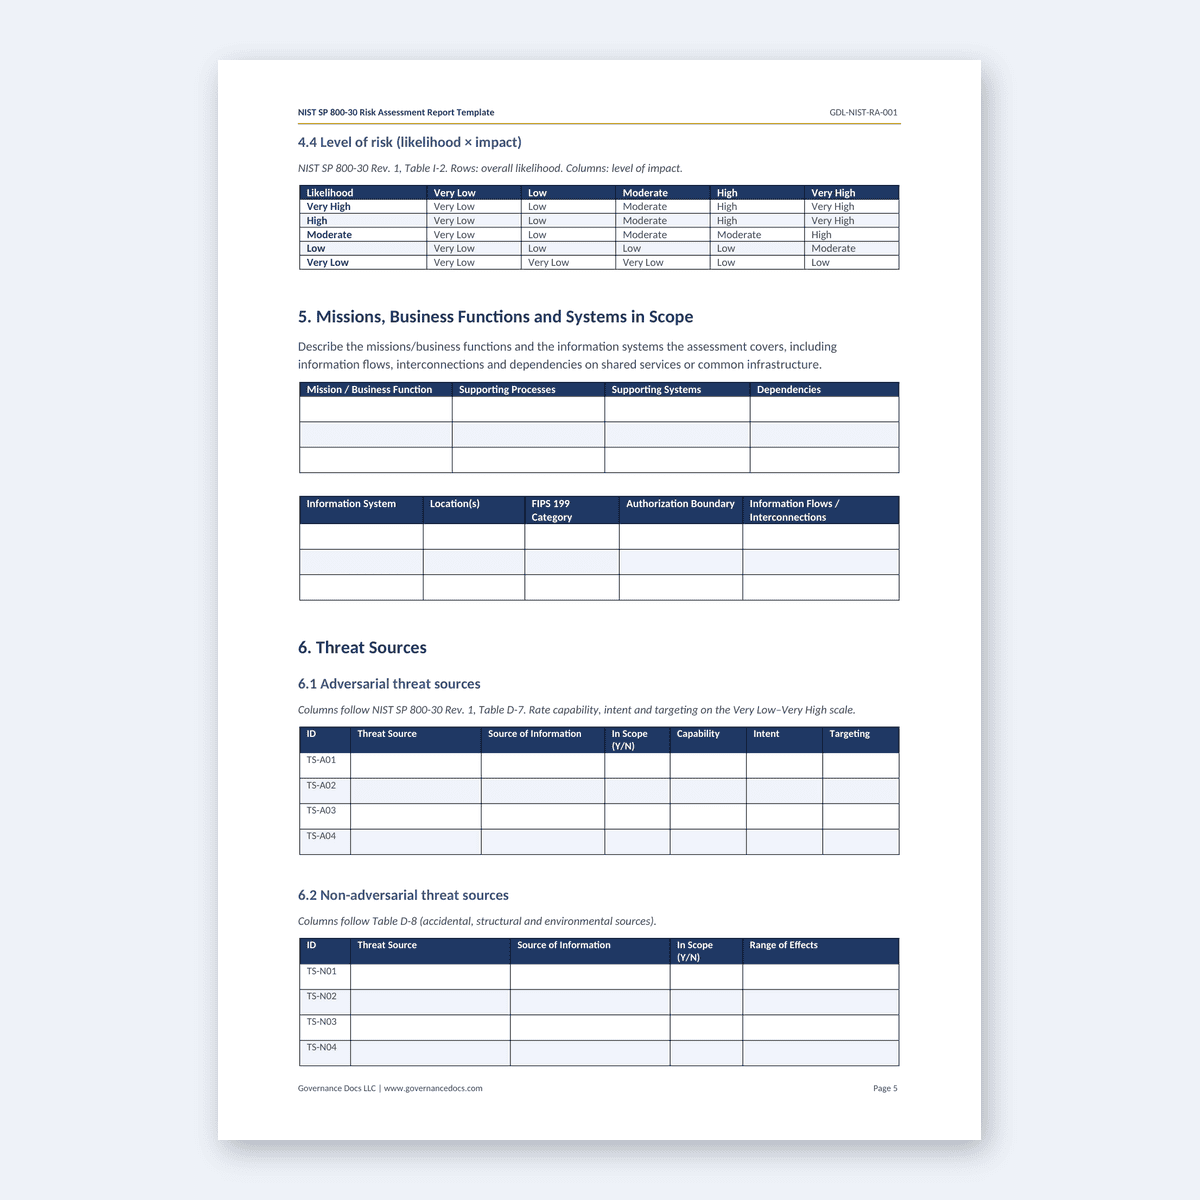
- NIST SP 800-30 Risk Assessment Report Template
- NIST CSF 2.0 Maturity Assessment Template
- CSF 2.0 Organizational Profile
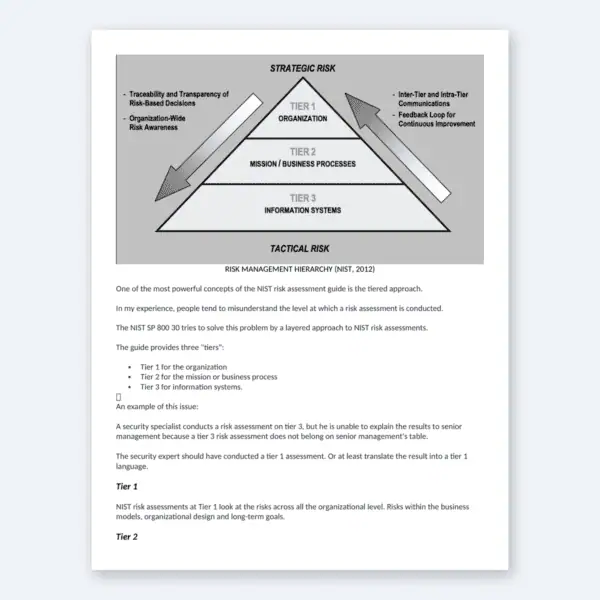
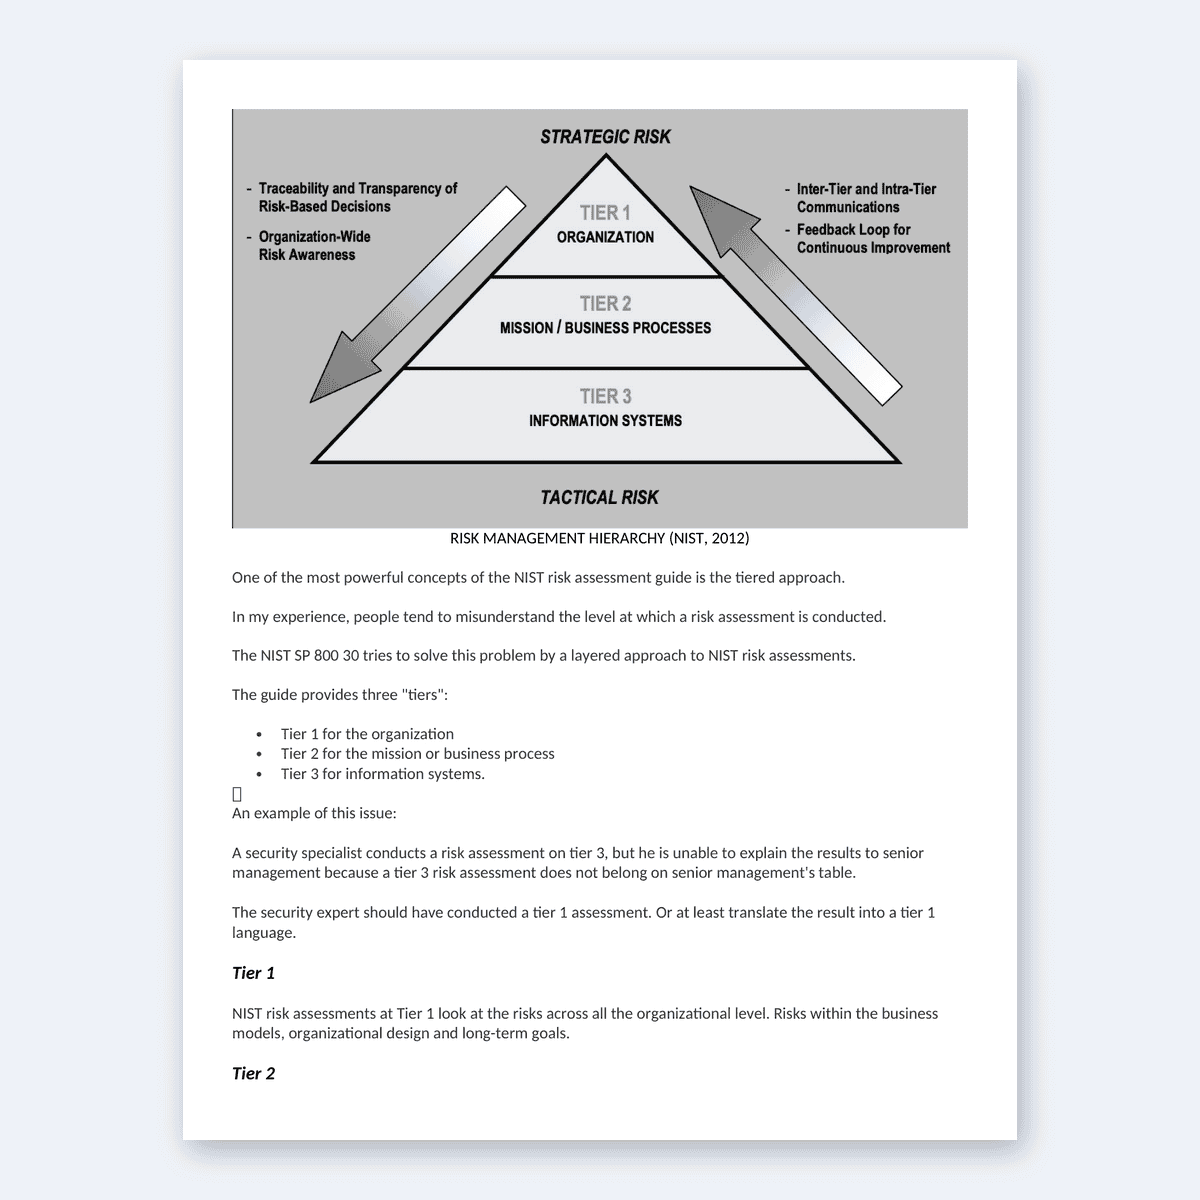
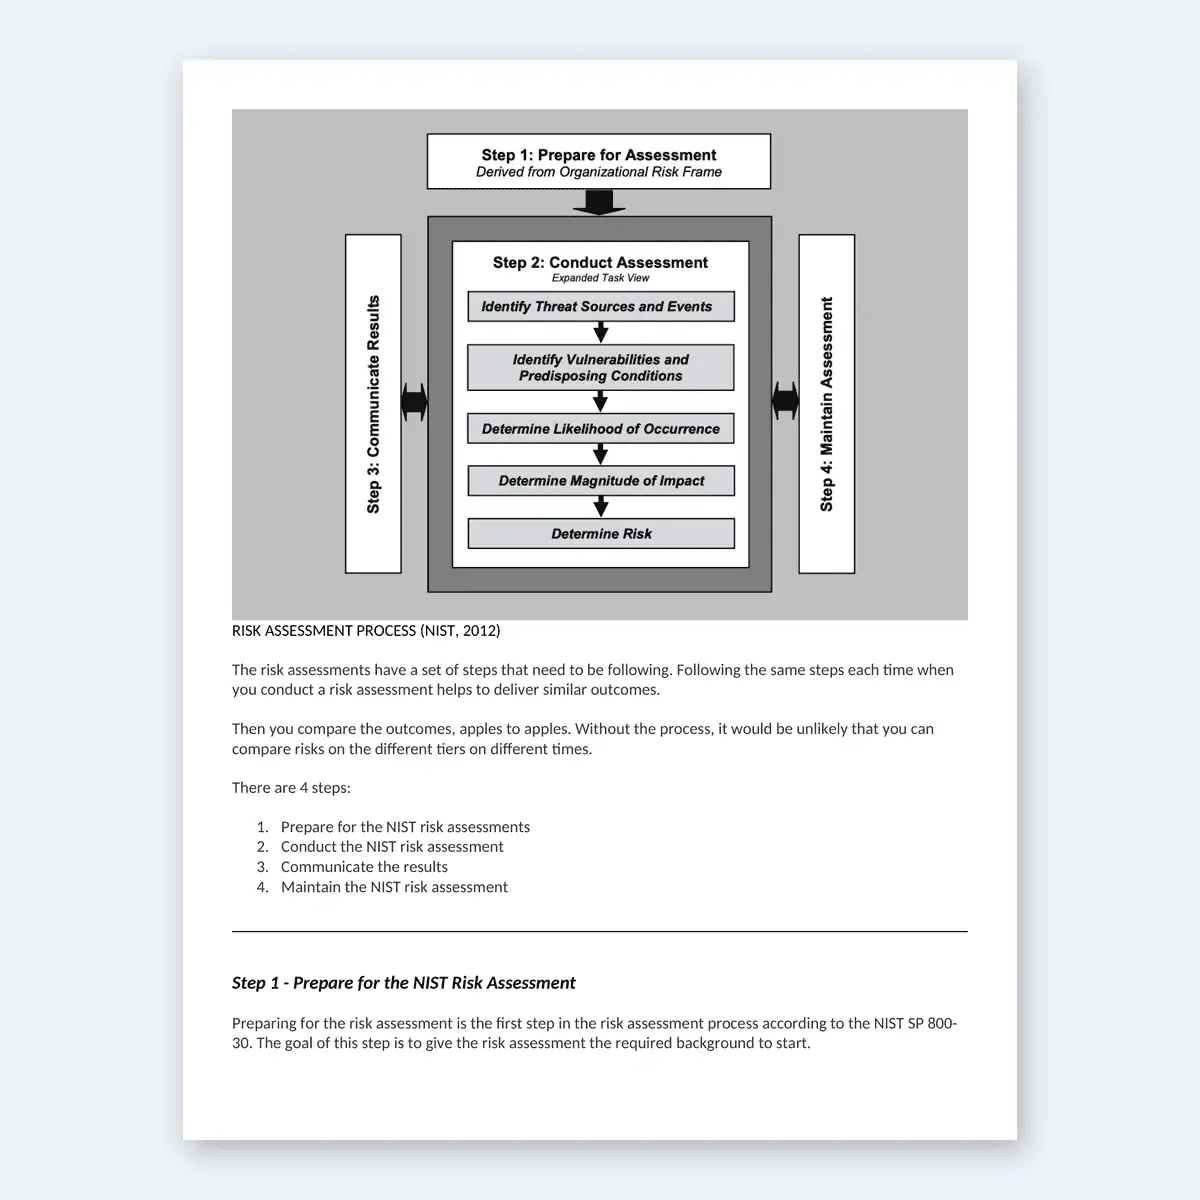
- The Complete Guide to NIST 800-30 Risk Assessments
- Acceptable Use Policy
- Access Control Policy
- Anti-Malware Policy
- Asset Handling Policy
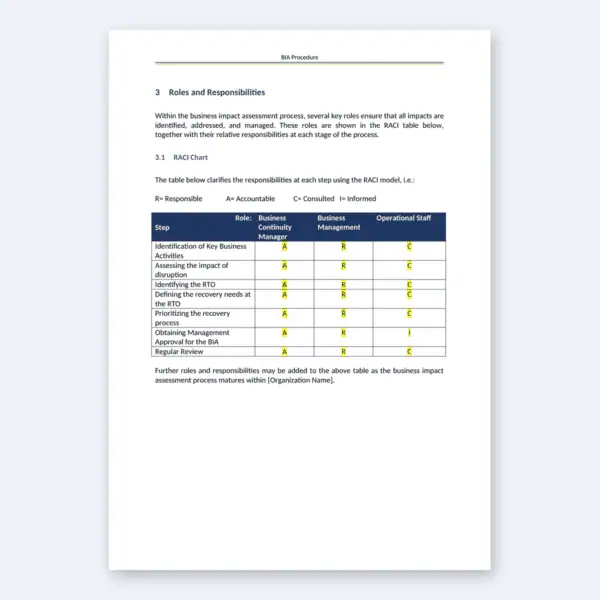
- BIA Procedure
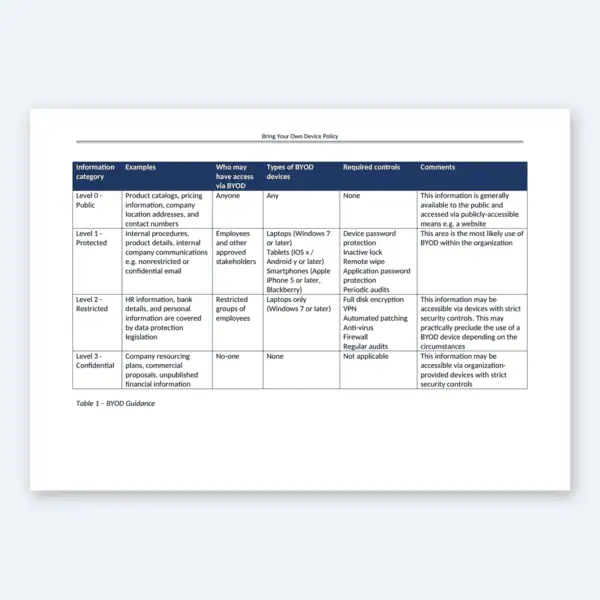
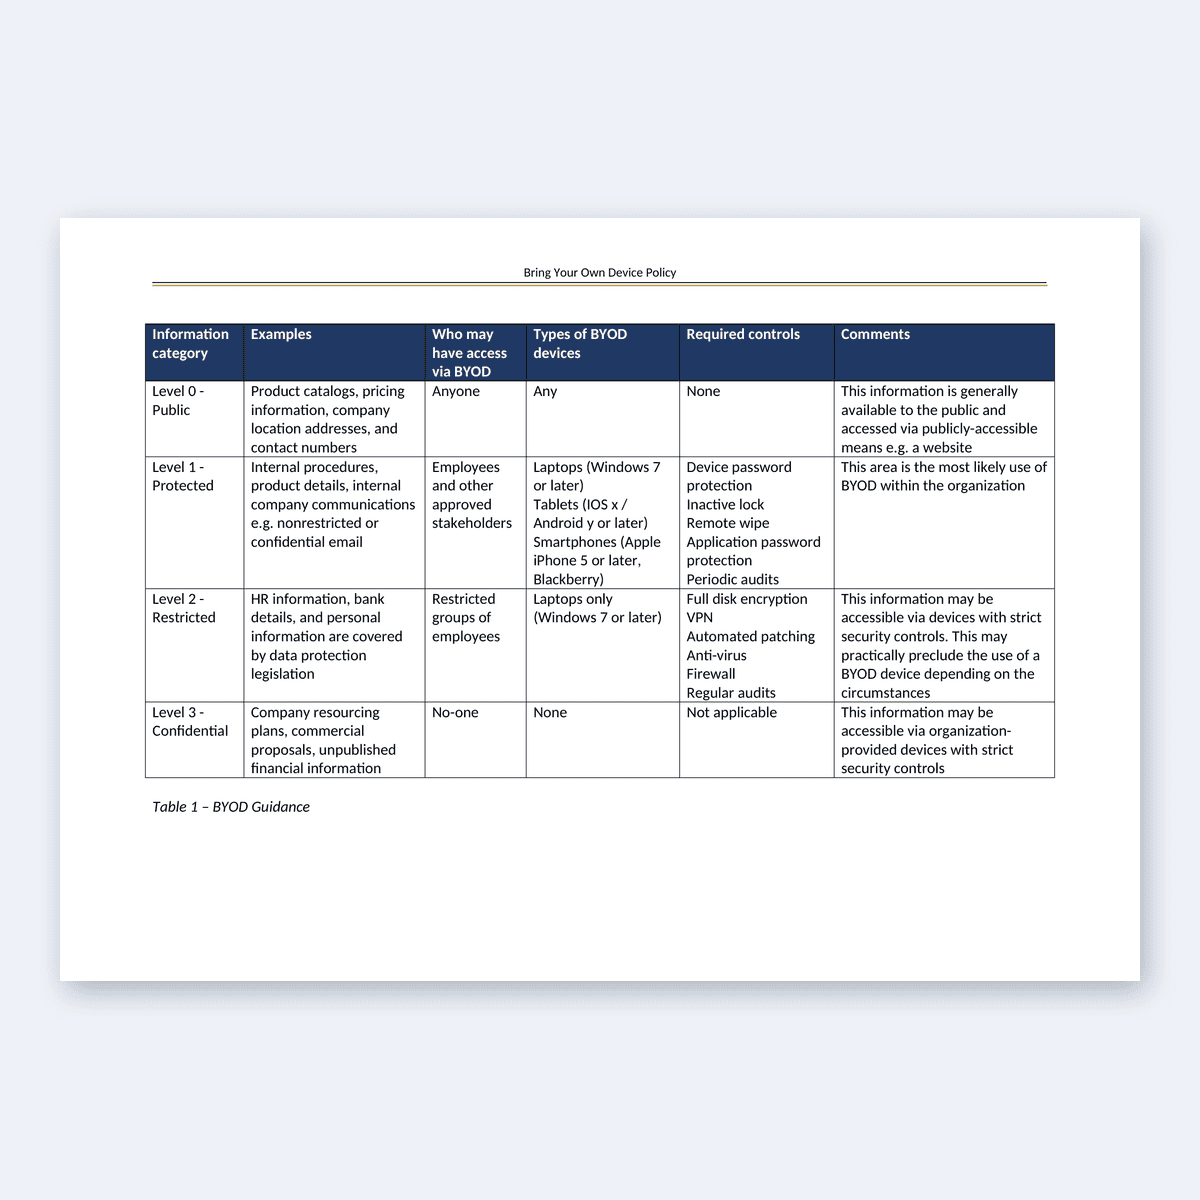
- BYOD Policy
- Change Management Policy
- Cloud Services Security Policy
- Configuration Management Procedure
- Copyright Compliance Policy
- Cryptographic Policy
- Cyber Incident Response Plan
- Cyber Security Risk Management Framework
- Data Masking Policy
- Data Retention Policy
- Development Environment Policy
- DLP Policy
- Email Usage Policy
- Employee Disciplinary Process
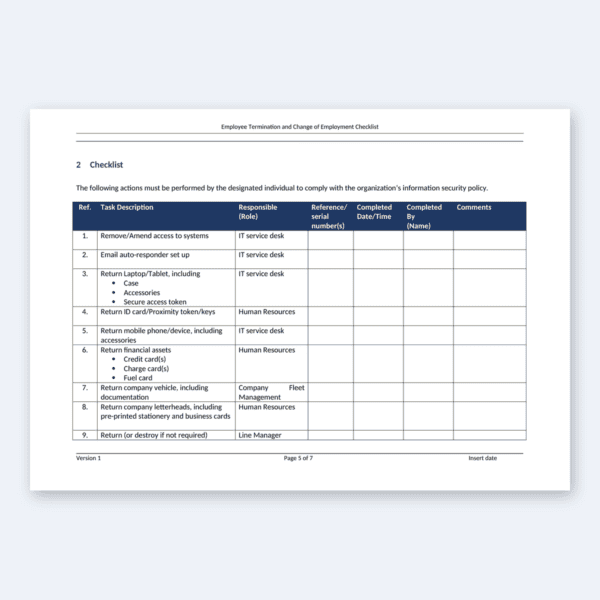
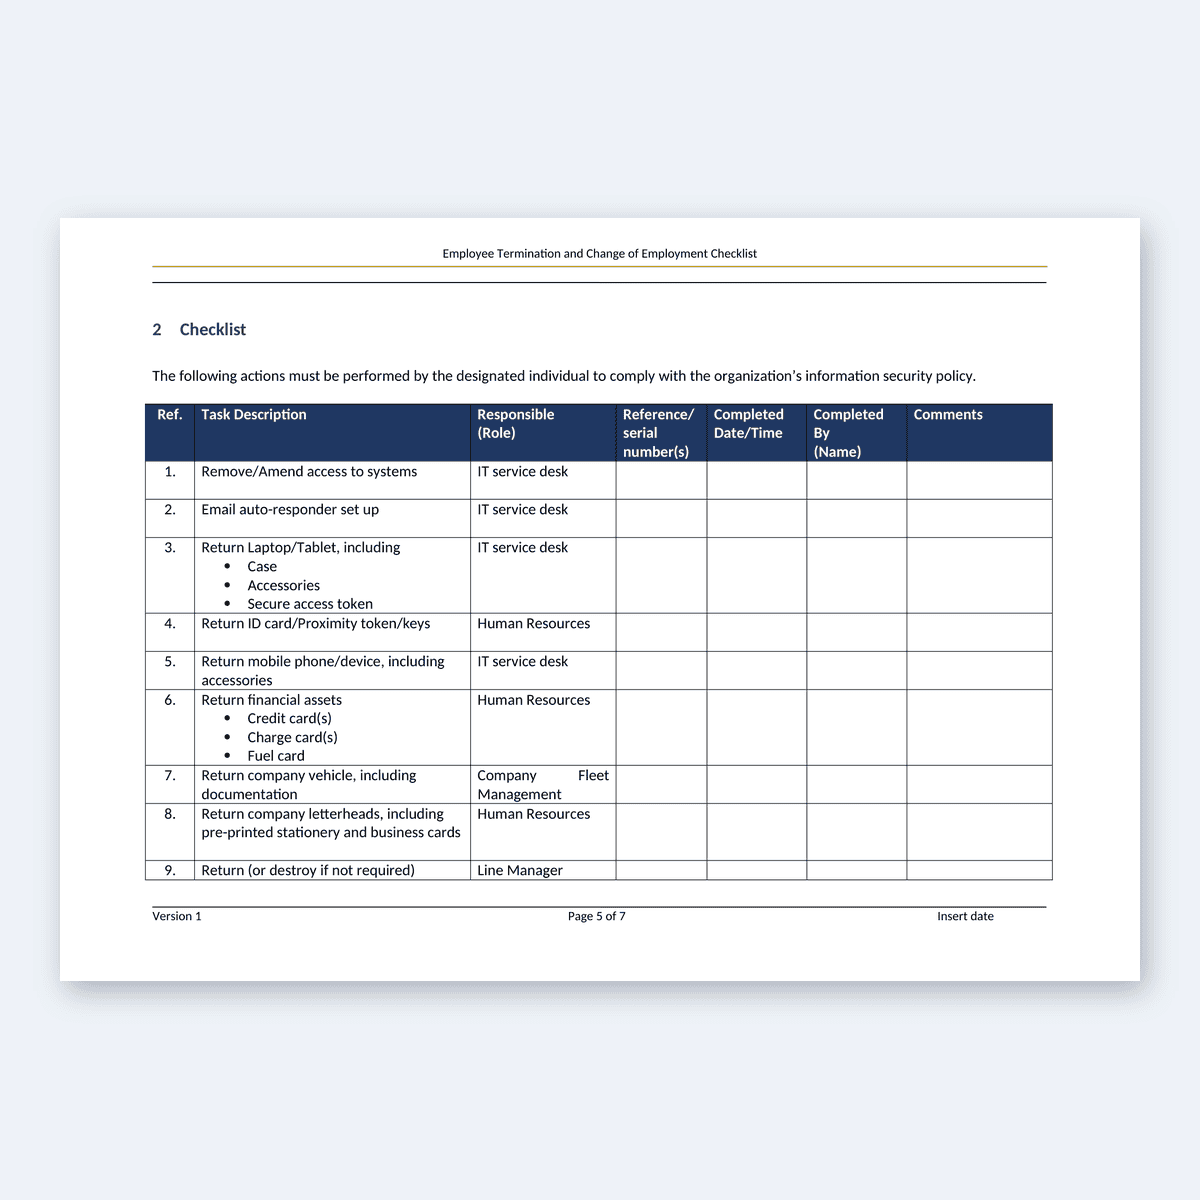
- Employee Movement and Termination Checklist
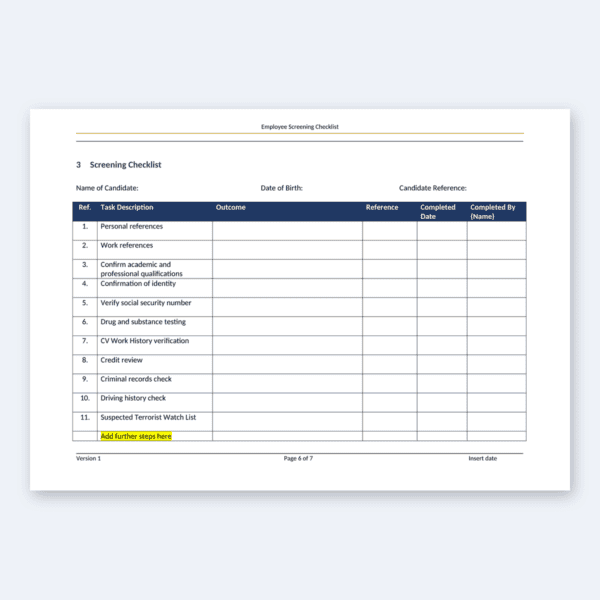
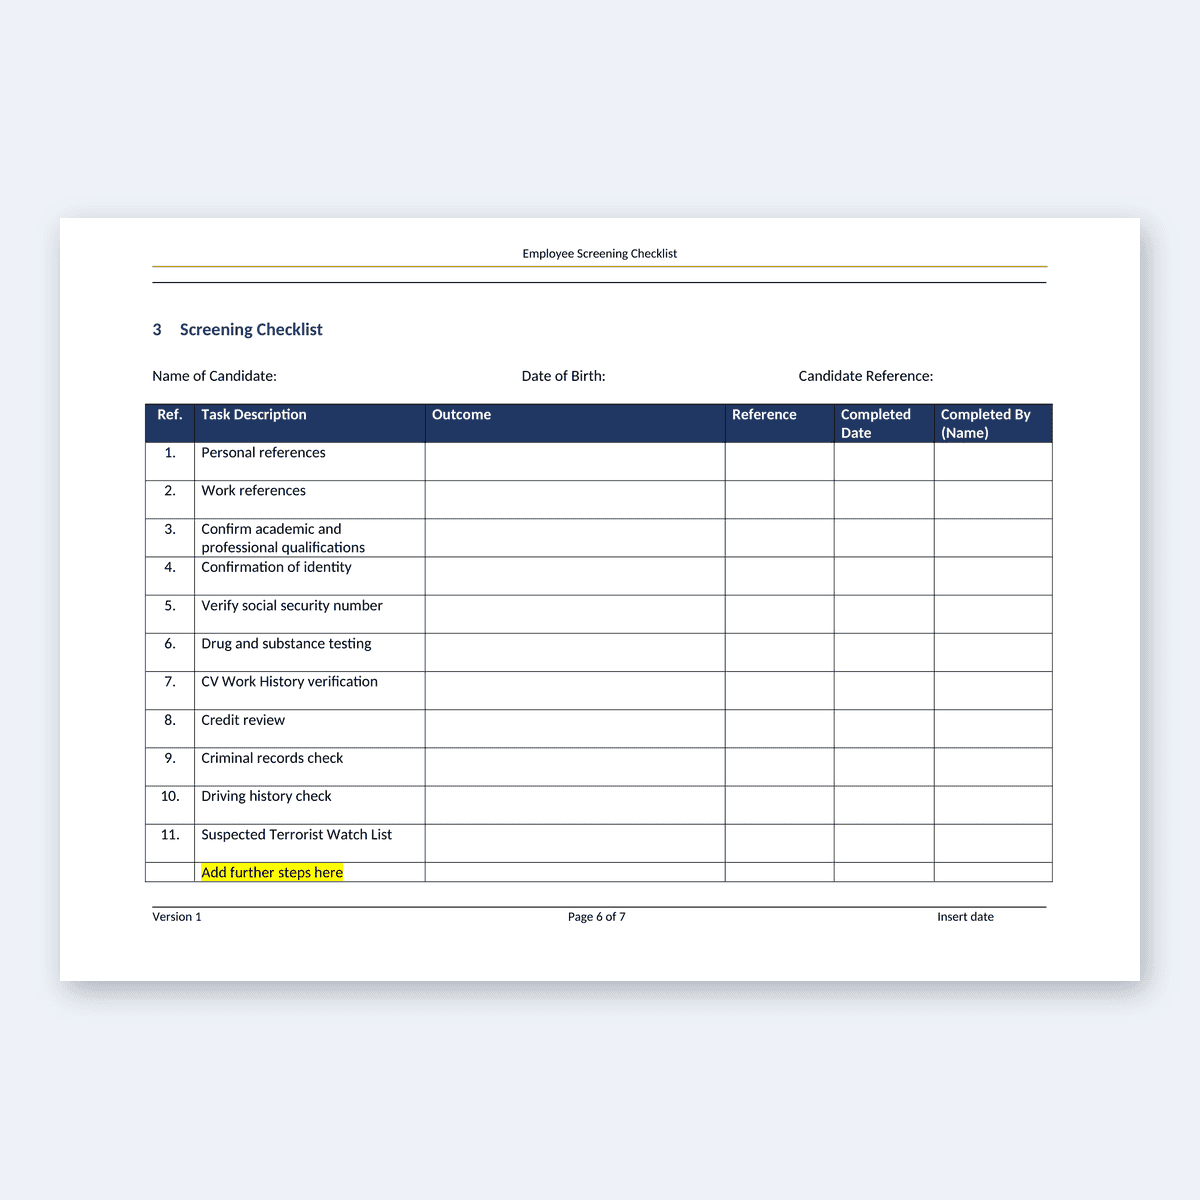
- Employee Screening Checklist
- Employment Contracts Clauses
- Incident Response Procedure
- Information Security Classification Policy
- Information Security Labelling Procedure
- Information Security Policy
- Information Security Roles and Responsibilities
- Internet Acceptable Use Policy
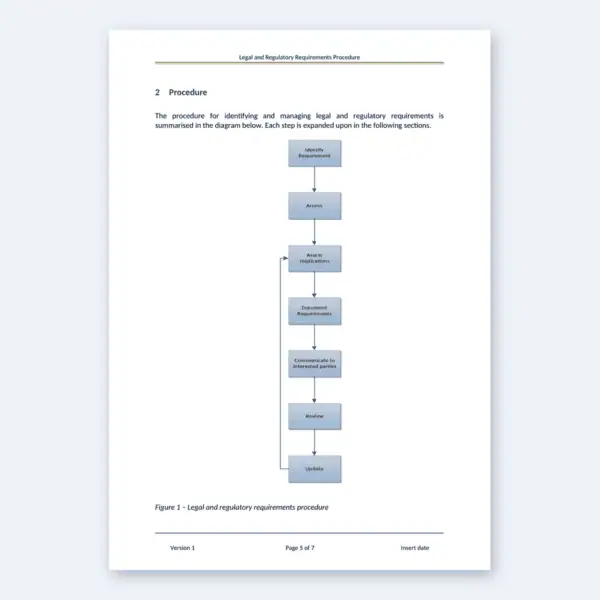
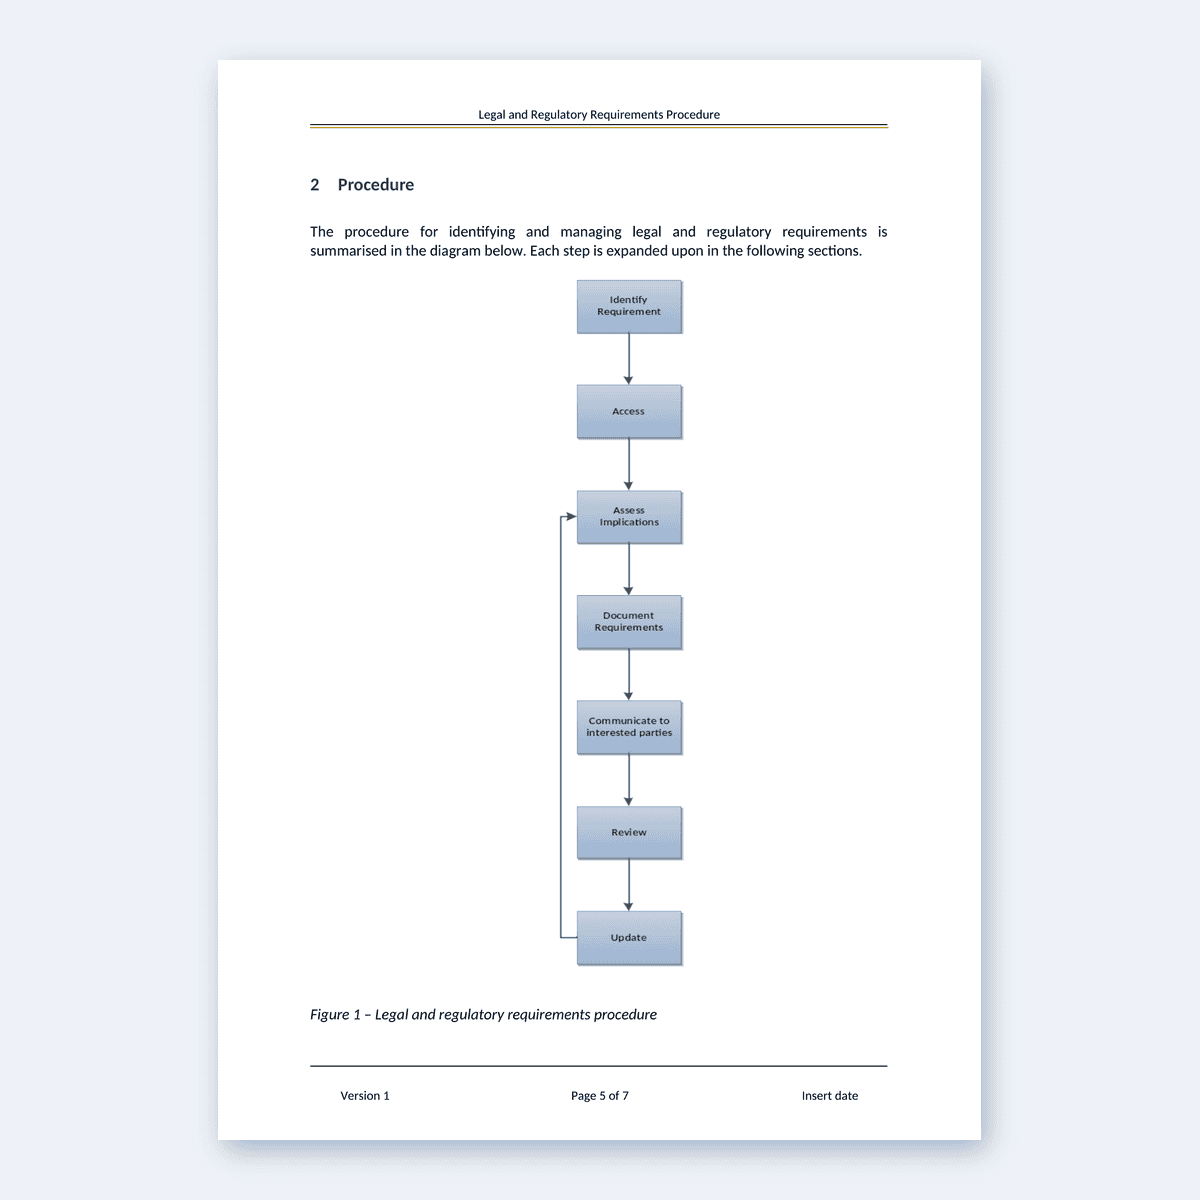
- Legal and Regulatory Requirements Procedure
- Management Support Letter
- Media Disposal Procedure
- Mobile Computing Policy
- Network Security Policy
- Physical Security Design Policy
- Physical Security Policy
- Recruitment and New Joiner Checklist
- Remote Working Policy
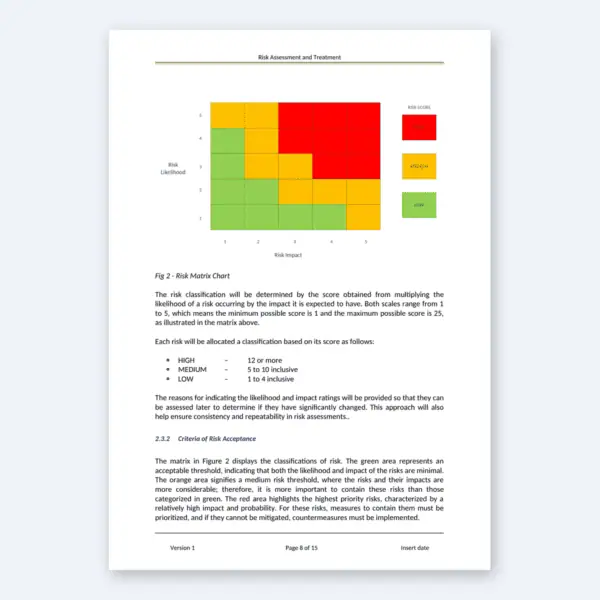
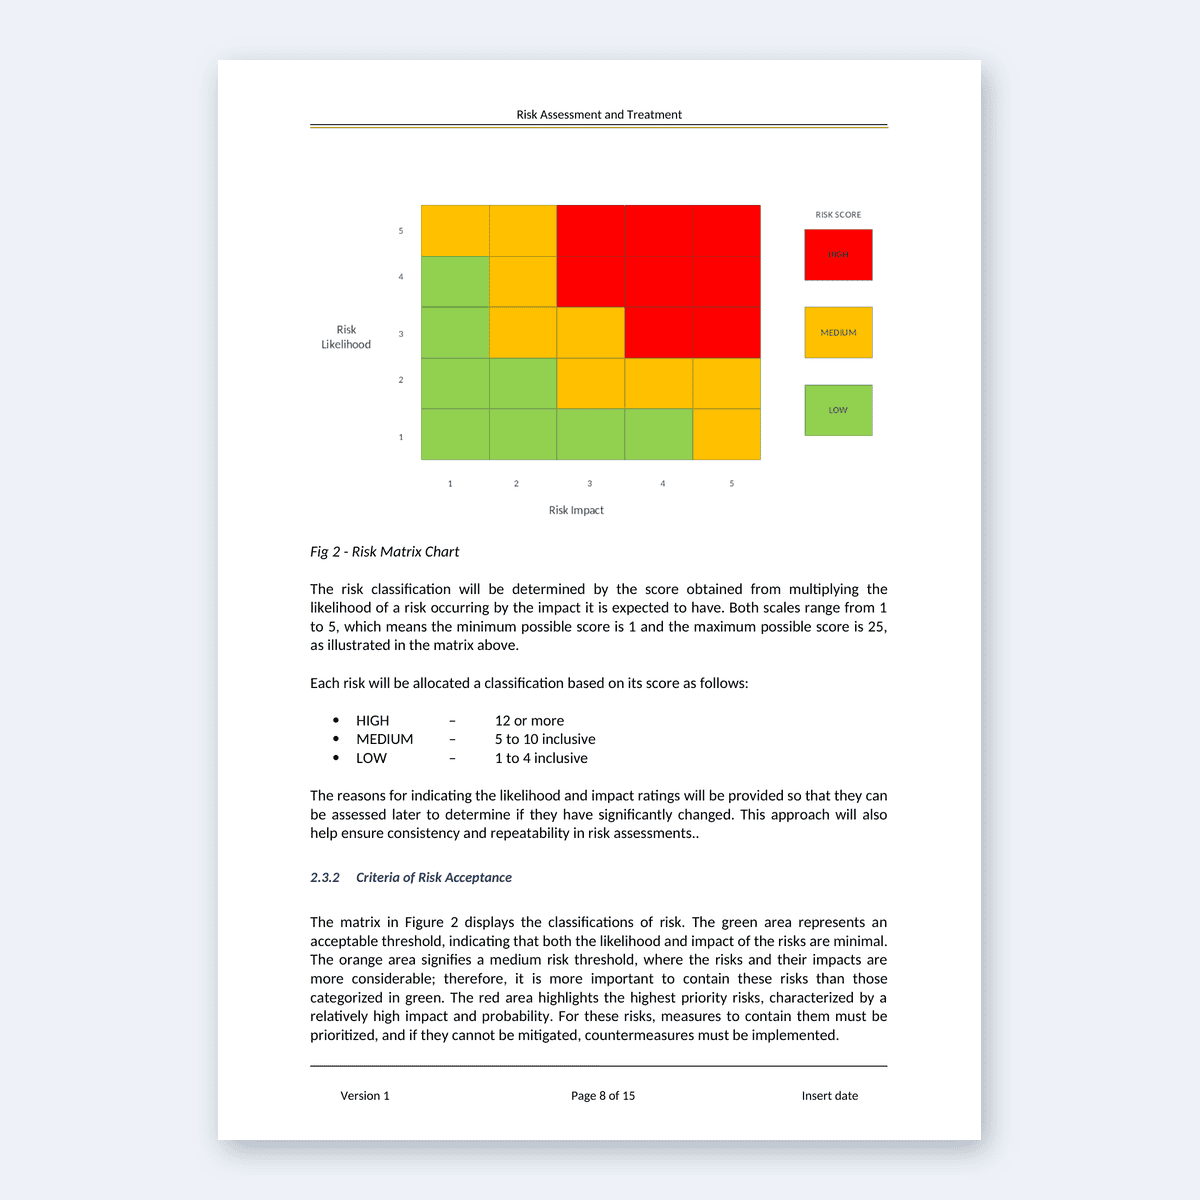
- Risk Assessment and Treatment
- Risk Assessment Report
- Risk Treatment Plan
- Secure Areas Policy
- Secure Coding Policy
- Secure Development Policy
- Security Monitoring Procedure
- Segregation of Duties Policy
- Standard NDA
- Vendor Access Procedure
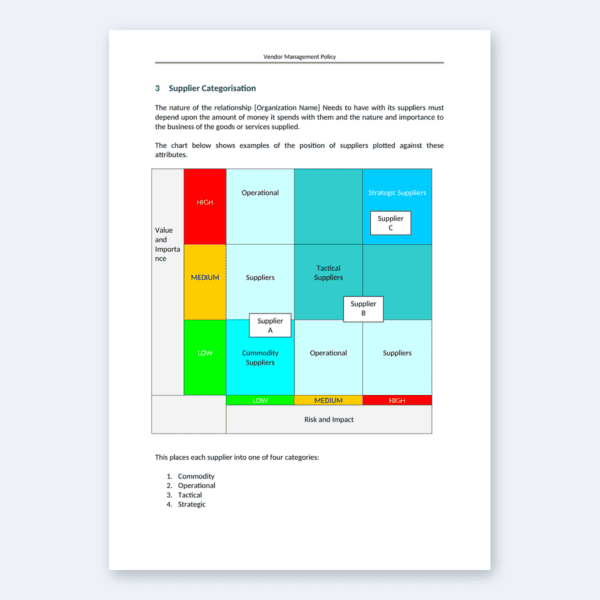
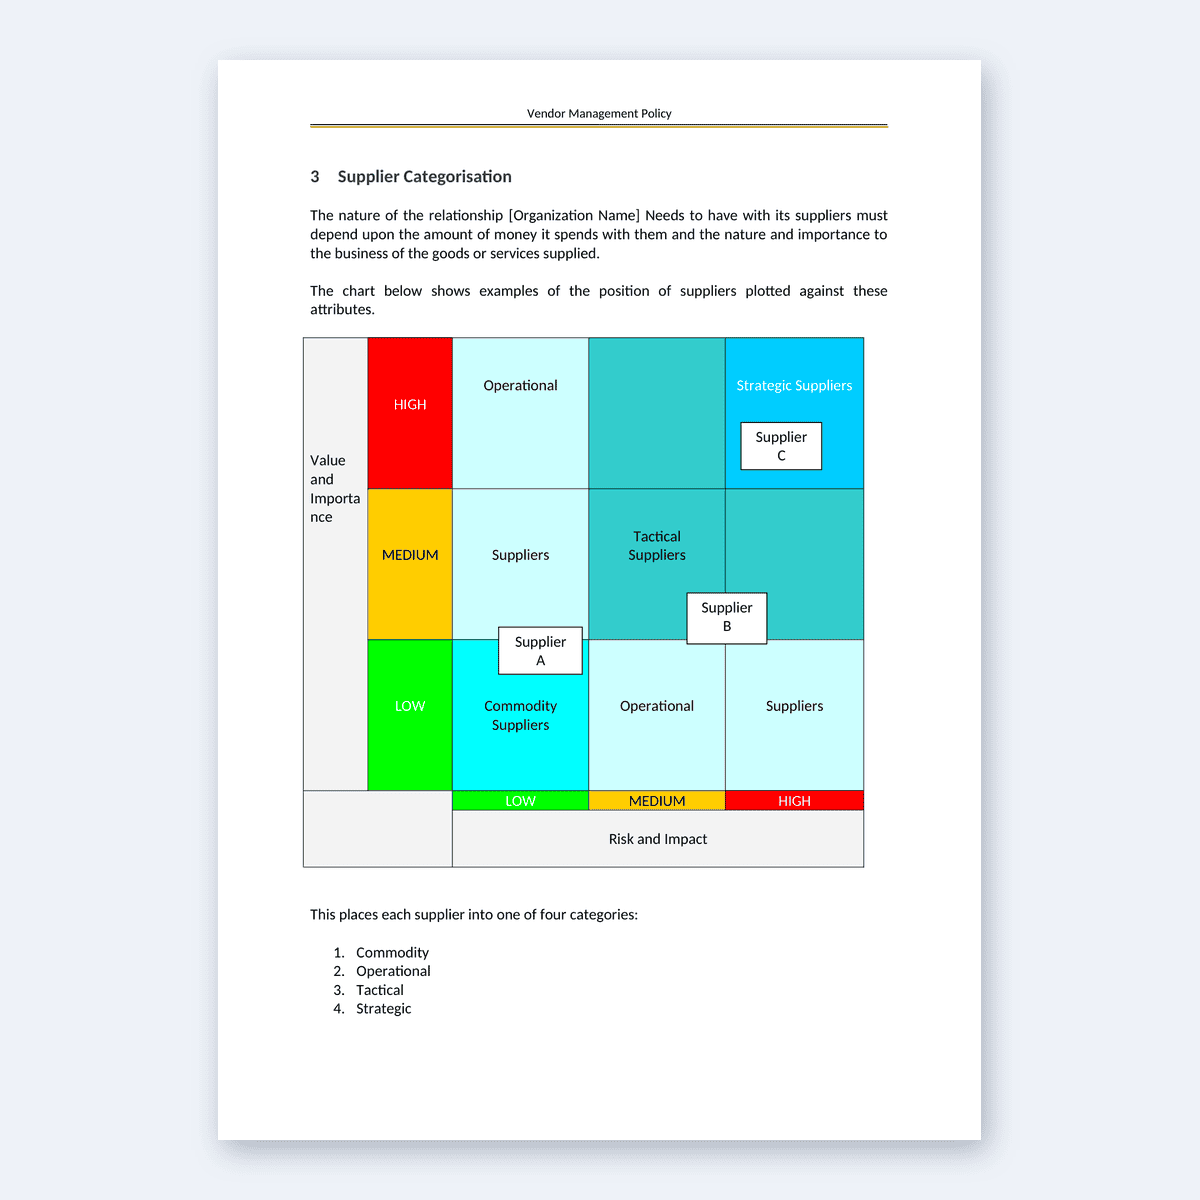
- Vendor Management Policy
- Vendor Security Agreement
- Vulnerability Assessment Procedure
- Vulnerability Management Policy
- Web Filtering Policy
- Security Categorization Worksheet
- System Security Plan Template
- Plan of Action and Milestones Workbook
Why Choose NIST Toolkit?
This toolkit provides a structured, repeatable, and comprehensive approach to risk assessment and cybersecurity governance, ensuring that your organization remains compliant, resilient, and secure. Designed for CISOs, risk managers, IT security teams, and compliance officers, this toolkit eliminates guesswork and accelerates NIST-aligned risk management implementation.
Looking for the Cybersecurity Framework instead?
This toolkit is a risk assessment pack built on NIST SP 800-30. It includes a CSF 2.0 maturity workbook and a CSF 2.0 Organizational Profile (Current and Target Profiles for all 106 Subcategories, a gap summary and CSF Tiers), but it is not a full Cybersecurity Framework implementation pack. If you need a complete document set to run and evidence a CSF 2.0 programme, including crosswalks, see the NIST CSF Toolkit. Organisations that need both usually buy both.
Get Your Security Risks Under Control Today!
Whether you’re looking to strengthen organizational risk management, achieve compliance, or enhance cybersecurity resilience, this toolkit is your ultimate resource to achieving effective information security governance under the NIST frameworks.
This toolkit is built on NIST SP 800-30, the Guide for Conducting Risk Assessments.
Frequently Asked Questions (FAQ)
What is the NIST Cyber Risk Management Toolkit?
The NIST Toolkit is a complete set of 50+ professional templates built on the NIST SP 800-30 risk assessment methodology. It helps businesses manage cybersecurity risks by providing ready-made tools for risk assessment, incident response, compliance checks, and vendor security evaluation.
Who should use the NIST Toolkit?
This toolkit is ideal for CISOs, IT managers, risk officers, consultants, and government agencies. It’s designed for anyone responsible for cybersecurity risk management, compliance, or running a structured risk assessment programme.
What’s included in the NIST Toolkit?
It includes 55 editable Word documents and 6 Excel workbooks: the SP 800-30 risk assessment template and report, the risk treatment plan, a cyber risk management framework, a business impact analysis workbook, a gap analysis workbook, and the security policies and procedures your treatment decisions point to, plus two NIST reference PDFs.
Is the toolkit aligned with NIST SP 800-30?
Yes. The toolkit follows the NIST SP 800-30 risk assessment methodology, and its NIST CSF 2.0 Maturity Assessment Template covers all six Functions of the Cybersecurity Framework—Govern, Identify, Protect, Detect, Respond and Recover—across all 106 Subcategories. Note that CSF 2.0 is voluntary guidance: there is no certification against the Cybersecurity Framework.
Can I customize these NIST documents for my organization?
Absolutely. All templates are editable in Microsoft Office formats. You can easily insert your organization’s name, logo, and data. Automated scoring and built-in risk models make customization quick and effective.
Find More Products:
Implementing for clients? The Consultant Package bundles 92 toolkits — 8,500+ editable templates — under one firm-wide licence that covers unlimited client engagements. $1,399 one-time.
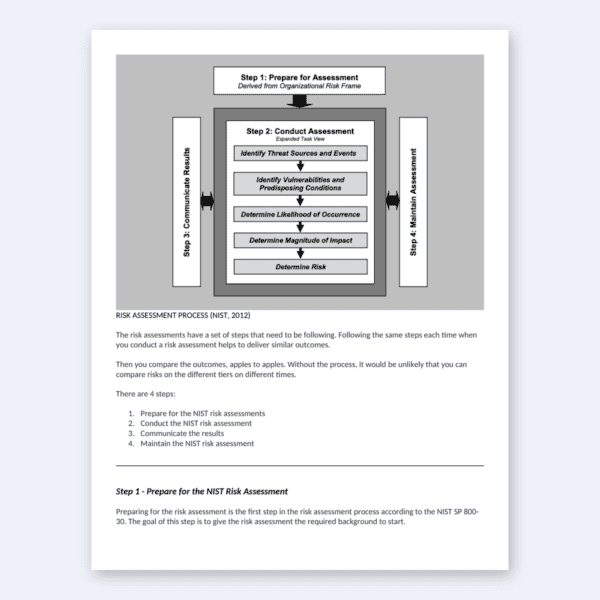
Looking for one document? If you are working from SP 800-30, the process has four steps and each one has to produce something. Our guide to the NIST risk assessment template covers what it has to contain.
Guides for the NIST Cyber Risk Management Toolkit
Free articles that explain the requirements this toolkit covers.

 NIST Cyber Risk Management Toolkit$89.00




Really handy toolkit with clear resources that made managing cyber risks feel much more straightforward.
A well structured and comprehensive toolkit that provides clear, practical resources for managing cybersecurity risks effectively.
This toolkit was super easy to work with and gave me a clear way to organize and manage cyber risks.
A practical resource that makes cyber risk planning clearer and easier to manage.
A thoughtfully organized resource that makes handling cyber risks much more straightforward.