Description
What the report contains
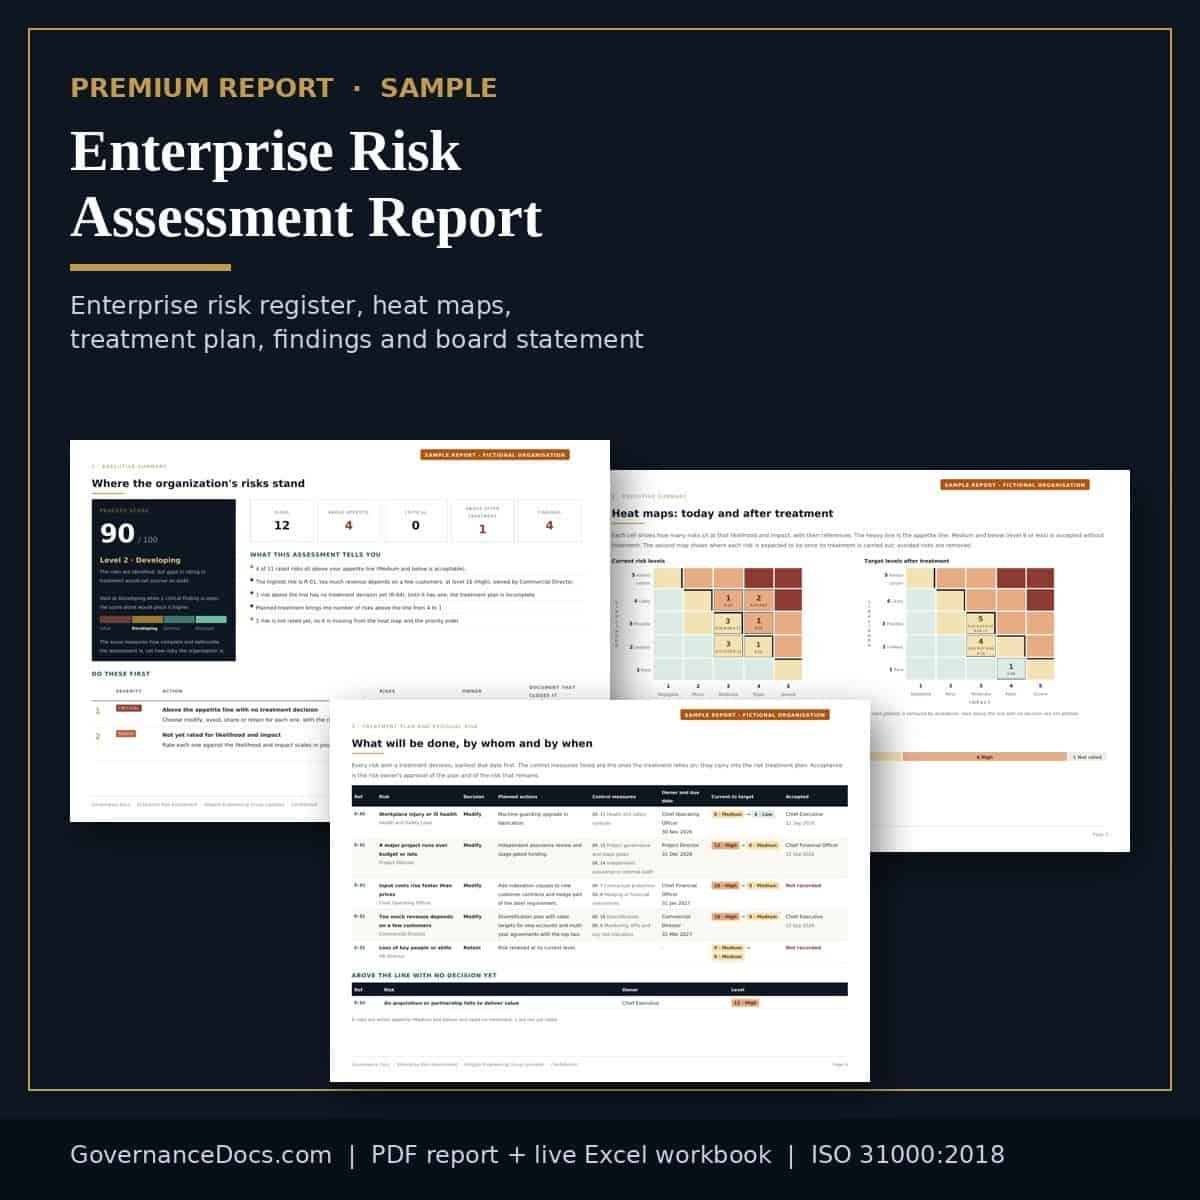
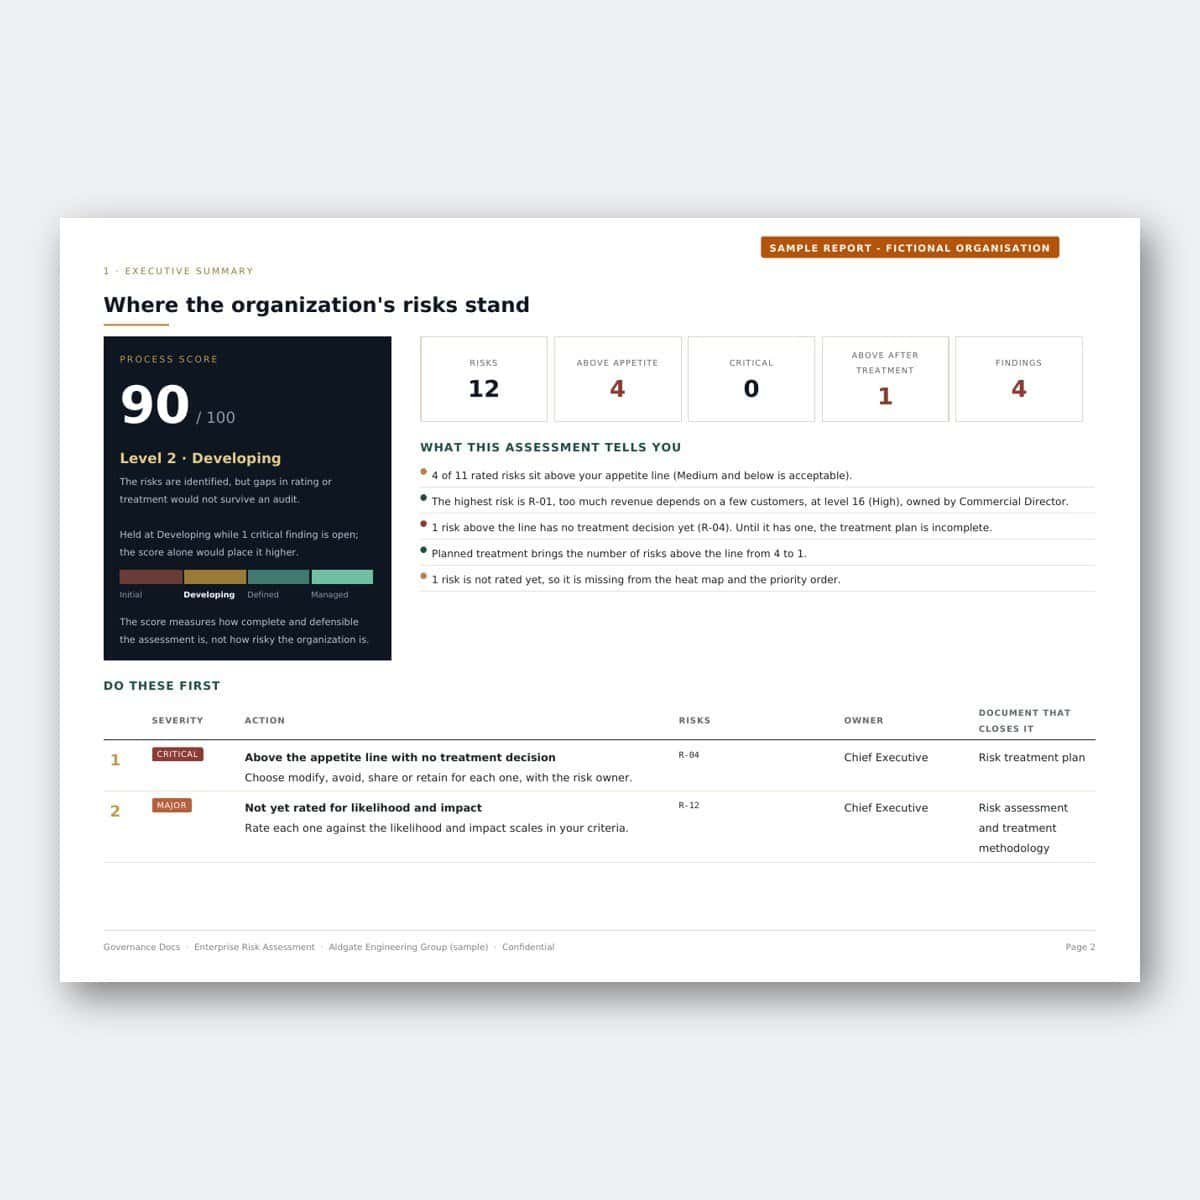
You already have your heat map, your top risks and your findings for free. This is the full assessment behind them, written up as the record an auditor, a board or a risk committee expects to see.
- The complete enterprise risk register, highest level first. Every risk with its owner, the objectives, units, projects and assets it affects, the controls already in place, its likelihood, impact and level, and the rationale for the rating.
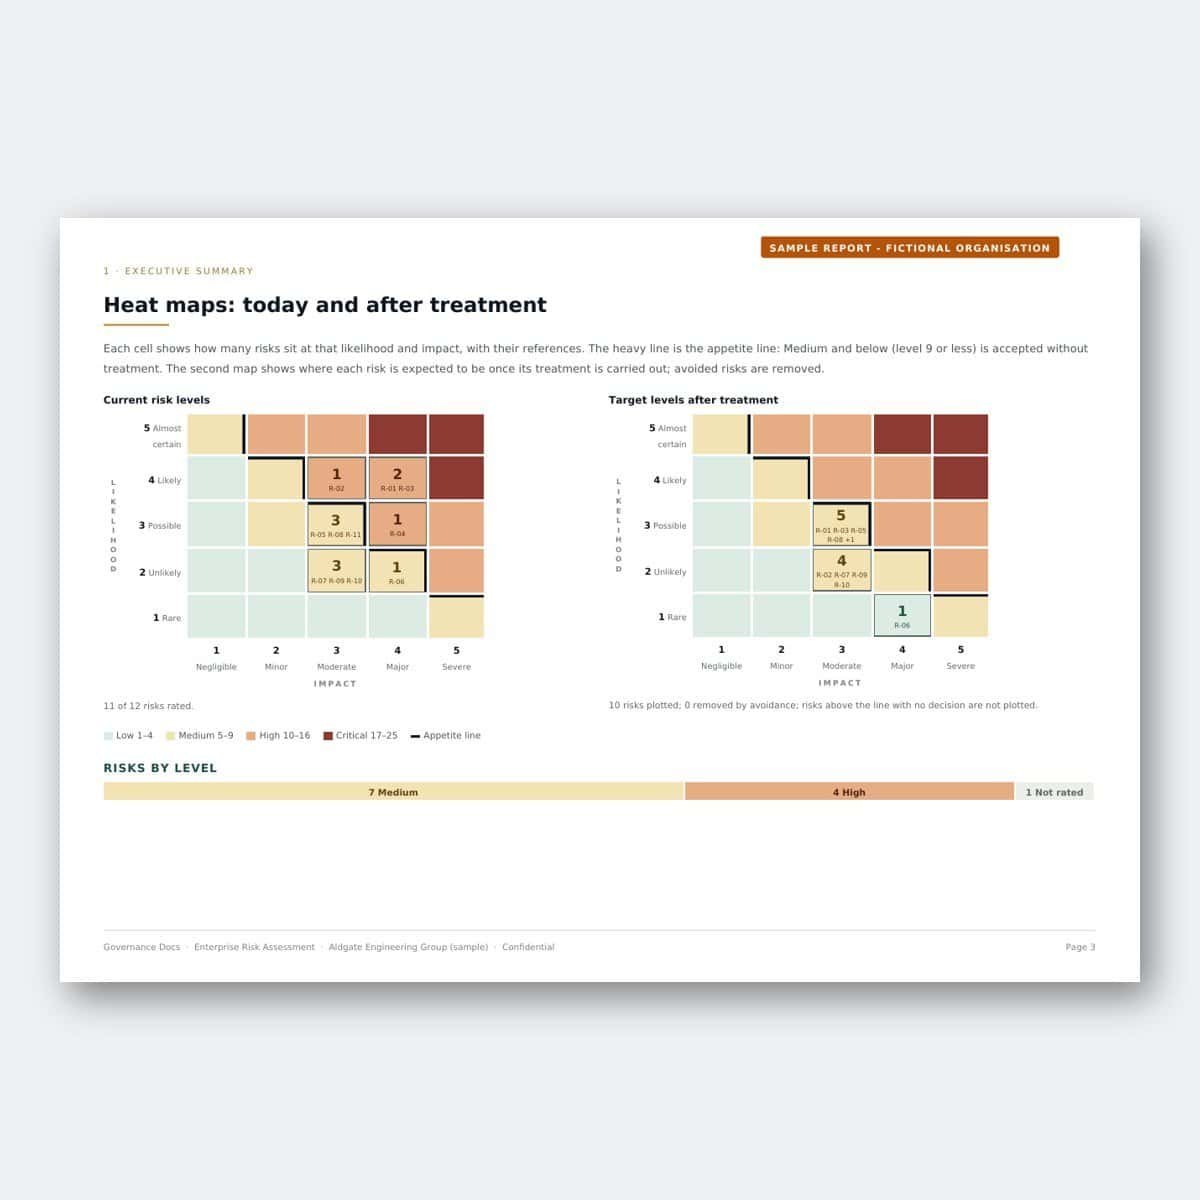
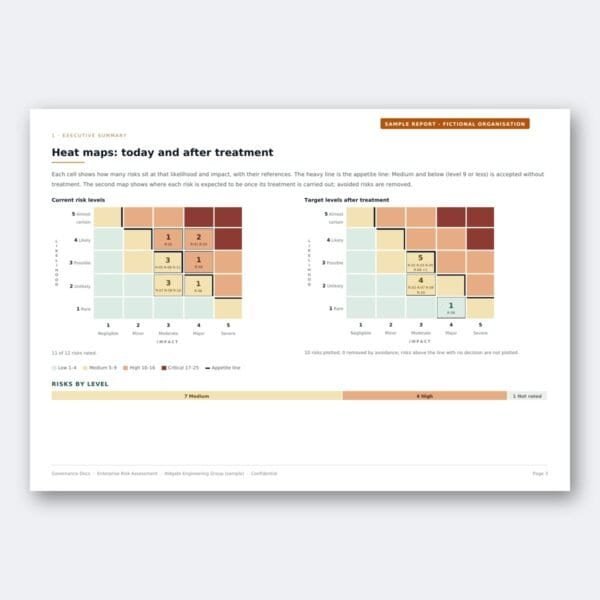
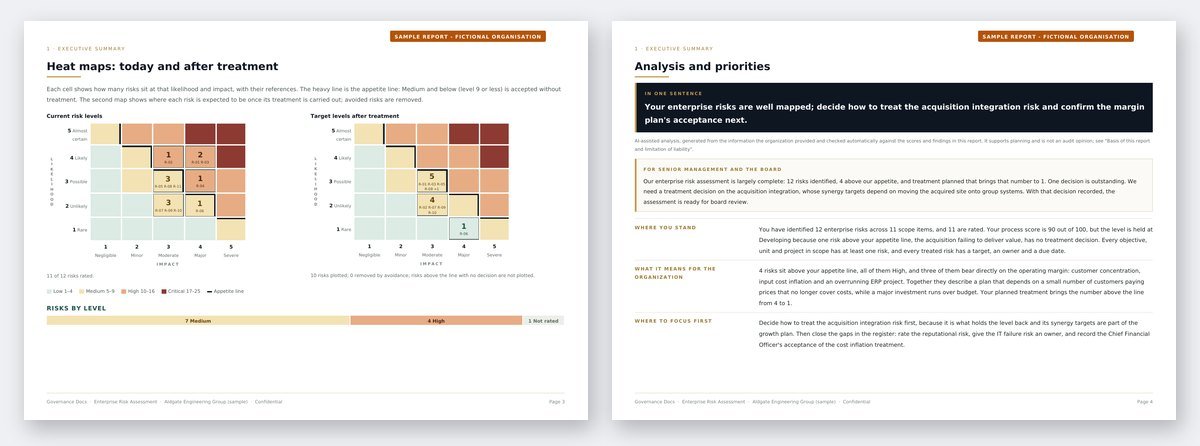
- Heat maps today and after treatment, side by side. Both drawn against your own appetite, so a board can see at a glance what the treatment plan achieves.
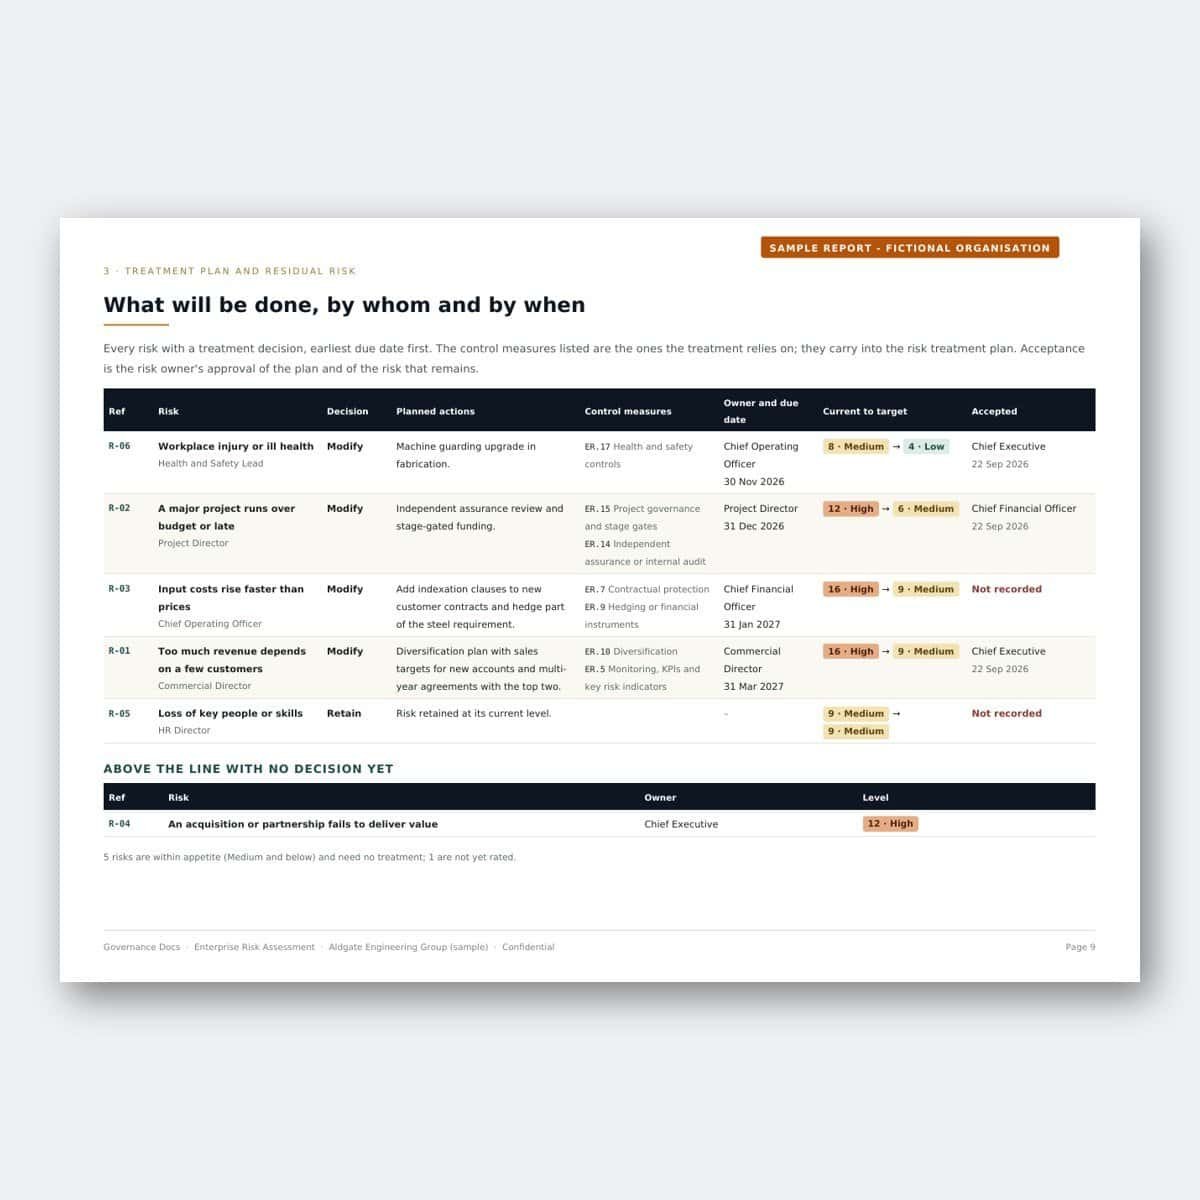
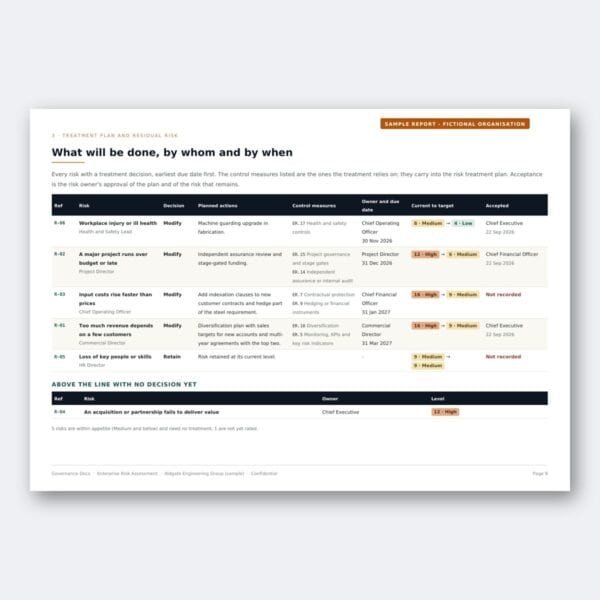
- The treatment plan by due date. For each risk: the decision, the planned actions, the kinds of control it relies on, the owner, the due date, the current and target level, and the risk owner’s acceptance.
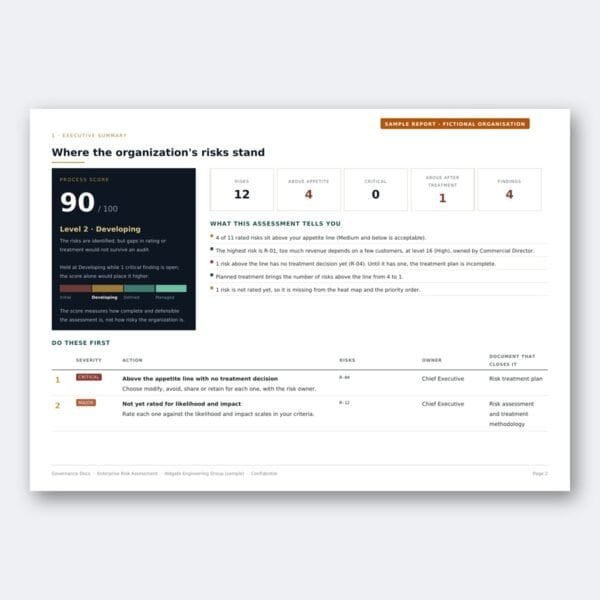
- Every finding, with what closes it. Each gap between your assessment and what ISO 31000 clauses 6.4 and 6.5 describe, the risks it applies to, what to change, and the document that closes it.
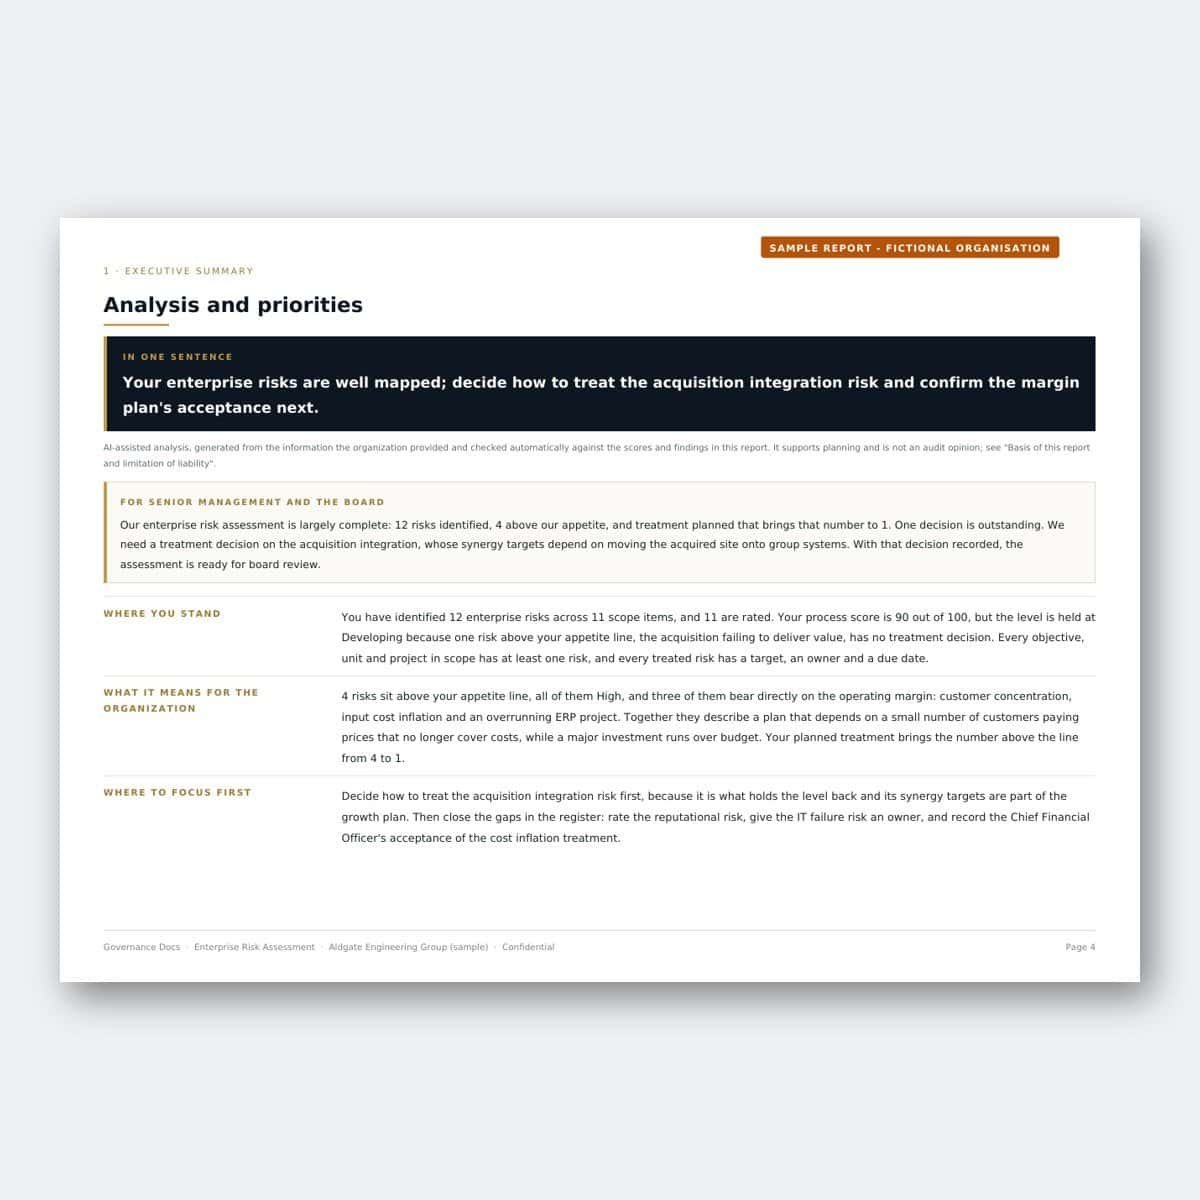
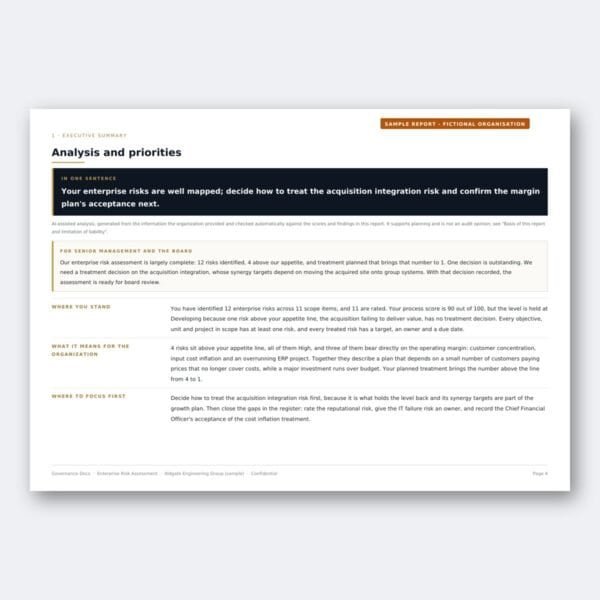
- An AI-assisted analysis and 30/60/90-day roadmap. A one-sentence verdict, where you stand and what it means, a statement for senior management, three to five priorities and a roadmap, written from your own ratings and checked automatically against them.
- Your process score in detail. Nine weighted dimensions, from criteria and ownership to treatment and residual risk acceptance, so you can see exactly where the assessment is thin.
- Your criteria, written up. Likelihood and impact scales, risk bands and the appetite line every rating was made against.
- What changed since last year. Run next year’s review from this register and the report shows which risks were added, closed or moved level, and how the headline figures changed.
The live Excel workbook
A risk register is only useful if it can be kept up to date when something changes, so you also get the register as a working file, not a static export:
- Dashboard: the process score, level and heat maps, recalculated as you edit.
- Criteria: your scales, band ceilings and appetite line, which drive every calculation.
- Scope and Risk register: change a likelihood or impact and the level, band and appetite check update.
- Treatment plan: decisions, actions, owners, due dates, targets and acceptance.
- Control measures: the catalogue of control types, with those your treatments rely on marked as selected and the risks they treat listed, so monitoring and assurance know what to test.
How to get it
- Run the free enterprise risk assessment: set your criteria, list what is in scope, pick risks from the library, rate them and decide how to treat each one.
- See your heat map, top risks and findings free on the result page.
- Choose Get the full report. The report and workbook are in your account straight away, and they rebuild from your latest answers whenever you download them.
Built to ISO 31000:2018 and suitable for a board risk register, a risk committee pack or an annual risk review.
One payment covers this assessment. Edit it as often as you like and download the updated report at no extra cost. This is a self-assessment built from the information you enter; it is not a certification or an audit opinion.

 Critical IT and Cybersecurity Indicators
1 × $39.00


Reviews
There are no reviews yet