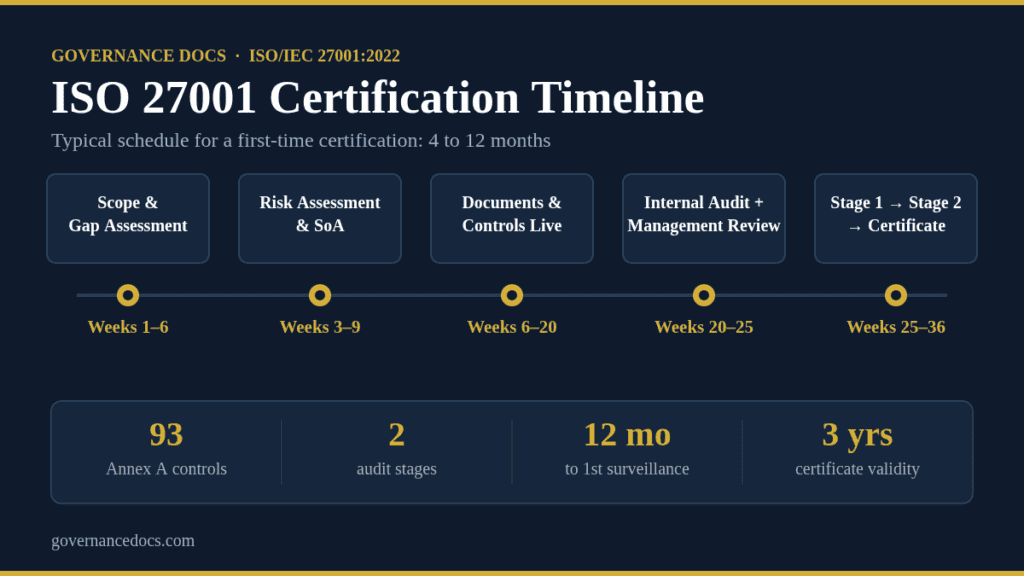
The ISO 27001 certification timeline runs four to twelve months for most first-time organizations, and almost none of that time is spent in the audit itself. The audit is a handful of days. Everything before it — scoping, risk work, writing the documents, running the controls long enough to produce records, then auditing yourself — is what sets the date on the certificate.
That distinction matters because it changes what you can actually compress. Buying a faster certification body does not move the date. Starting your internal audit earlier does.
Free gap assessment
Where do you actually stand against ISO 27001?
Score every management system clause and all 93 Annex A controls, free, and get a prioritised gap list back.
What the ISO 27001 certification timeline really measures
There are two clocks running, and people conflate them. The first is your implementation clock: defining scope, running a risk assessment, selecting controls, writing the Statement of Applicability, and operating the management system long enough that it has a history. The second is your certification body’s clock: stage 1, the gap between stages, stage 2, then an independent certification decision.
Free ISO 27001 risk assessment
Which of your risks sit above your appetite line?
Set your own risk criteria, pick from 61 information security risk scenarios, rate likelihood and impact, and decide how to treat each one. You get a heat map, a process score and the findings an auditor would raise, free.
The second clock is short and fairly predictable. The first one is where projects slip by months. A realistic ISO 27001 certification timeline gives roughly 70% of the calendar to implementation and evidence, and 30% to the audit sequence and the decision that follows it.
The standard itself sets the workload. ISO/IEC 27001:2022, edition 3, published October 2022, carries 93 Annex A controls across four themes — 37 organizational, 8 people, 14 physical and 34 technological. You do not implement all 93. You justify every inclusion and exclusion in the Statement of Applicability, which clause 6.1.3 makes mandatory. That justification exercise, done honestly, is a multi-week task on its own.
The ISO 27001 certification timeline, phase by phase
The ranges below are typical for a company of 20 to 200 people with a single main site or a cloud-hosted product. Larger scopes, multiple legal entities and regulated data stretch every row.
Phase
Typical duration
What ends it
Scope definition and gap assessment
2–6 weeks
A written scope statement and a ranked list of gaps
Risk assessment and risk treatment plan
3–6 weeks
Approved risk treatment plan and a completed Statement of Applicability
Documentation build
4–10 weeks
Policies, procedures and registers approved and issued
Control implementation
6–16 weeks
Controls live, running in parallel with documentation
Evidence accumulation
6–12 weeks
Enough records to sample — typically at least one quarter
Internal audit and management review
3–5 weeks
Both completed, findings raised and actioned
Stage 1 audit
1–2 days on site
Readiness report from the certification body
Gap between stage 1 and stage 2
4–8 weeks typical
Stage 1 findings closed
Stage 2 audit
2–5 days on site
Audit report with any nonconformities
Nonconformity closure and certification decision
2–12 weeks
Certificate issued
Phases overlap, and the published ISO 27001 certification timeline ranges above assume they do. Documentation and control implementation should run together, not in sequence, and evidence starts accumulating the day a control goes live rather than after everything is approved. Run them properly in parallel and a 12-month ISO 27001 certification timeline compresses to seven or eight.
Four gates that set your ISO 27001 certification timeline
Four specific things gate the date. Miss any one and the stage 2 audit either gets postponed or fails.
1. One completed internal audit. Your certification body will look for evidence that you audited your own management system before asking anyone else to. Not a gap assessment, not a readiness check — a documented internal audit against the standard, with findings.
2. One completed management review. Same principle. Top management has to have met, reviewed the defined inputs, and made decisions that are minuted. A review scheduled for the week after stage 2 is the single most common reason a certification slips a quarter.
3. Enough operating evidence to sample. There is no clause that says “three months of records.” What the standard requires is a management system that demonstrably operates, and an auditor cannot sample records that do not exist. Most certification bodies are comfortable with a quarter of live operation across access reviews, incident handling, change records and supplier checks.
4. Certification body availability. Accredited auditors are scheduled months out. Engage a body while you are still writing documents, not once you are ready — a four-week delay here is common and completely avoidable.
What the audit stages add to the ISO 27001 certification timeline
Initial certification is a two-stage audit under ISO/IEC 17021-1, and the number of audit days is not negotiable guesswork. It is calculated under Annex C of ISO/IEC 27006-1:2024, driven mainly by the effective number of people in scope, the number of sites and the complexity of what you do.
Stage 1 is a documentation and readiness review. The auditor confirms the scope, reads the policy, the risk assessment and the Statement of Applicability, and checks that your internal audit and management review have happened. Stage 2 is the certification audit proper, where the auditor samples evidence to confirm the controls you selected are implemented and working.
ISO/IEC 17021-1 does not prescribe a fixed interval between the two stages. Certification bodies set their own, and four to eight weeks is the norm; longer gaps are usually granted only where stage 1 raised something substantial. If the gap runs too long, some bodies will repeat elements of stage 1 — which adds cost and days you did not plan for.
After stage 2, the report goes to an independent reviewer inside the certification body who makes the certification decision. That review typically takes two to six weeks. Where stage 2 raised a major nonconformity, the certificate is held until it is closed, and most bodies allow roughly 90 days for initial certification before a partial re-audit is triggered. Minor findings are usually accepted with a corrective action plan and verified at the first surveillance audit. Our guide to ISO 27001 nonconformities covers the major-versus-minor distinction in detail.
Three realistic scenarios
Fast
Typical
Slow
Elapsed time
4–5 months
7–9 months
12–18 months
Starting point
SOC 2 or equivalent program already running
Some security controls, no management system
Nothing documented, scope still contested
Scope
One product, one entity, cloud only
One entity, a couple of offices
Multiple entities, on-premise estate, regulated data
Documentation approach
Templates tailored
Templates plus consultant review
Written from scratch internally
Main risk to the date
Certification body availability
Evidence period and internal audit
Scope churn and executive attention
The slow column is not a story about incompetence. It is almost always a scope that keeps moving. Every scope change re-opens the risk assessment, which re-opens the Statement of Applicability, which re-opens the documents. Freeze the scope early and defend it — it is the highest-leverage decision in the whole ISO 27001 certification timeline.
Life after the certificate: the three-year cycle
The certificate is valid for three years, and the cycle starts on the date of the certification decision, not on the last day of your stage 2 audit. Two dates then matter permanently.
The first surveillance audit must take place no more than 12 months from the certification decision date. That is a boundary, not a target, and missing it puts the certificate at risk. Surveillance audits then continue at least annually except in the recertification year, and each one takes roughly a third of the initial audit time. The recertification audit happens in year three, before expiry, and takes around two thirds of the initial audit time. If you want the detail, see our guide to the ISO 27001 surveillance audit.
One planning note for 2026: the 2013 to 2022 transition period closed on 31 October 2025, so every valid certificate now sits against ISO/IEC 27001:2022. The 2024 climate amendment, which added climate considerations to the context and interested-parties clauses, is a free amendment and does not require a separate transition project — but auditors do ask whether you have considered it.
How to compress an ISO 27001 certification timeline
Four things reliably save months. Freeze the scope in week one and write it down. Start the documentation set from tailored templates rather than a blank page — document authoring is the largest single block of effort in most projects, and it is the one place where a purchased starting point converts directly into calendar time saved. Run controls and documentation in parallel so evidence starts accruing early. And book the certification body before you feel ready.
Three things do not help, whatever you are told. Paying for an expedited audit does not shorten the evidence period. Skipping the gap assessment saves two weeks now and costs six later — our ISO 27001 gap assessment guide explains what the four outputs should be. And treating the internal audit as a formality reliably produces a major nonconformity at stage 2.
Cost tracks the timeline closely, because most of the spend is people-time rather than audit fees. The full breakdown is in our ISO 27001 certification cost analysis, and if you are still deciding whether to start at all, is ISO 27001 worth it works through the payback case.
Frequently asked questions
How long does ISO 27001 certification take for a 30-person company? Six to nine months is realistic from a standing start, which is the middle of the published ISO 27001 certification timeline range. Four to five is achievable if you already run a SOC 2 program, because the control evidence largely exists and the work is mapping it to Annex A and building the management system layer on top.
Can I be certified without a full three months of records? Sometimes, but it is the auditor’s call, not yours. The requirement is a management system that demonstrably operates. With a narrow scope and dense records some bodies accept less, but planning for under a quarter of evidence is planning to be postponed.
What happens if we fail stage 2? You do not usually “fail” outright. You receive nonconformities. Majors must be corrected and verified before the certificate is issued, typically within about 90 days for initial certification; miss that and a partial or full re-audit follows. Minors are normally closed out with a plan and checked at the first surveillance audit.
Does buying a documentation toolkit actually shorten the ISO 27001 certification timeline? It shortens one phase — documentation — which is typically four to ten weeks of the project. It does nothing for the evidence period or the audit schedule. Treat it as removing the blank-page problem, not as a shortcut to the certificate.
When does the three-year clock start? On the certification decision date, which is usually two to six weeks after your stage 2 audit ends. Your first surveillance audit is due within 12 months of that date.
Where to start
The single largest block of elapsed time in an ISO 27001 certification timeline is producing the documented information the standard requires — the policies, the risk methodology, the Statement of Applicability, the registers and the audit records. Starting those from tailored templates rather than a blank page is the one lever that moves the date without cutting corners on evidence.
Our ISO 27001 Toolkit is built for exactly that phase: 165 templates in Microsoft Office format, aligned to ISO/IEC 27001:2022 and its 93 Annex A controls, with example text you tailor rather than invent. It is $99 and it replaces the slowest part of the schedule.