-
×
 ISO 45001 Toolkit - Comprehensive 50+ Templates
1 × $99.00
Subtotal: $99.00

This is the most comprehensive NIS2 compliance documentation toolkit currently available.
The documents are created in Microsoft Office format and are ready to be tailored to your organization’s specific needs. As well as standard format and contents, this NIS2 Documentation Toolkit includes example text that is clearly highlighted to illustrate the type of information that needs to be provided regarding your organization. Full example documents are also included to help you with your implementation of Directive (EU) 2022/2555.
$99.00
✓ In stock — instant download after checkout
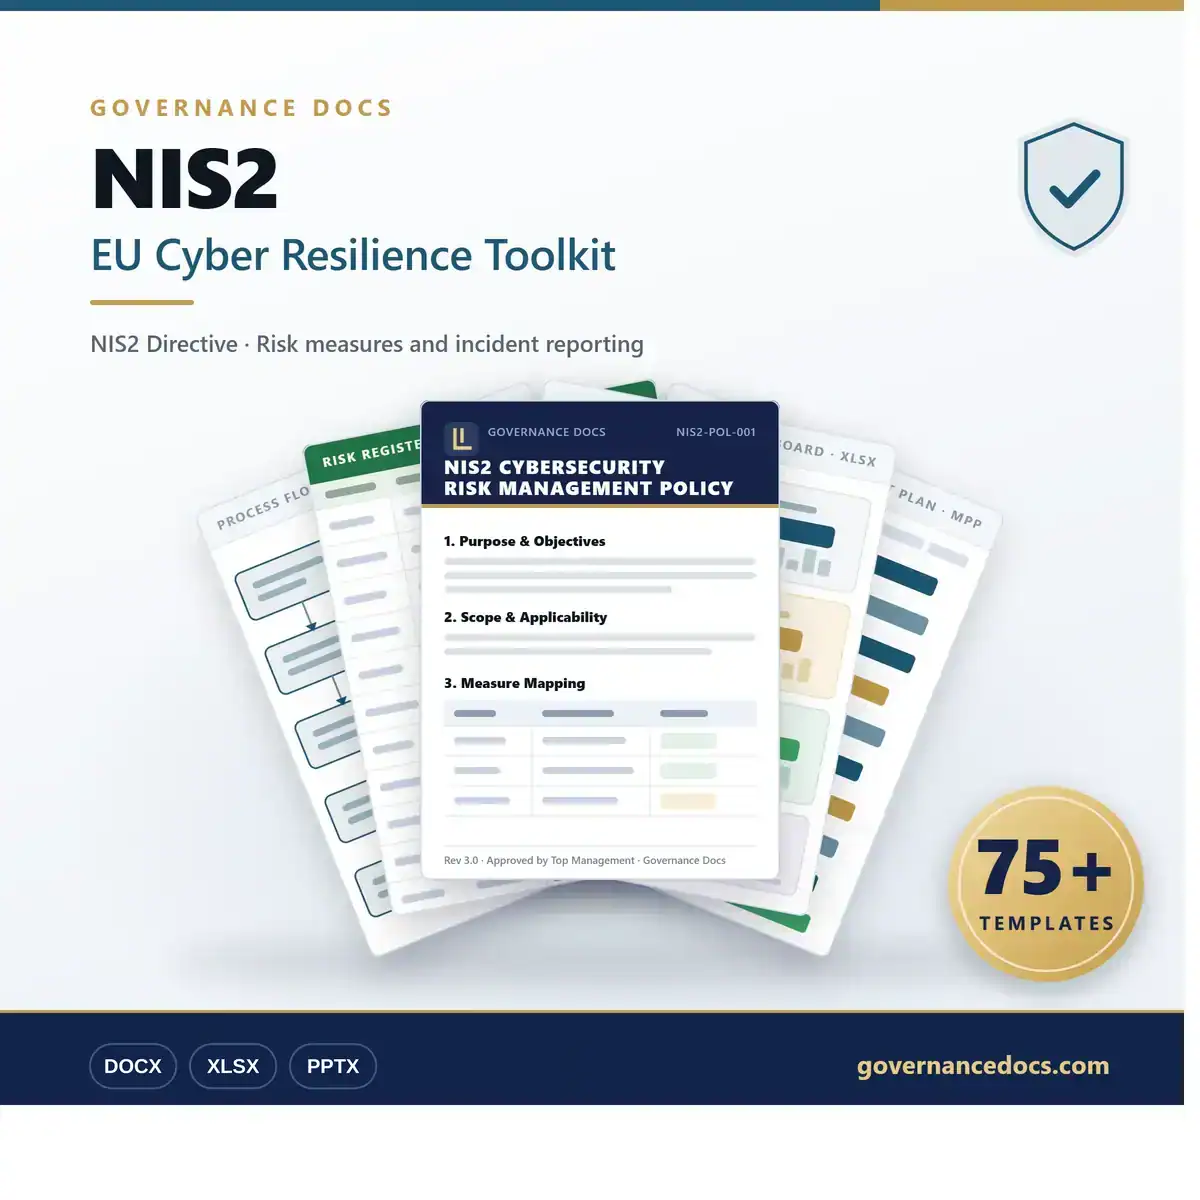
This NIS2 Toolkit is the most comprehensive resource currently available for implementing a cybersecurity compliance programme in accordance with Directive (EU) 2022/2555 (NIS2).
Developed in Microsoft Office format, the documents are fully customisable to address your organisation’s unique requirements. Each template is structured with standard content and includes clearly highlighted example text to guide users in providing the necessary organisation-specific details. Additionally, full example documents are included to support a smooth and effective implementation process.
This toolkit not only simplifies your NIS2 compliance journey but also serves as a vital resource for awareness and training in cybersecurity best practices. Designed for business leaders, compliance professionals, and expert cybersecurity consultants, it provides structured guidance to streamline your path toward NIS2 conformance. Whether you’re seeking to establish a solid cybersecurity governance foundation or strengthen existing controls, this toolkit ensures you have the right resources and support for a seamless compliance process. Enhance Your NIS2 Implementation with Expert Support and Training.
Authored by a CISSP-certified auditor with over 20 years of experience in Information Security, this NIS2 Toolkit encapsulates decades of expertise and practical knowledge in a user-friendly, ready-to-use format.
Governance Docs have created this pack to comply with Directive (EU) 2022/2555 (NIS2) and its associated technical guidelines, including ENISA recommendations and relevant implementing acts.
NIS2 Cybersecurity Compliance Documentation Pack.
A complete and comprehensive documentation package designed to assist clients, consultants, and service providers in successfully achieving compliance with Directive (EU) 2022/2555 (NIS2).
Acceptable Use and Communications Policy.docx
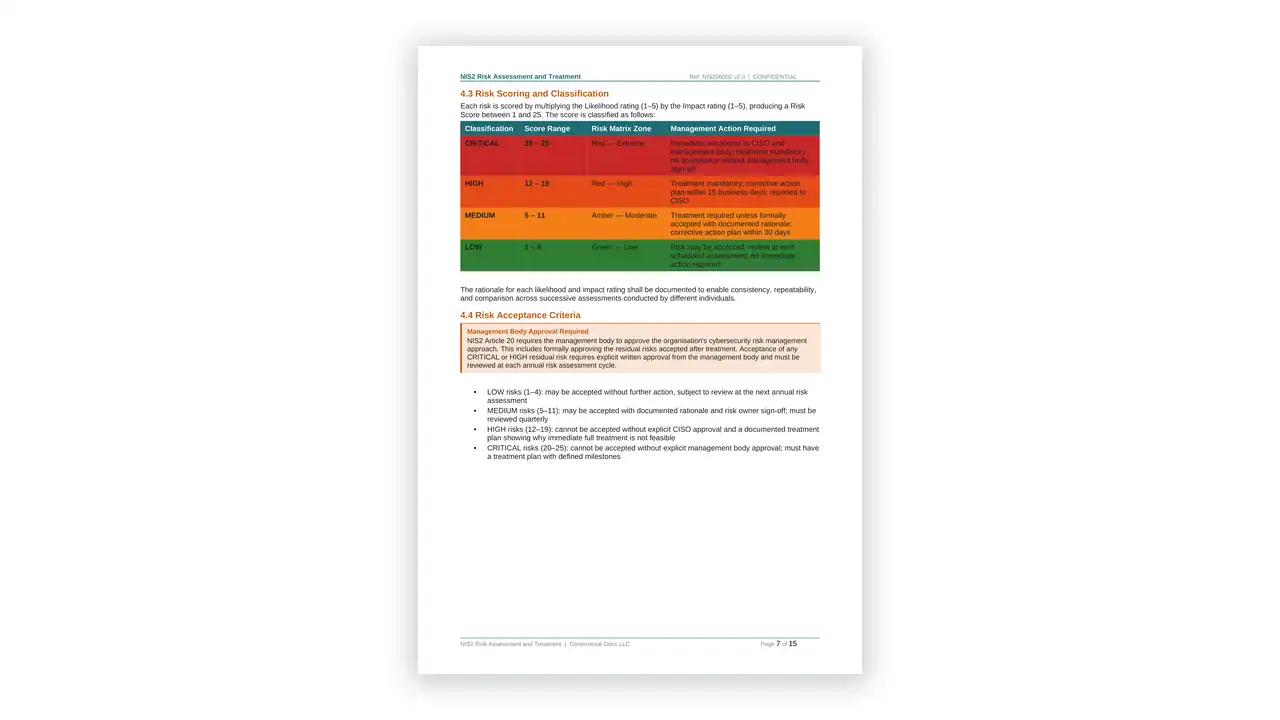
Acceptance of Residual Risks.docx
Access Control Identity Management Policy.docx
Asset and Information Handling Policy.docx
Backup and Recovery Policy.docx
BCM Crisis and Operational Resilience Plan.docx
Business Continuity Exercising and Testing Plan.docx
Business Continuity Exercising and Testing Report.docx
Cloud Services Security Policy.docx
Communication Plan.docx
Configuration Management Procedure.docx
Cryptographic Policy.docx
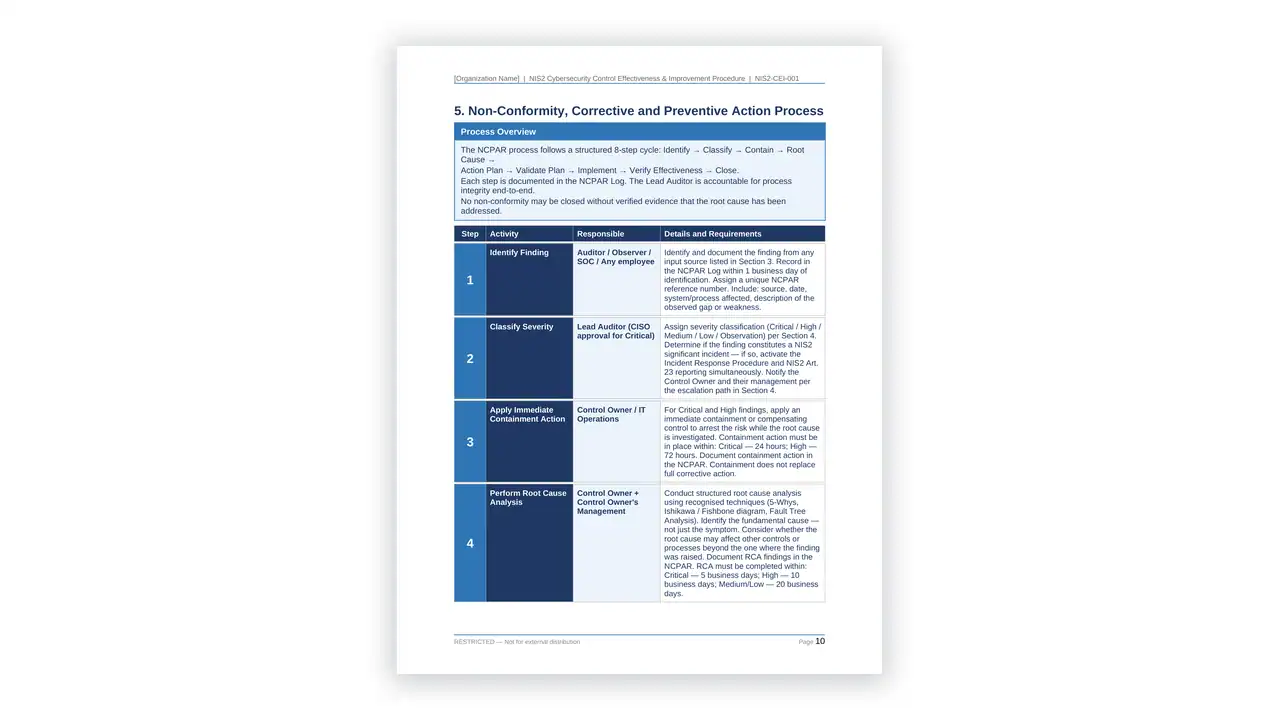
Cybersecurity Control Effectiveness and Improvement Procedure.docx
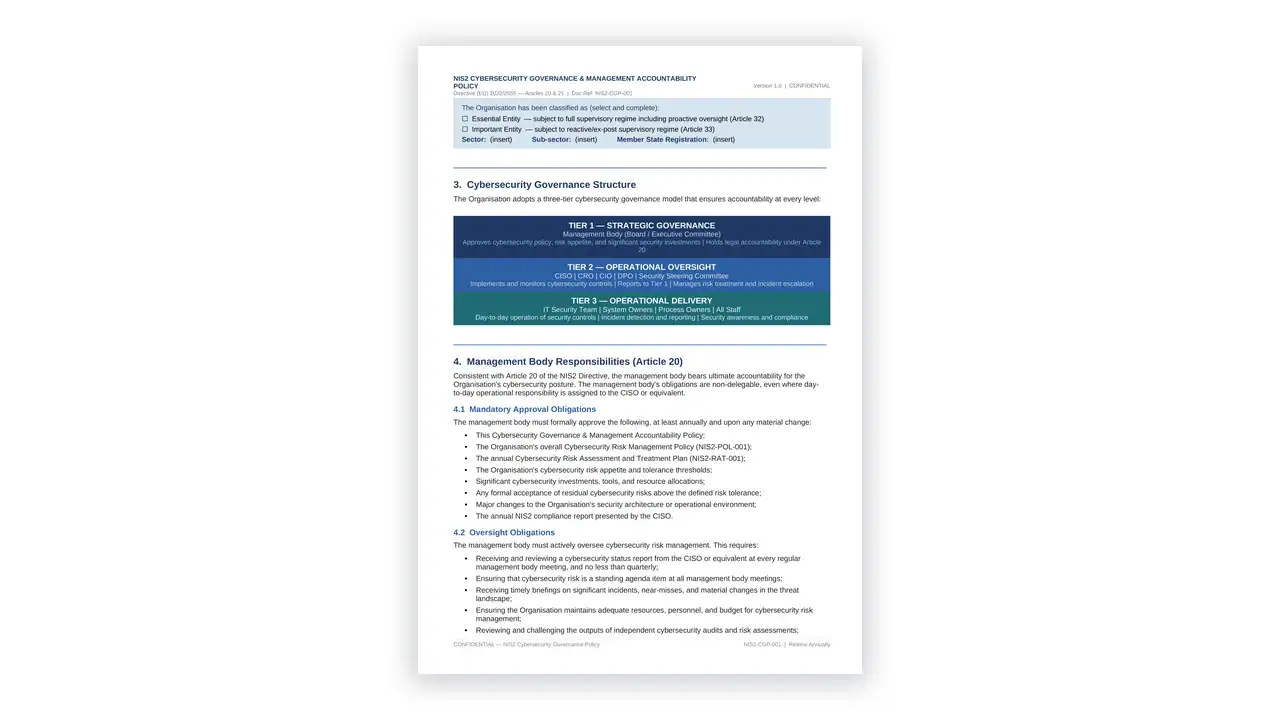
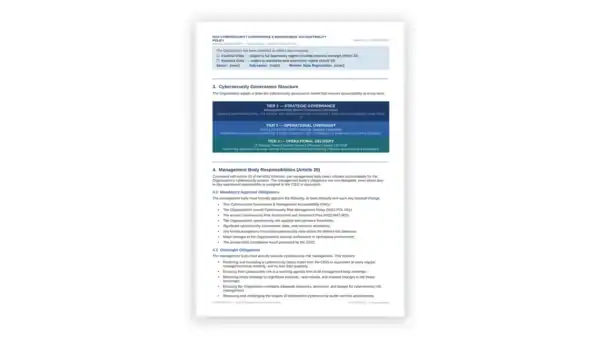
Cybersecurity Governance Management Accountability Policy.docx
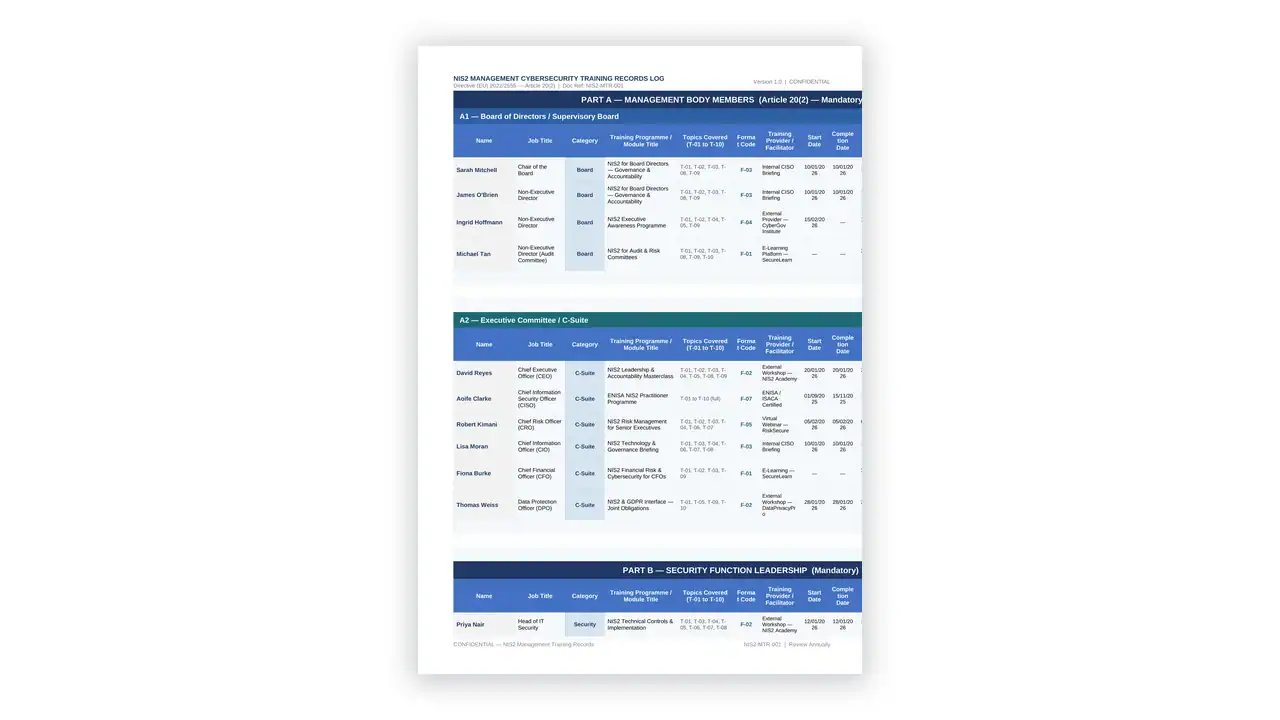
Cybersecurity Training Records Log.docx
Data Loss Prevention Policy.docx
Data Masking Pseudonymisation Policy.docx
Data Restoration Form.docx
Development Environment Policy.docx
Directory of Suppliers and Service Providers.docx
Employee Movement and Termination Checklist.docx
Employment Contract Cybersecurity Clauses.docx
ICT Change Management and Secure Configuration Policy.docx
Information Asset Valuation Guideline.docx
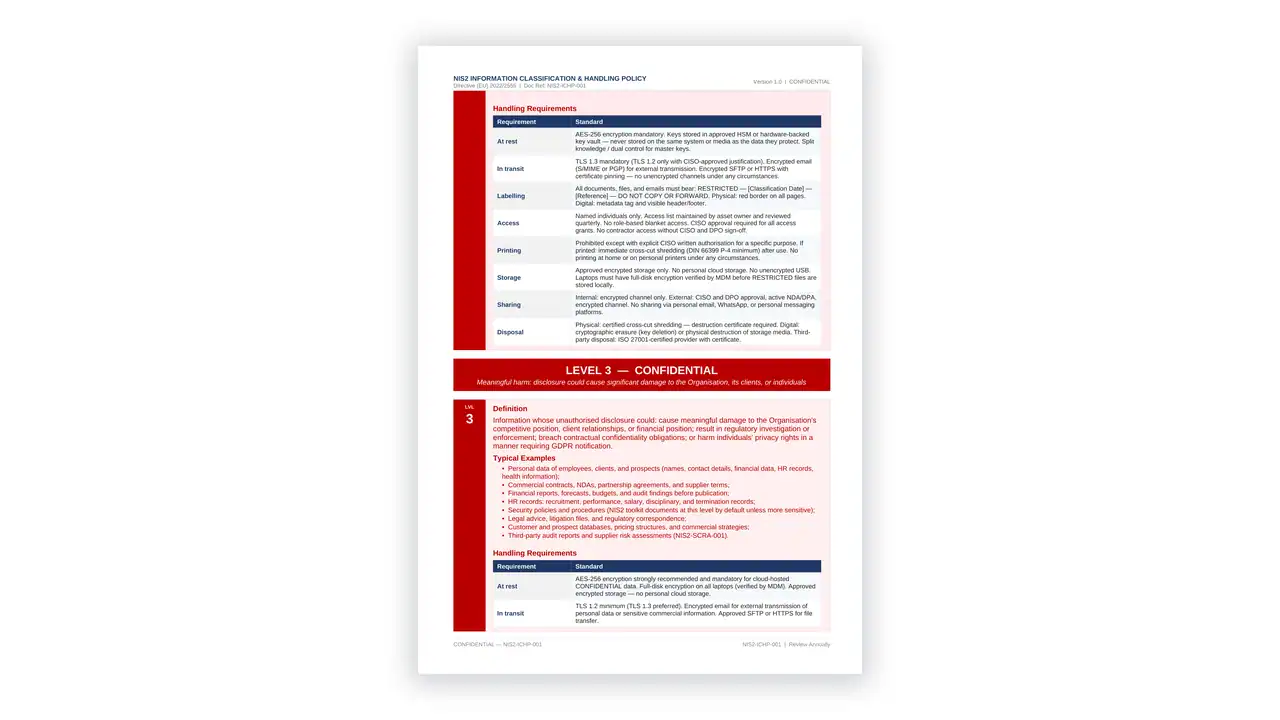
Information Classification and Handling Policy.docx
Information Data Lifecycle Management Policy.docx
Information Transfer and Secure Communications Procedure.docx
Internal Audit and Compliance Review Procedure.docx
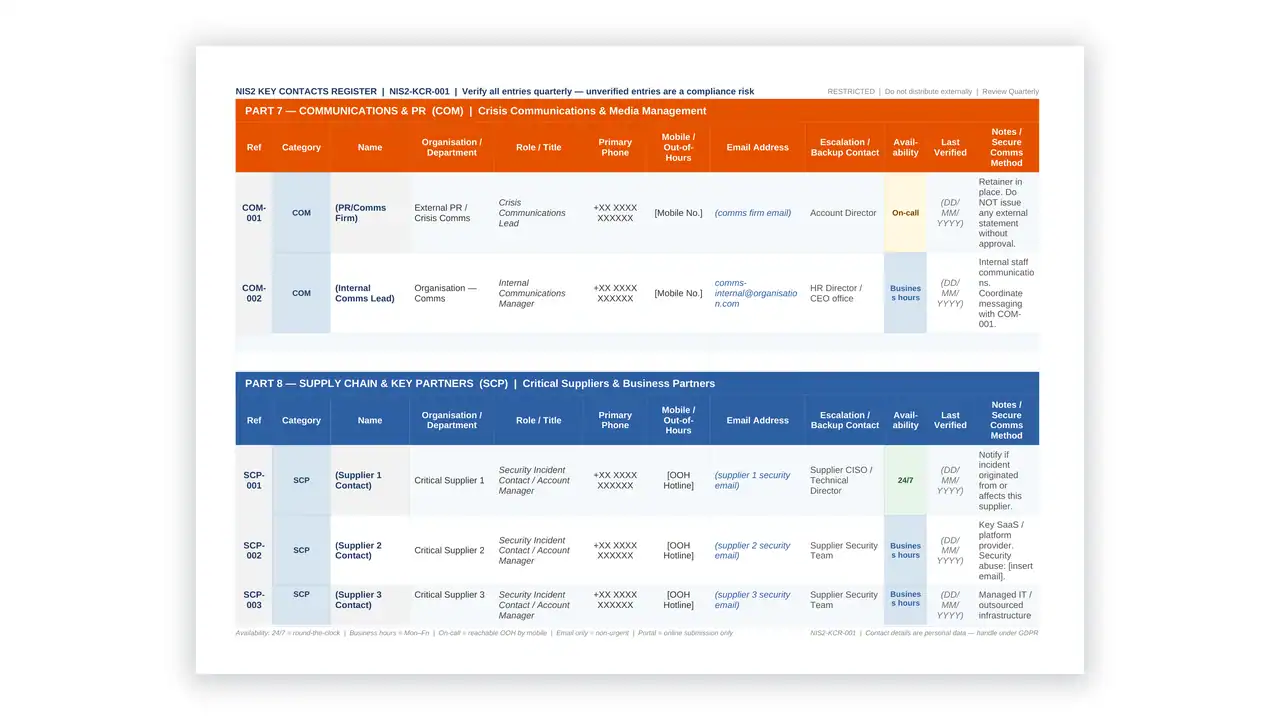
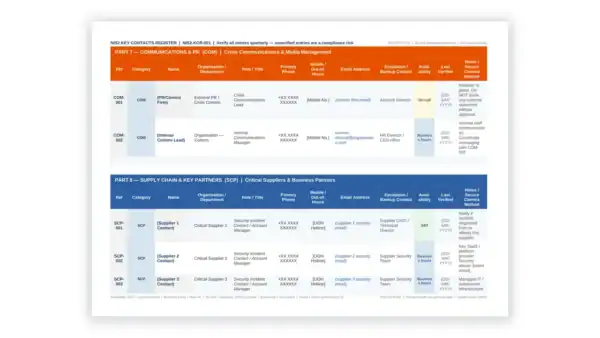
Key Contacts Register.docx
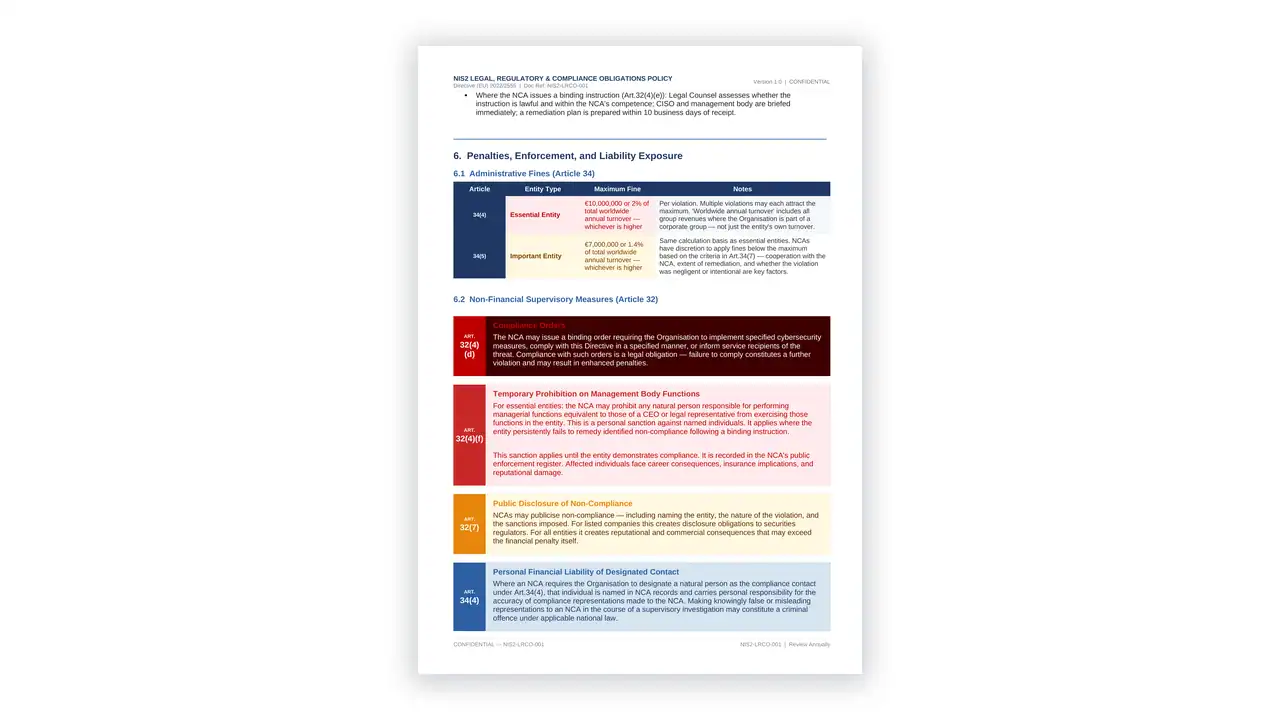
Legal Regulatory and Compliance Obligations Policy.docx
Malware & Cyber Threat Protection Policy.docx
Minor Incident Response Procedure.docx
Mobile Computing and Remote Access Policy.docx
Network & Information Systems Monitoring Procedure.docx
Network Security and Segmentation Policy.docx
NIS2 Audit Plan.docx
NIS2 Audit Schedule.docx
NIS2 Audits Procedure.docx
NIS2 Cybersecurity Operations Policy.docx
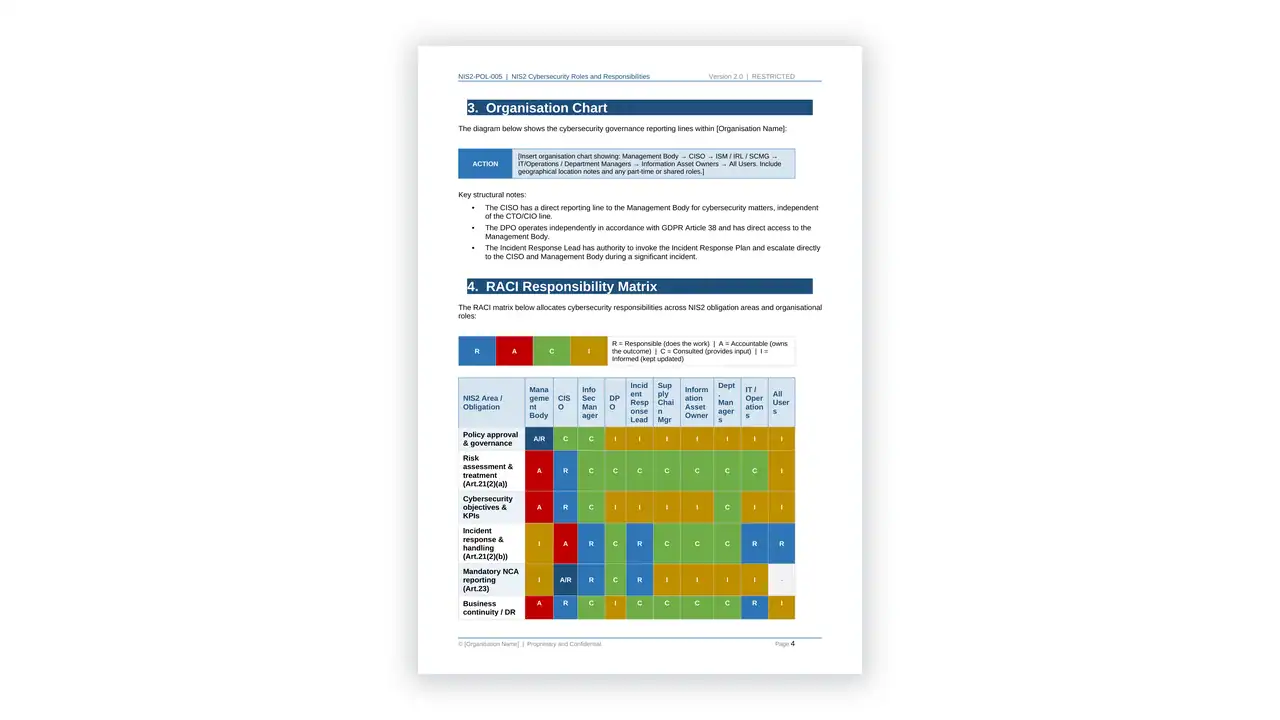
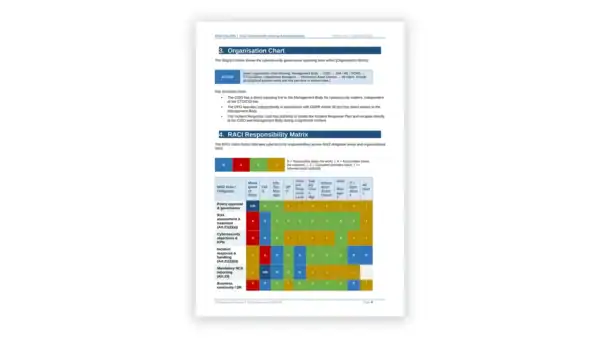
NIS2 Cybersecurity Roles and Responsibilities.docx
NIS2 Early Warning Notification Template.docx
NIS2 Network and Information Systems Security Policy.docx
NIS2 Scope and Registration Document.docx
Organisation of Information Security.docx
Physical Media Transfer Procedure.docx
Physical Security Policy and Design Standard.docx
Pre-Employment Personnel Security Screening Checklist.docx
Project Management Security Policy.docx
Recruitment New Joiner Checklist.docx
Remote Working Policy.docx
Removable Media Management Procedure.docx
Risk Assessment and Treatment.docx
Risk Assessment Report.docx
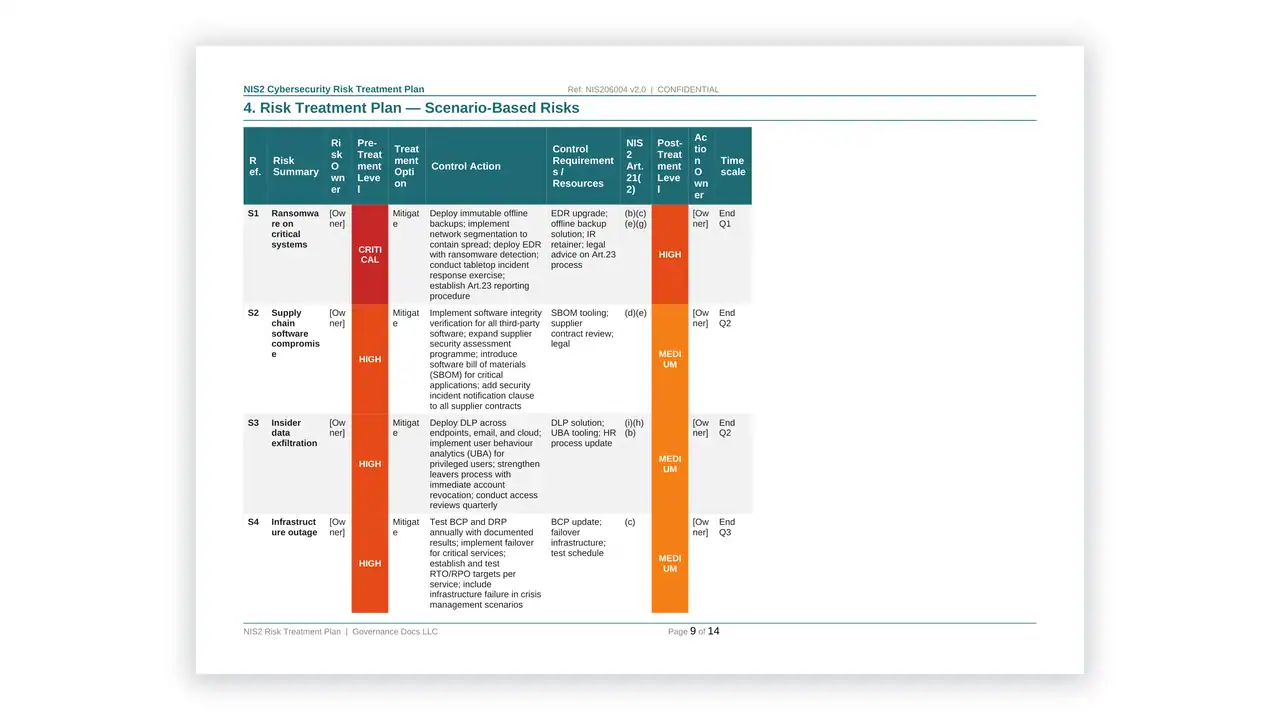
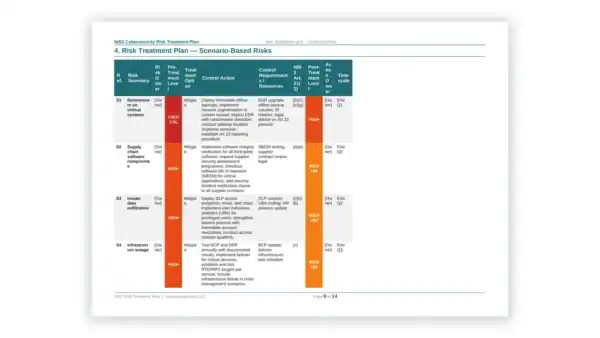
Risk Treatment Plan.docx
Secure Areas Policy.docx
Secure Coding Policy.docx
Secure Data Disposal Policy.docx
Secure Development and Software Supply Chain Policy.docx
Security Event Logging and Monitoring Policy.docx
Segregation of Duties Policy.docx
Significant Incident Handling Procedure.docx
Significant Incident Reporting Form.docx
Stakeholder Email Templates.docx
Supply Chain and Third Party Security – Policy_Procedure and Agreement.docx
Supply Chain Third Party Risk Assessment Form.docx
Technical Briefing on Security Roles and Responsibilities Matrix.docx
Threat Intelligence Policy.docx
Vendor Access Procedure.docx
Vulnerability Management Policy and Procedure.docx
Web Filtering Policy.docx
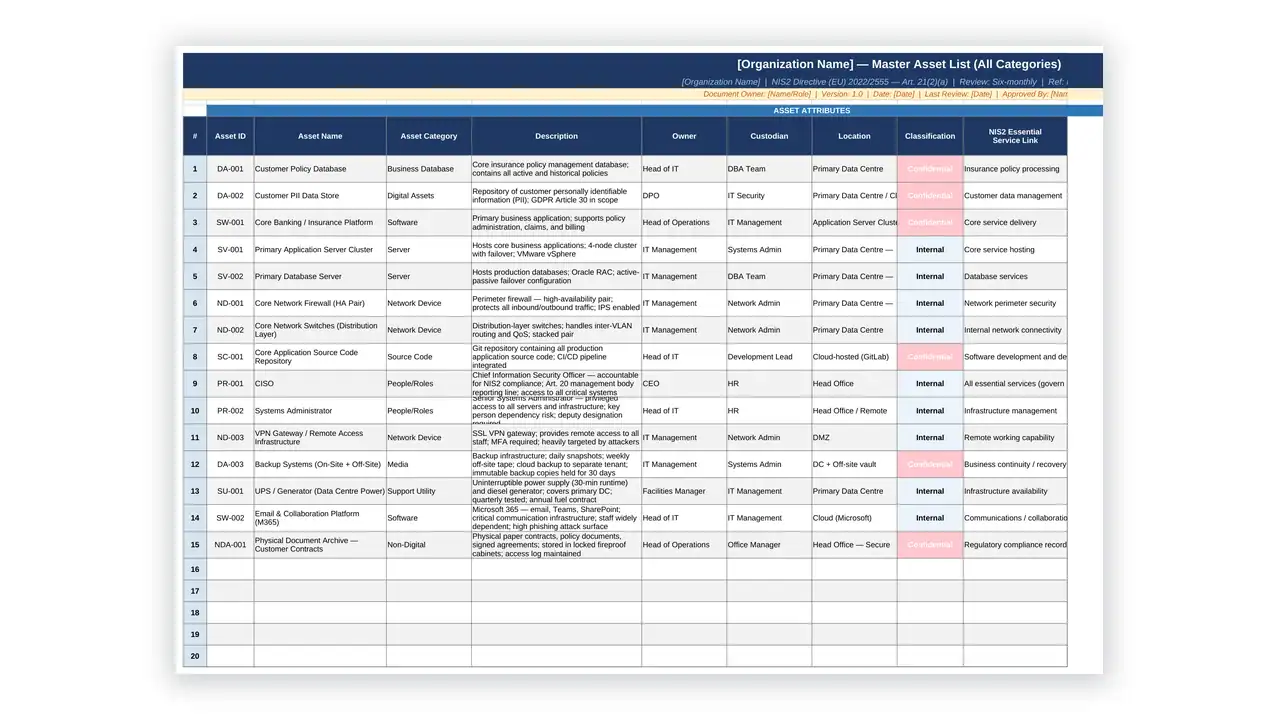
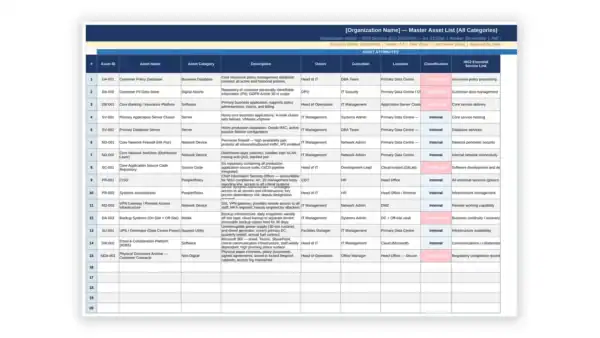
Asset Register.xlsx
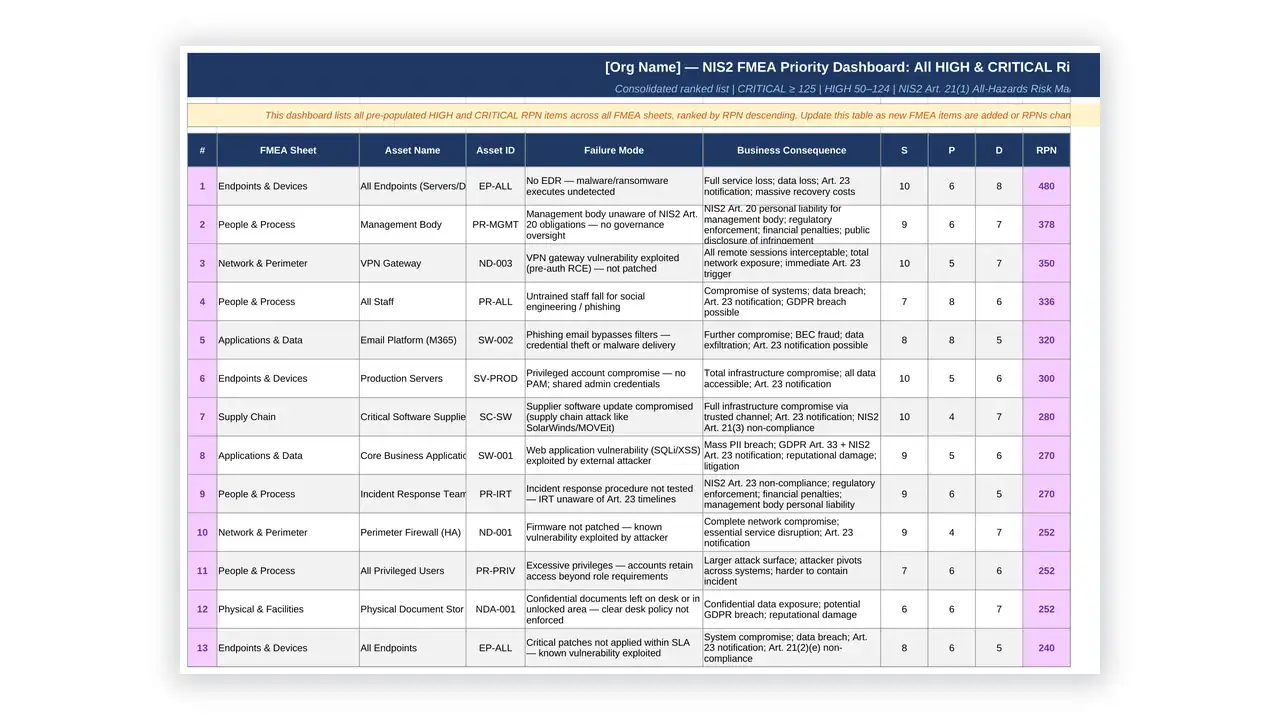
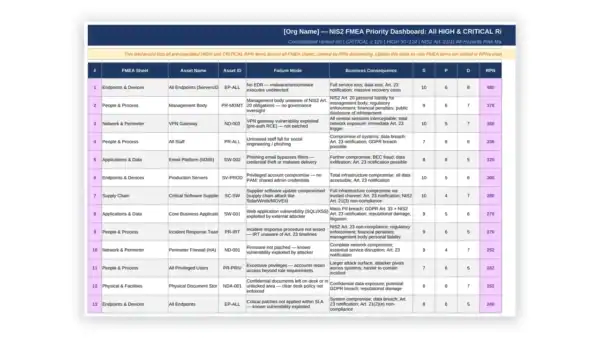
Cybersecurity FMEA Workbook.xlsx
Information Classification Matrix.xlsx
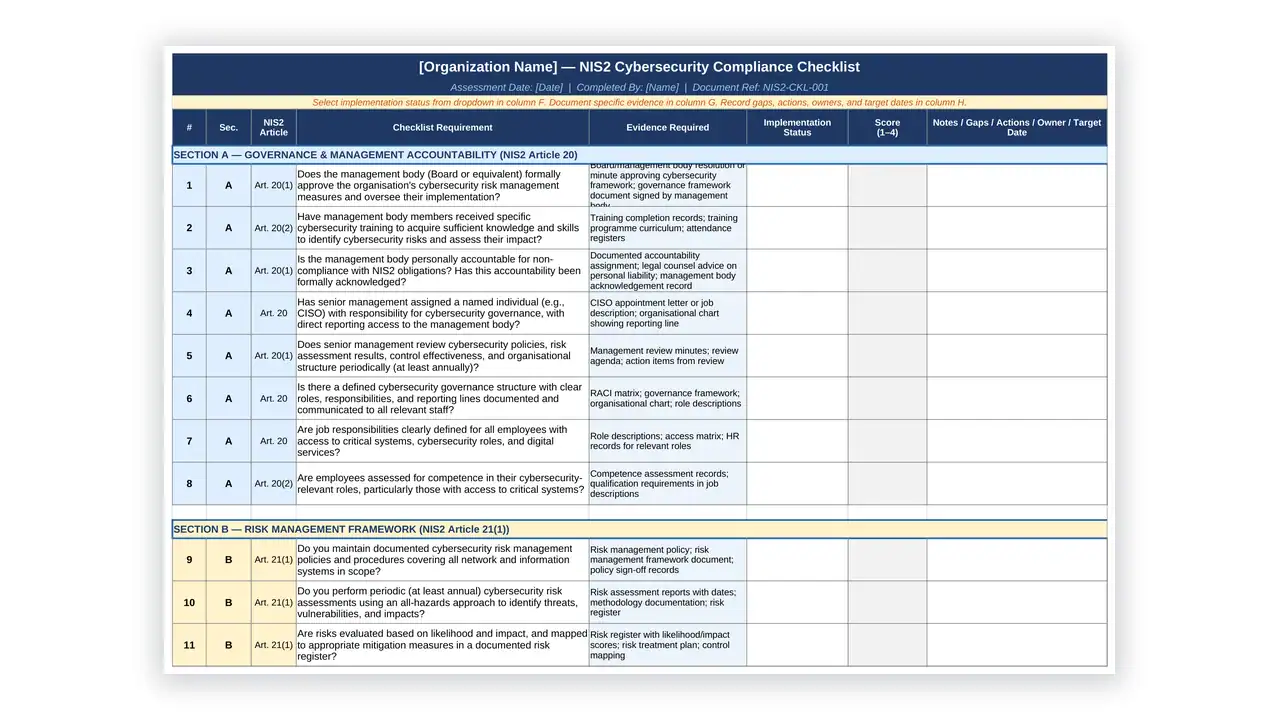
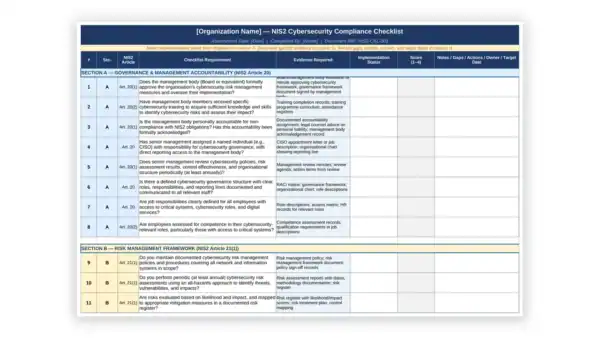
NIS2 Checklist.xlsx
NIS2 Information Risk Register.xlsx
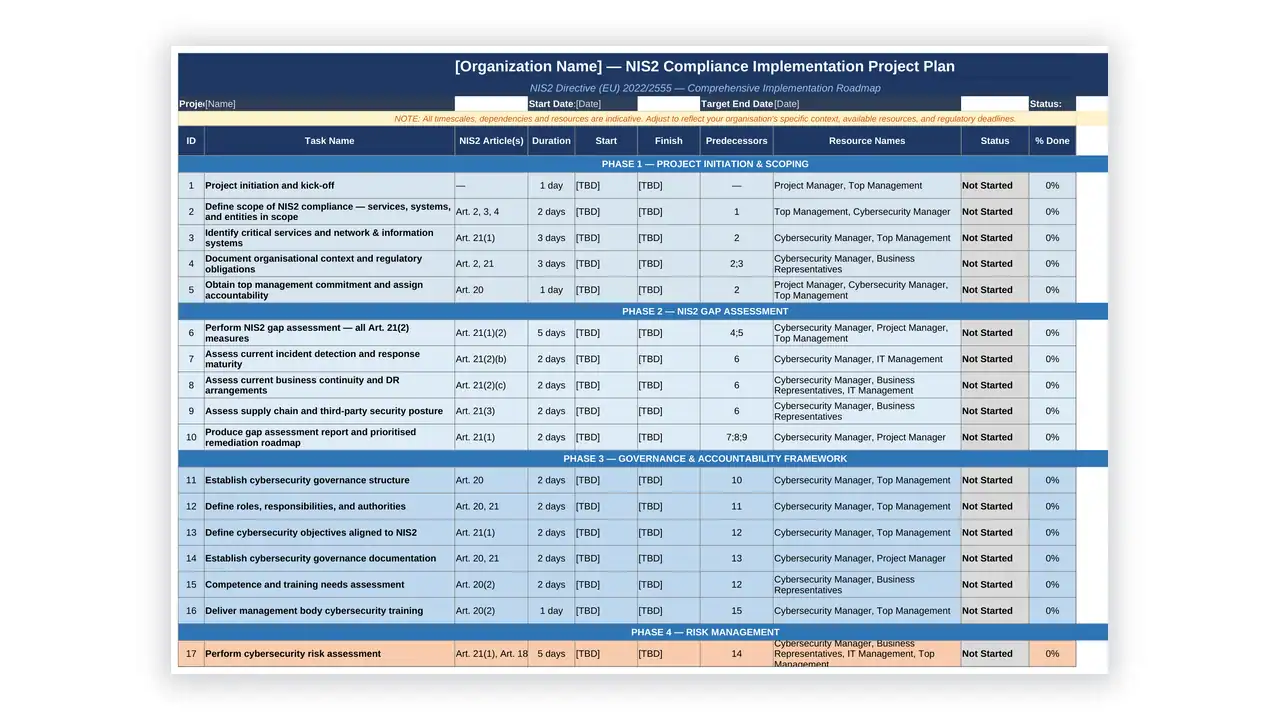
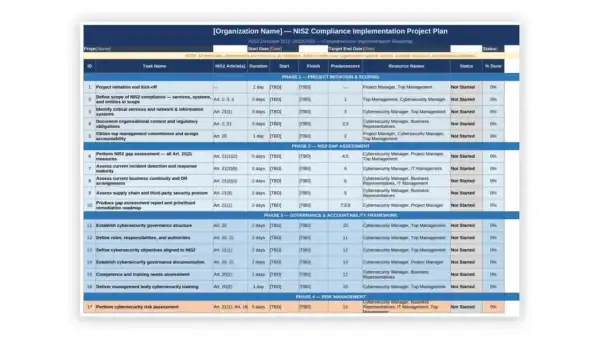
NIS2 Project Plan.xlsx
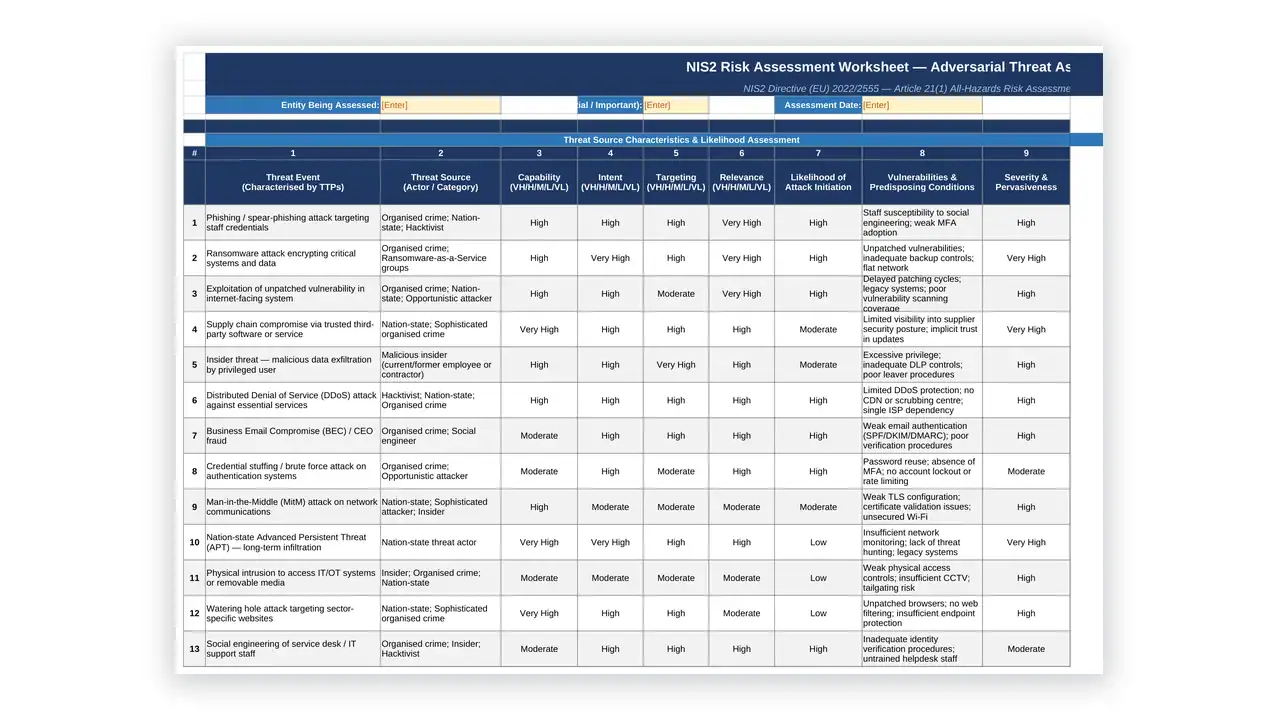
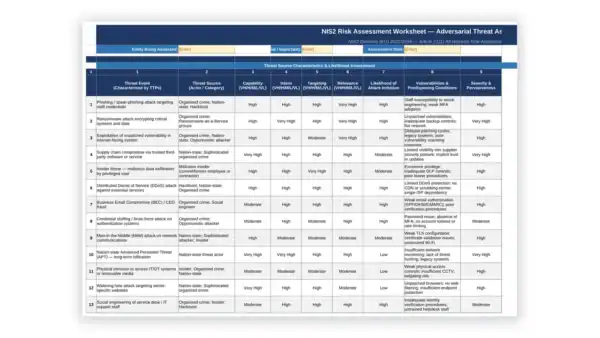
NIS2 Risk Assessment Worksheet.xlsx
All documents of this Toolkit are developed based on The NIS 2 Directive
Article 3 of Directive (EU) 2022/2555 divides everyone in scope into two categories, and which one you fall into changes how you are supervised rather than what you have to do.
Both categories owe the same Article 21 risk-management measures and the same Article 23 reporting. Enforcement is what differs. Essential entities face proactive supervision under Article 32, including regular targeted security audits and random checks. Important entities are supervised after the fact under Article 33, when an authority has evidence or an indication of non-compliance. The fine ceilings differ as well: at least EUR 10 million or 2% of total worldwide annual turnover for essential entities, whichever is higher, against at least EUR 7 million or 1.4% for important entities (Article 34). The NIS2 Toolkit does not make the classification for you, but its scope and registration document is where you record which category you fall into and the reasoning behind it.
Article 21(2) sets out ten areas that every in-scope entity must cover on an all-hazards basis: policies on risk analysis and information system security; incident handling; business continuity, including backup management, disaster recovery and crisis management; supply chain security; security in acquisition, development and maintenance, including vulnerability handling and disclosure; policies and procedures to assess whether the measures are effective; basic cyber hygiene practices and cybersecurity training; cryptography and, where appropriate, encryption; human resources security, access control policies and asset management; and multi-factor or continuous authentication with secured voice, video, text and emergency communications where appropriate. Every one of the ten has documentation behind it in this NIS2 Toolkit.
A significant incident runs to three deadlines anchored to two different events.
The NIS2 Toolkit’s significant incident reporting form is structured around these three submissions, so the 24-hour, 72-hour and final positions are captured as separate records rather than as one document revised in place.
Article 20 places the duty on the board rather than on the security function alone. Management bodies must approve the cybersecurity risk-management measures taken to comply with Article 21, oversee their implementation, and can be held liable for the entity’s infringements of that Article. Members of the management body are also required to follow training themselves. Both obligations produce records a supervisor can ask for, and this NIS2 Toolkit includes the approval, governance and training documentation to evidence them.
One practical point on scope: Member States had to adopt and publish their transposing measures by 17 October 2024 and apply them from 18 October 2024. The law that binds you is your Member State’s implementation, so national thresholds, registration duties and reporting channels should be checked against it rather than against the Directive alone. The NIS2 Toolkit is written to the Directive itself, which is the common denominator across the national implementations.
Implementing for clients? The Consultant Package bundles 70 toolkits — 6,100+ editable templates — under one firm-wide licence that covers unlimited client engagements. $1,399 one-time.
Sorry, no reviews match your current selections
 NIS2 Toolkit - 75+ Comprehensive Templates$99.00


Same as for the ISO 27001 toolkit, I have not got a chance to use it yet but once I do, I will be glade to comment on it. Regards
A practical and well organized toolkit that makes cybersecurity compliance much easier to handle.